


Pinned Tweet
My talk, Python for Threat Intelligence, is now available to watch on YouTube. Check it out if you want a look how my team leverages Python for our day-to-day analysis, some of the packages we use, and how we approach development in general. youtube.com/watch?v=Zf38qnca…

Aaron Stephens retweeted
"The previous update (October 22 16:18 UTC) reported that Sophos observed successful exploitation of PHP2Shell in customer environments. Upon further analysis, we are correcting that assessment as Sophos customer telemetry shows scanning and a small number of failed exploitation attempts. As of this update, there is no evidence of a successful compromise due to these vulnerabilities." sophos.com/en-us/blog/proof-…

Aaron Stephens retweeted

As just announced in the @UN First Committee, Russia’s COSMOS 2612 military satellite has been exhibiting threatening behavior by intentionally maneuvering dangerously close to a commercial satellite, behaviors consistent with on-orbit weapons operations. This violates long-established safety thresholds in low Earth orbit. The United States will continue to secure and defend American vital national security interests in, from, and to space.

Aaron Stephens retweeted
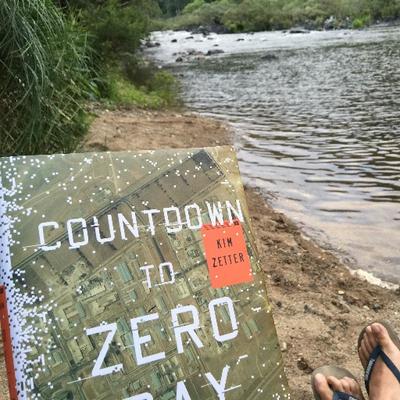
Despite claims by Trezor today that none of its crypto devices have been compromised - unlike the devices of Ledger, its competitor - hardware hacker @joegrand says he found implants in two Trezor devices and reported this to Trezor in August. My story: zetter-zeroday.com/trezor-wa…

Aaron Stephens retweeted

All intel people want more data, though imo many of these wants come with subtle naïvety, as if some new data will automatically deliver results. Access & data collection will not miraculously increase visibility into threat actors, nor will it magically unlock security value.
Aaron Stephens retweeted

Every other law enforcement agency is playing checkers while the U.S. Postal Inspection Service (@USPIS_HQ ) investigators are playing chess.

Aaron Stephens retweeted

Department of Energy Employee Arrested in Washington State on Charges of Attempted Material Support to Houthis ow.ly/rr8I50ZU86L

ALT News release | October 1, 2026 | Department of Energy Employee Arrested in Washington State on Charges of Attempted Material Support to Houthis

ALT SAC Herrington: “Protecting the American people is the FBI’s mission and the cornerstone of everything we do. We deeply value the partnership of the Department of Energy and the law enforcement agencies working with us on Joint Terrorism Task Forces throughout Washington, as well as the tireless efforts of our investigators to develop this case. Their work is a remarkable example of our shared commitment to protecting the state of Washington...”
Aaron Stephens retweeted

FastAPI now has built-in OpenTelemetry support, natively 📈
No extra code needed.
See how your app behaves in production.
Go and upgrade to "fastapi[standard]" version 0.142.2 ⬆️
Read the docs: fastapi.tiangolo.com/advance…

Aaron Stephens retweeted
I think that all of the focus on exploit specific detection is a losing strategy in general. Post-exploitation detection is more resilient and if you're strong there, you will catch intrusions regardless of the CVE number. The overwhelming majority of in the wild zero day exploitation I have encountered in my life has been identified by detecting post-exploitation behavior.
Aaron Stephens retweeted

#flareon13 And we're off to the races. Data centers everywhere just got a little warmer. Doesn't stop people from entering "flare" as the first flag though
Aaron Stephens retweeted
IFWI, but also there needs to be longer sentences. Two years for involvement with RYUK is a joke.

SIX CYBERCRIMINALS EXTRADITED TO THE UNITED STATES.
Operation Riptide sent a message every cybercriminal targeting Americans needs to hear:
There is NO safe harbor.
The FBI and our international partners will identify you. We will locate you. And no matter where in the world you try to hide, we will work to bring you back to the United States to face justice.
Borders will not protect you. Distance will not save you.
We will find you.
—DKP 🇺🇸

Aaron Stephens retweeted

Two Swedes Detained in Finland on Suspicion of Espionage
militarnyi.com/en/news/two-s…

do us all a favor and stop using cti labels you didn’t define. they are rarely (never) published with enough transparency to use in your own analysis.


Aaron Stephens retweeted
Hopefully you listened when I said get your resumes ready. @GreyNoiseIO is hiring Threat Researchers who will develop and exploit first, second, and third-party access and sources to produce cyber threat intelligence that practitioners will use to detect, disrupt, and impose cost on adversaries. job-boards.greenhouse.io/gre…

Aaron Stephens retweeted

Ten years a former senior Pentagon official told me what I thought was an apocryphal story: American spies had saved Steve Jobs, and by extension, Apple.
Tracking it down became a personal obsession and the starting point for my new book, Valley of Death. I'm thrilled to share the excerpt about Jobs and the CIA published today in the @WSJ.
wsj.com/tech/steve-jobs-appl…

Aaron Stephens retweeted

Source: He didn't remove the metadata.
He also didn't even change the title, which suggests Curaleaf and TheraTrue are exploring a business deal.

Aaron Stephens retweeted

We’re thrilled to welcome @ImposeCost to GreyNoise as our new SVP of Adversary Operations ⚡
With deep experience spanning Google Threat Intelligence Group, Mandiant, and U.S. Marine Corps Forces Cyberspace Command, Andrew joins GreyNoise with a clear mission: build on our early visibility into edge device exploitation and ultimately help defenders move from retroactive awareness to proactive disruption.
🔗greynoise.io/blog/new-svp-ad…
Welcome to GreyNoise, Andrew!

Aaron Stephens retweeted

Wake up babe the new @WhiteHouse cyber privateering construct just dropped whitehouse.gov/presidential-…

Aaron Stephens retweeted
When I was still in government, I attended a conference and heard Kevin Mandia speak. I made the decision that I wanted to work for his company, and so that is what I did. I joined an elite team and we earned it every day. I have always been in awe of not just my teammates but also just how many former members went on to do great things after their time at Mandiant. It is with a full heart and way less pigmentation in my hair that I announce that the time has come for me to do just that. I want to thank my fellow Mandiants and Googlers, current and former, many who are actually out here as Mandiant veterans already doing great things in the community and industry. After much deliberation with great organizations and people, I have found my next team. That will be a follow up announcement.
Let's get after it.
Aaron Stephens retweeted

18 years ago today, Dan Kaminsky @dakami disclosed the DNS cache poisoning vulnerability at Black Hat USA 2008, triggering one of the largest coordinated patch efforts in internet history.
Before public disclosure, Dan organized multiple vendors to fix the flaw in secret. Many more legendary stories than could fit here, like how he exposed Sony’s rootkit across more than 568,000 networks and identified critical certificate vulnerabilities.
Dan followed what he cared about and his curiosity.
As Michael Tiffany @kubla put it, “Only Dan thought, ‘I could fix the human eye in software.’” He built DanKam, an augmented-reality app that helped colorblind people see color. Michael hosted Dan while he built the first version and described watching a colorblind houseguest sit at the kitchen table, “crying tears of joy seeing red for the first time.”
His mother, Trudy Maurer, may have said it best when she accepted his Lifetime Achievement Award at the 2025 Difference Makers. “Daniel was the catalyst for many achievements across the vast internet spectrum, and I believe Dan truly represented the intersection of technology and humanity.”
@dotMudge, who presented the award, said: “The Lifetime Achievement Award isn’t about what you achieve in your lifetime. That’s part of it. It’s about how many people you influence and bring in and then take it further.”
We lost Dan too early from diabetic ketoacidosis in April 2021 at age 42.
Some of you are hearing the name Dan Kaminsky for the first time.
The coordinated, community-first spirit Dan modeled is the bar.
If you're in Vegas this week, you're walking the streets that the legends of security who came before you walked, when they also had no idea what they were doing, facing problems nobody had solved before.
They had to figure it out as they went. Just like you're going to do.
Thanks to those who contributed to this tribute video: Jeff Moss @thedarktangent, @paulvixie, @gadievron, Lena Smart, Derek Hinch and the many others who shared here.