
@OWASP #IoT & #EmbeddedAppSec Project leader | Co-Chair: @CloudSA IoTWG | Author & Tech Reviewer| 🍕 CISO @Cisco
Los Angeles
Joined December 2013
- Tweets2K
- Following2.1K
- Followers2.2K
- Likes2.6K




A-a-ron Guzman retweeted

We want to drop a thanks to @cisco taking on Gold Sponsorship of the BBV this year! It's support like yours that enables us to host this epic Village and without partners like you we simply couldn't do it.
#BugBountyVillage #DEFCON
A-a-ron Guzman retweeted
Before protecting the wireless IoT in our homes, businesses, and global events, he was a hacker cold-emailing companies.
Now a CISO, Aaron shows hackers how to get the biggest return on Cisco's program.
youtu.be/-FMwi_V6XeY

A-a-ron Guzman retweeted
Tracing the evolution of vuln disclosure from pre-bounty days to modern large-scale programs, @scriptingxss highlights the growing complexity of managing submissions, scaling security operations & maintaining strong relationships with the researchers.
youtu.be/-FMwi_V6XeY

A-a-ron Guzman retweeted

⚒️ Tune in to Hardware Vulnerabilities: Lessons from the Vendor Frontlines, where vendors spill the truth and the hardware spills…well, vulnerabilities. #hw_ioNL2025 is wide awake now!
On Panel: Adam Laurie, Aaron Guzmann and Sebastian Paul Avarvarei.
👉hardwear.io/netherlands-2025…

A-a-ron Guzman retweeted
When hardware sneezes, the whole system catches a cold🤧
Join Aaron Guzmann, Adam Laurie & Sebastian Avarvarei at #hw_ioNL2025 as they share frontline vendor stories—and reveal what never to do when your chips start behaving strangely
👉hardwear.io/netherlands-2025…
#Panel #hardware

A-a-ron Guzman retweeted
Here’s the second half of our Friday lineup at @DEFCON – and it’s just as stacked. 🔥
@DaneSherrets, @Shlibness, @mgianarakis, Jordan Macey, @CryptoGangsta, @scriptingxss, @nytr0gen_, @erbbysam, and @BrunoModificato.
See you there. 👀 #BugBounty

A-a-ron Guzman retweeted
Don't miss "To Pay or Not to Pay? The Battle Between Bug Bounty & Vulnerability Disclosure Programs" by Aaron Guzman (@scriptingxss) on Friday, August 8 at 04:00 PM inside the Village.
Read more at bugbountydefcon.com/agenda
#BugBounty #DEFCON33
A-a-ron Guzman retweeted
We’re excited to announce that Aaron Guzman (@scriptingxss) will be speaking at the Bug Bounty Village at DEF CON 33!
Stay tuned for more details on their talk, you won’t want to miss it.
#BugBounty #DEFCON #BBV #BugBountyVillage
A-a-ron Guzman retweeted

Strengthen Enterprise Security Through Collaboration at Planet Cyber Sec AppSec SoCal!
Join Omar Minawi, @scriptingxss, Shelby Pace and Natalya Krecker for "How to Win Friends and Influence Trust: Reducing API AuthZ Risks Through Collaborative Defenses."
Discover:
- Power of security and API team collaboration
- Leveraging security research community
- Overcoming API testing challenges
- Collaborative defense strategies
Gain insights to mitigate API AuthZ risks and promote a security-centric culture.
planetcybersec.com/061224-co…
#PlanetCyberSec #AppSecSoCal #AppSec #CyberSecurity #APIAuthZRisks #CollaborativeDefenses

A-a-ron Guzman retweeted
Introductions are happening for the State of {Absolute} AppSec panel at @LASCONATX. Joining @cktricky and @sethlaw are @ejcx_ , @wickett, and @scriptingxss. Hop in to the discussion here: youtube.com/watch?v=g5JJ07jk…

A-a-ron Guzman retweeted

Aaron Guzman's insightful talk helps us discover OWASP's IoT Security Testing Guide for effective penetration tests and dive into robust methodologies and tools. #PlanetCyberSec #AppSecSoCal #AppSec #infosec
#IoTSecurity
@scriptingxss

A-a-ron Guzman retweeted

📖 Penetration Testing Findings Repository
A collection of Active Directory, phishing, mobile technology, system, service, web application, and wireless technology weaknesses that may be discovered during a penetration test
By @CISAgov
#cybersecurity
github.com/cisagov/pen-testi…

A-a-ron Guzman retweeted
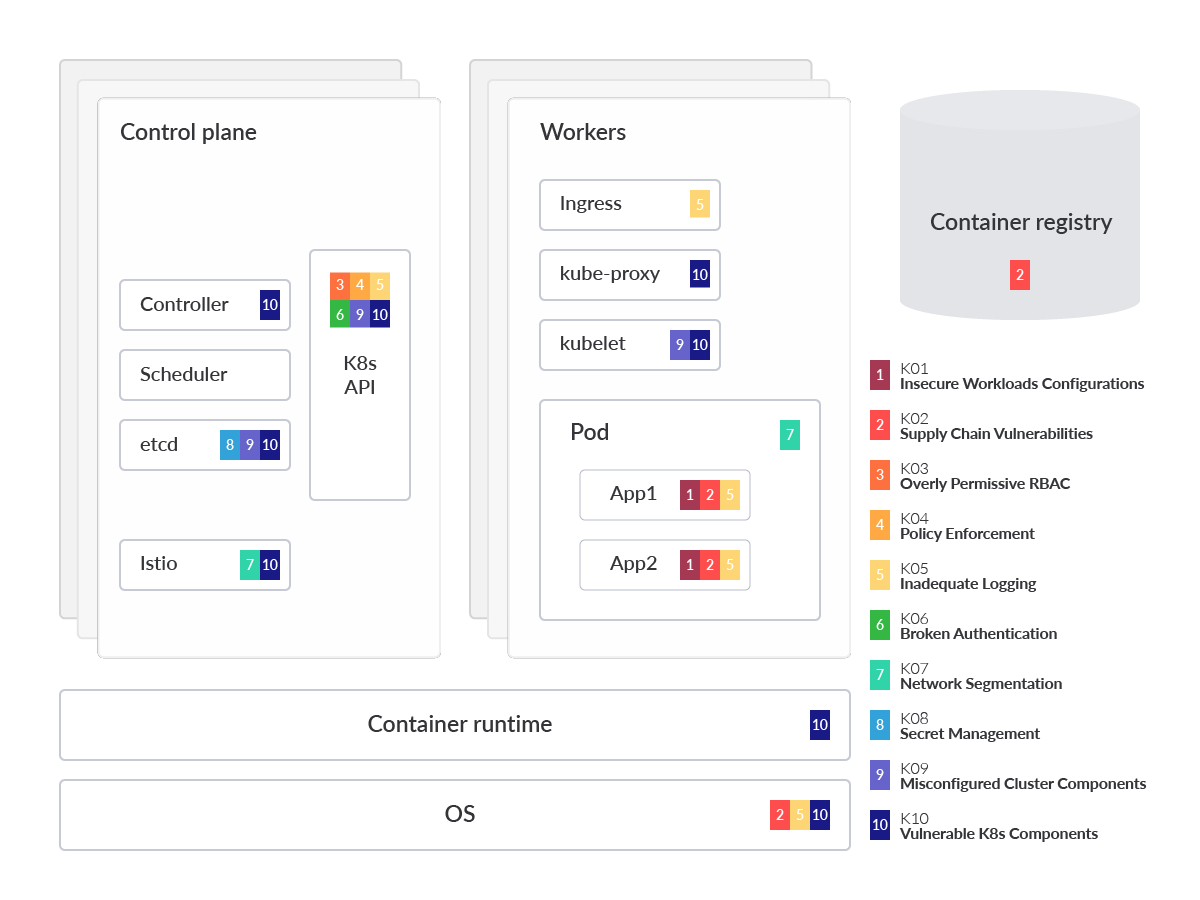
🗒️ @OWASP Kubernetes Top 10
Broken down into 3 categories in order of likelihood:
1️⃣ Misconfigurations
2️⃣ Lack of visibility
3️⃣ Vulnerability management
Risks, mitigations, and lots of relevant tools
By @sysdig
sysdig.com/blog/top-owasp-ku…
A-a-ron Guzman retweeted

30 cybersecurity search engines for researchers:
1. Dehashed—View leaked credentials.
2. SecurityTrails—Extensive DNS data.
3. DorkSearch—Really fast Google dorking.
4. ExploitDB—Archive of various exploits.
5. ZoomEye—Gather information about targets.
A-a-ron Guzman retweeted
✅ How to *actually* roll out YubiKeys/WebAuthN
Industry advice is to "just do it"
But it's actually really hard in practice
8 resources on lessons learned from companies who've done it 🧵
A-a-ron Guzman retweeted
🦀 Memory Safe Languages in Android 13
To date, 0 memory safety vulns in Android’s Rust code
Historical vulnerability density is >1/kLOC in C/C++ components → Rust has already prevented 100s of vulns
By @jeffvanderstoep
security.googleblog.com/2022…


A-a-ron Guzman retweeted
4) IoT Penetration Testing Cookbook by @scriptingxss and @adi1391
Get Book: amzn.to/3vfrqqy
For more visit: cybermaterial.com/iot/
👉 Follow @CyberMat3rial
#cybermaterial #cybersecurity #infosec #iot #books #cyberbooks


A-a-ron Guzman retweeted

Nice repository with a collection of resources related to firmware security
github.com/PreOS-Security/aw…
#iot #embedded #firmware #infosec #cybersecurity

A-a-ron Guzman retweeted

O yea ... we did it! #Metasploit integration into a #firmware #security scanner goes the next level with EMBA - github.com/e-m-b-a/emba

