




Excited to see the continued development of @boardyai
Network effects are one of the few durable moats as things become easier to build; I think Boardy has a good shot at getting this right
This quoted post is unavailable.
Today we’re opening @FindemAi Studio to everyone.
I’ve spent the last 15 years on both sides of hiring: building a recruiting agency where customers paid us to find people, then building software that gave them tools to do it themselves.
There’s a lot of room between those two options.
A leader hiring their first VP of Engineering wants to meet candidates, run interviews, and make the final call. But they’d gladly hand off the hours of research it takes to find people who’ve built teams at their stage and in their domain.
That’s the idea behind Findem Studio: hand off a task, such as an executive market map, and get finished work back with the method and evidence attached. You spend your time checking the work and making decisions, rather than doing every step yourself.
You can also connect Findem through MCP if you already work in a surface like Claude, ChatGPT, Copilot, or Gemini.
What piece of hiring work would you hand off first?
Reply or DM me, and I’ll send you free credits to try it 🚀
Evan Walden retweeted

Today we’re announcing the General Availability of Agent SSO, and we’re including it in our core SSO offering.
SSO transformed how people move across applications, making access seamless for users and centralizing identity and control for IT. AI agents need the same thing.
Today, connecting agents is a mess of static API keys, fragmented integrations, and endless user consent prompts. But Agent SSO changes that. Powered by the open Cross App Access (XAA) standard, it enables agents to be registered as first-class identities. For IT, it means centralized visibility and least-privilege policy. For users, it means their AI agents can seamlessly connect across enterprise apps without interrupting their flow.
This makes a lot of sense

you can't put the same designer, PM, and engineer on five projects at once.
unless they're @bot s.
Grok Bot v0.23.0 now has Channels. same team, different projects, same time.

Just did an expense report with Codex driving the bus and it was downright pleasant.
- Scanned email and credit card statement for transactions
- Upload receipt pics from camera roll
- Rippling expense report with browser-use
Thank you @OpenAI @ChatGPTapp 😭

ok this is the new standard for demo videos. one screen recording, one app, 20 minutes. out comes 3d animations, ai voiceover, music, callouts. the just-post-the-loom era is genuinely over.
Started playing with @TownAI and am pretty blown away -- unlocks Openclaw/Hermes-like capabilities without the configuration issues, safety anxiety, time investment, etc.
Onboarding was gorgeous and "just worked" out of the gate 🥲
What a time to be on the internet!
Like I thought to myself...I should ask these guys if they have a desktop app, then clicked this menu and got...literally everything.

Evan Walden retweeted

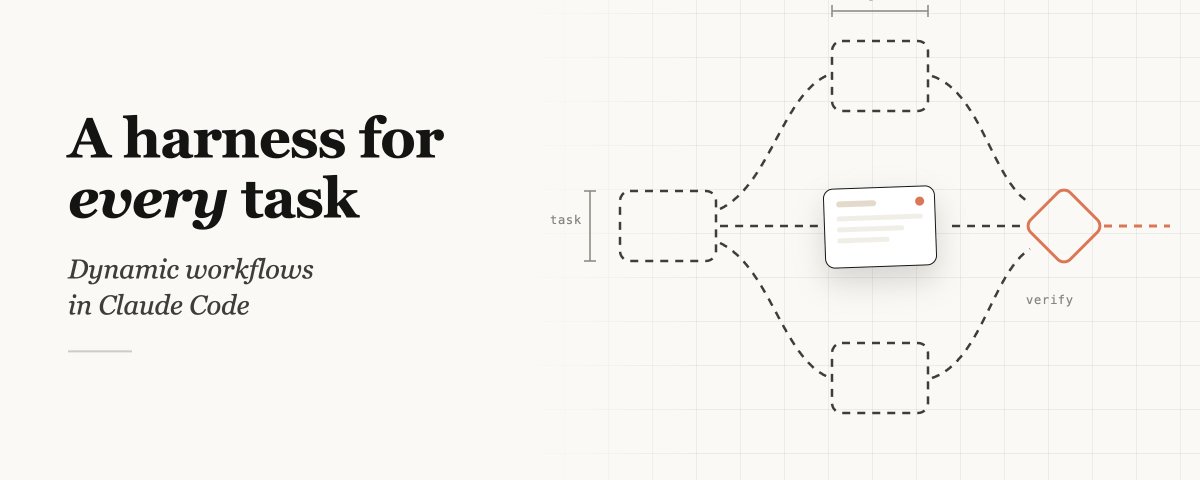
Workflows are the biggest upgrade to Claude Code’s capabilities since skills and subagents.
I dove deep into it with @sidbid to figure out best practices, examples and more. I’m particularly excited about the non-technical tasks it enables for Claude Code.

a claude /slides skill that turns a rough outline into a polished html deck, directly from the terminal. love how simple this is.
Evan Walden retweeted

To get good animations from an AI you need to get good at telling it what you want:
- "stagger this list of items"
- "make this animation direction-aware"
- "spacial consistency", "crossfade", "layout animation",
I made a motion vocabulary for this:
animations.dev/vocabulary
a claude /slides skill that turns a rough outline into a polished html deck, directly from the terminal. love how simple this is.


Late to the AI presentation party, but @Pitch has always had the best taste in the category, and there's real second-mover advantage in watching everyone else ship the wrong thing first. Excited to see where this goes. xitter.cf/christianreber/status/…

We’re entering a new era for presentation software. Not slide editors. Presentation operating systems.
At @Pitch , we’ve always cared deeply about craft and interface quality. Bringing AI into professional presentation software – where every detail matters – was incredibly hard.
Today feels like a breakthrough. Pitch Agent is launching. 🌟
And this is just the beginning of Pitch becoming an AI-native software company.
pitch.com
Evan Walden retweeted

Introducing Roughdraft!
A new open source project designed to make collaboration with agents better.
The idea is to bring commenting and suggested changes to markdown (e.g. plan docs) in a nice interface.
Free, local, etc.
👉 roughdraft.md 👈
Evan Walden retweeted

Team shipped a Codex Security plugin with 5 AppSec workflows:
> Security Scan
Scans PRs, commits, branches, patches, folders, or full repos. Runs the full pipeline end-to-end
> Threat Model
Maps the repo: assets, trust boundaries, attacker inputs, invariants, and failure modes
> Finding Discovery
Finds plausible vulns: authz bypass, SSRF, path traversal, injection, cross-tenant leaks, sandbox escapes, dangerous sinks, etc
> Validation
Separates signal from noise. Uses PoCs, tests, debugger traces, ASan/valgrind, realistic repros, or static tracing
> Attack Path Analysis
Turns findings into attacker stories: reachability, counterevidence, impact, severity, and whether it should actually be reported
It’s a packaged security review for your projects:
threat model → discovery → validation → attack path → report
Try it out today!!


