

Building trust layer for hardware infrastructure (yes AI infra as well) at @eclypsium. @CHIPSEC. Former @intel, @IntelSecurity, @McAfee
Joined April 2010
- Tweets2.9K
- Following1.2K
- Followers4K
- Likes1.6K




Yuriy Bulygin retweeted

The latest InfraTrust Pulse is out and September’s data reminds us that CVSS alone isn’t a patch strategy. Reachability, active exploitation, device role, inherited components, and firmware exposure all matter when deciding what gets attention first. na2.hubs.ly/H07-9WC0

Hardware is the new cloud… oh wait

Before AI:
- hardware is hard
- teams > solo founders
- technical founders only
- PhDs build tech in search of a problem
- hot SaaS startups get 100x ARR multiples
After AI:
- hardware is the only thing AI can't build
- solo founders are 100x engineers
- anyone can build
- PhDs building AI infra name their price
- SaaSpocalypse
Am I missing anything?
Agents taking over GPUs, BMCs, DPUs in the data centers and we are in for a rough ride…

Yuriy Bulygin retweeted

agents will find & repurpose attack surfaces humans overlook ie. Artifactory in @OpenAI - @huggingface incident
Neoclouds have an even less visible hardware layer: firmware, BMCs, GPUs and network devices.
@eclypsium already protects some of the largest neoclouds.. but so many still fly blind cc @c7zero
This is beautiful. DRAM scrambling + C6 save state

New exploit: “xor dword [0xf80c2094], 1<<22”
Unlocks CPU microcode, the platform security processor, system management mode, and every internal processor register, all at once, on 100 million AMD CPUs. As far as I can tell can’t be fixed.
github.com/xoreaxeaxeax/skit…
Yuriy Bulygin retweeted

"Peter Thiel says, you have to be contrarian but right to be an entrepreneur.
So, you have to be comfortable looking stupid for a long time.
When I was calling those banks and saying, "Hey, we're a crypto company. We want to do this," they would hang up on me.
Or I'd go pitch the 30th venture investor and get a no.
Or the thousandth employee we tried to hire or whatever.
We're willing to be misunderstood for a long time.
And then you slowly start to have these breakthroughs.
If you look at Uber, they were fighting for a decade to just be like, yeah, it's actually better and safer than a cab — and the entrenched interests were fighting them.
Or Airbnb with the hotels.
Self-driving cars.
Everything that's truly innovative and breakthrough is going to upset an entrenched incumbent, eventually intersect with the government, and just piss off some segment of the population who are like...
"How dare you question the status quo."
— @brian_armstrong

My conversation with @brian_armstrong, co-founder and CEO of @coinbase and @newlimit.
0:00 Crypto Power in DC
0:25 Market Structure Clarity
1:39 SEC Lawfare Origins
5:49 Suing the Regulator
9:09 Winning the SEC Case
11:11 Long Term Founder Mindset
12:20 Autism and Focus
15:04 Mission First Company Culture
21:10 Rebuilding From Scratch
23:05 Follow Your Nose
25:20 From Side Hustles to Coinbase
30:07 Argentina and Bitcoin Spark
32:33 Airbnb to Coinbase Nights
36:25 Finding a Co-founder
37:35 YC Without a Co-founder
38:41 Finding the Perfect Partner
40:18 Losing Money Per Trade
41:23 Support Backlog Chaos
43:29 Banking and Compliance Gauntlet
47:47 Raising Fast to Survive
51:36 Mission Values and Inspiration
57:54 Hiring for Spikes
1:02:14 Centralized vs Decentralized
1:05:51 From Bitcoin Wedge to Super App
1:07:59 How Coinbase Runs Today
1:11:00 Decision Speed and Risk
1:12:43 Internal Venture Bets
1:14:46 Funding Ideas Internally
1:15:18 Coinbase Marketing Experiments
1:16:56 Internet Native Shareholder Updates
1:21:58 Media Diet and Going Direct
1:26:47 Building a New Industry
1:31:44 Starting New Limit Longevity
1:36:17 CEO Stress and Routines
1:40:59 AI Agents at Coinbase
1:44:35 Base App Explained
1:46:47 Other Bets and SEZs
1:49:21 Closing Thanks
Includes paid partnerships.
Yuriy Bulygin retweeted

I've got some really cool gift recently... UEFI Petya PoC: youtube.com/watch?v=dMOiypRX… 😁
Yuriy Bulygin retweeted

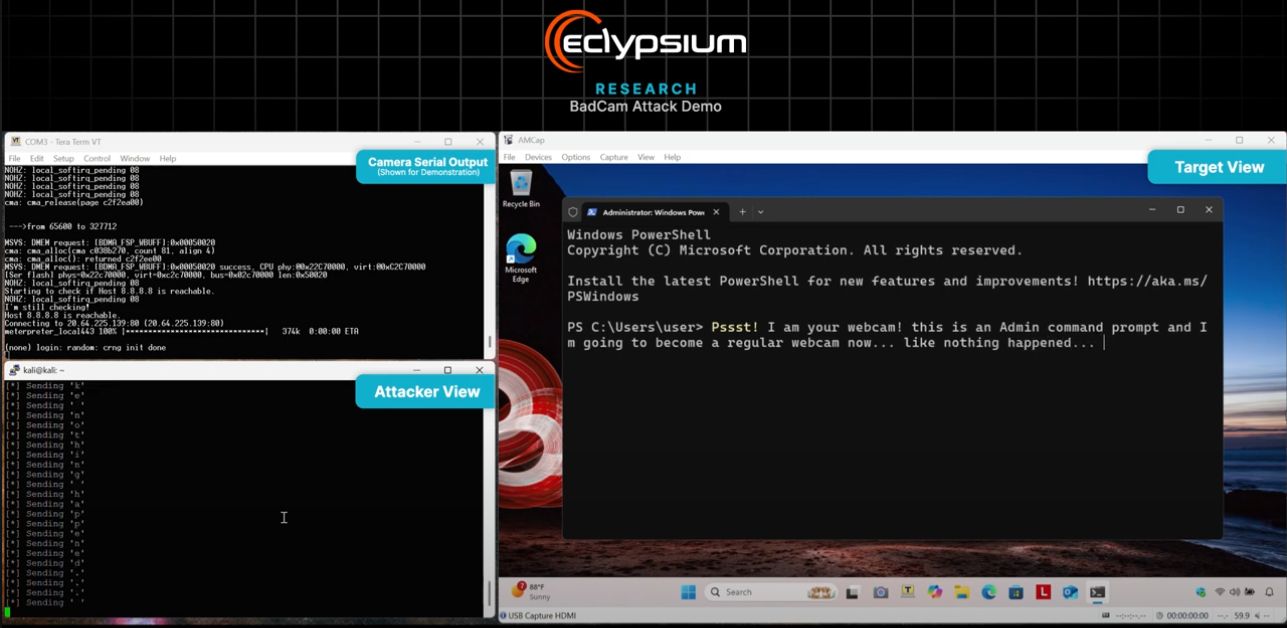
The BadCAM research has been published! Why is this significant? Attackers can now weaponize connected USB peripherals that run Linux and do not validate firmware signatures.
Yuriy Bulygin retweeted

If you use llamafile, llama.cpp, llama-cpp-python, Oobabooga, LMStudio or any other software that exposes llama.cpp grammar sampling, I found a few remotely exploitable bugs triggered through a single web request that got patched today. More to come from my work at @Eclypsium

Yuriy Bulygin retweeted

found a critical bug that exists in every Linux boot loader signed in the past decade 🥰 github.com/rhboot/shim/commi…


Added #downfall detection via content update


Yuriy Bulygin retweeted

I found a remote(-ish) memory corruption bug in Intel's BIOS. Bluetooth HID Report parsing is yucky
research.nccgroup.com/2023/0…
Yuriy Bulygin retweeted
Hundreds of models of Gigabyte motherboards, used in gaming and other high-performance computers, have a backdoor in their firmware that invisibly downloads code to the machine at startup—and does so insecurely, leaving the feature open to abuse. wired.com/story/gigabyte-mot…

Yuriy Bulygin retweeted
Eclypsium analysis found a backdoor in Gigabyte systems implementing intentional functionality during system startup. Due to significant #supplychainrisk, we're disclosing this info & defensive strategies on an accelerated timeline >> bit.ly/3N6axIA
#supplychainsecurity
Yuriy Bulygin retweeted
Attention anyone having an MSI motherboard or computer. MSI just said they were hacked and attackers might have tried modifying BIOS and software updates.
Disable all updates from MSI for the time being
pcmag.com/news/msi-confirms-…

Such a loss :(

It is with profound sadness that we mourn the loss of our friend and mentor, @aloria. Kelly had an indomitable spirit, and our world is a bit darker without her.

Yuriy Bulygin retweeted
New release: #TinyTracer v2.3 : github.com/hasherezade/tiny_… - with improved syscalls tracing support - now syscalls are automatically mapped to corresponding functions names
