
Sr Manager, APT Threat Research @Proofpoint
Montréal, Québec
Joined March 2009
- Tweets975
- Following842
- Followers1.7K
- Likes1.9K



Pinned Tweet
Crunching reports by so many different researchers was a great learning experience. There is a lot of awesome knowledge out there! And to top it off, I got to work alongside the relentless @0xfmz. Mission accomplished!

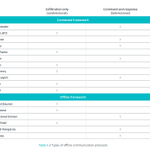
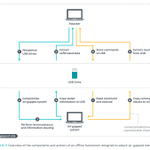
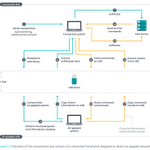
#ESETresearch has published a comprehensive whitepaper comparing all known malware frameworks designed to breach air-gapped networks. Read more: welivesecurity.com/2021/12/0… @adorais @0xfmz 1/7

Alexis Dorais-Joncas (@adorais.bsky.social) retweeted

On August 28th, China-aligned actor TA412 (aka Violet Typhoon) began delivering a Chrome exploit. Within days, 3️⃣ more state-sponsored clusters adopted the same exploit chain.
Our Discarded podcast features the Proofpoint researchers who tracked it all. proofpoint.com/us/podcasts/d…

Alexis Dorais-Joncas (@adorais.bsky.social) retweeted

Happy to announce that I’ll be presenting at State of Statecraft this October! The presentation will be about the investigation of a China-aligned APT group that we call SinisterEye. Read more here👇

BEHOLD: the 🆘 AGENDA is OUT!
VOLUME II features numerous discussions on developments in state-sponsored operations covering digital espionage, cyber/physical sabotage, economic tradecraft, disruption, attribution and dare we say, more?
Agenda 👉 stateofstatecraft.com/agenda
🧵

Alexis Dorais-Joncas (@adorais.bsky.social) retweeted
Heard about those zero days in Chrome and Windows? Well, @markkelly0x found them being used in the SAME exploit kit, proliferating across the APT ecosystem.
Meet BlueMoon exploit kit:
proofpoint.com/us/blog/threa…

Alexis Dorais-Joncas (@adorais.bsky.social) retweeted
#ESETresearch discovered #GuardBreaker - a technique used by 🇷🇺 Russia-aligned UAC-0099 against a victim in 🇺🇦Ukraine, interfering with AI-assisted malware analysis by deliberately triggering LLM safety mechanisms. @reib3n1 1/3

Alexis Dorais-Joncas (@adorais.bsky.social) retweeted
Proofpoint @threatinsight identified a targeted campaign against operations personnel at energy firms linked to projects in Pakistan.
The messages were sent on 18 March 2026, and mimicked invitations to the upcoming Pakistan Energy Exhibition & Conference (PEEC).
We track the activity as UNK_VaporVibes. 1/8

Alexis Dorais-Joncas (@adorais.bsky.social) retweeted
Alongside this activity recently highlighted by Google, @Proofpoint @threatinsight has observed additional exploitation of WinRAR vulnerability CVE-2025-8088 by both financially motivated threat actors and by state‑aligned groups linked to China and the DPRK.

We are tracking widespread exploitation of critical WinRAR vulnerability CVE-2025-8088 by state-sponsored espionage groups and financially motivated actors. 🔍
All orgs and users should update to the latest version of WinRAR.
Learn more and get IOCs:
bit.ly/4t2FuAB

Alexis Dorais-Joncas (@adorais.bsky.social) retweeted

1/16
Recently I became aware of this @Jerusalem_Post breaking "News" article, which turns out to be more like a paid content:
jpost.com/middle-east/iran-n…

Vendors only have partial visibility on any campaign. What appears as highly targeted to one can be widespread to another. It is normal and expected - we all have visibility biases.
Working together and combining our findings is the only way to get closer to the full picture 🤜🤛

Proofpoint also observed the activity reported by Trellix in email threat data targeting financial organizations and people in positions of leadership.
Our researchers offer clarifying context below to supplement @TrellixARC’s technical analysis. 🧵
Developing story - attack against #BGP peers of a European telco. The malicious emails impersonated that same telco and included the ASN of each recipient in the subject line.
The emails contained a password-protected RAR attachment with the malicious payload.
Between December 11 and 12, 2024, a spearphishing campaign targeted at least 20 Autonomous System (AS) owners, predominantly Internet Service Providers (ISPs), and purported to come from the Network Operations Center (NOC) of a prominent European ISP.
All of the observed targeted entities peer with the spoofed ISP and phishing emails were sent to contact addresses present in the AS's WHOIS records, indicative of a highly deliberate targeting effort.
Each spearphishing email was personalized to the target based on their Autonomous System Number (ASN) and purported to relate to a detected BGP (Border Gateway Protocol) flapping session within the target’s network.

Alexis Dorais-Joncas (@adorais.bsky.social) retweeted

Cette information pop à droite à Haude depuis qq jours et je pense qu’il manque beaucoup de contexte alors petit thread 👇

Des clients de banques françaises victimes d’un logiciel malveillant qui vise « des informations personnelles »
➡️ l.leparisien.fr/y94n

Alexis Dorais-Joncas (@adorais.bsky.social) retweeted

Next monday, I'll have the privilege to chat with my colleagues @jiboutin, @adorais and Catherine Dupont-Gagnon (@Cybercitoyen_) for a panel focused on “State-sponsored cyber attacks: current trends and impact on modern society” at #FPS2024. Join us !
👉fps-2024.hec.ca

Rare opportunity to work with an exceptional team!
#ESETResearch is hiring a senior malware researcher for our 🇨🇦office. If you’d like to track some of the most impactful APTs/cybercrime campaigns, don’t wait and apply here 👇
jobs.eset.com/int/job-offer/… 1/3
Alexis Dorais-Joncas (@adorais.bsky.social) retweeted
Lots of good research this week on MacOS activity from Bluenoroff / TA444 / Sapphire Sleet
New record: only one of them said Lazarus instead of Bluenoroff 😂
"reverse engineering is better than hearsay"
Great quote. Feels like something @cherepanov74 would say too!

Alexis Dorais-Joncas (@adorais.bsky.social) retweeted

Public WiFi is so unsafe (it’s not it’s generally fine for personal/family use) that when I arp spoof and dns spoof not only do I get errors with TLS (this site doesn’t have hsts enabled) but my phone (android) literally warns me the network is acting in a suspicious manner….
That’s with defaults! If you harden the phone and browser a tiny bit by forcing dns over https (DoH) it will break the key component here (dns spoofing)!


Alexis Dorais-Joncas (@adorais.bsky.social) retweeted

The main thing I use it for is to check if a port is open.. and I do that simply cause I am old school and it's my habit
Alexis Dorais-Joncas (@adorais.bsky.social) retweeted

Hey @cybleglobal marketing team please clarify your blog and actually credit the author of the Ransomware Vulnerability Matrix… because that would be me 🙃 otherwise others may think you made it 🤦🏻♂️
hxxps://cyble[.]com/blog/ransomware-vulnerability-matrix-a-comprehensive/

