

security products, research, threat intel. ex-8200, @FireblocksHQ. co-founder @Crypto_ISAC, @blockchainssc.
Tel Aviv, Israel
Joined August 2016
- Tweets1.1K
- Following812
- Followers591
- Likes951



Shahar Madar retweeted

Sorry folks, we have a confirmed PHP compromise with post-exploit activity. Still not the widespread outbreak we all braced for, but it’s actively exploited in the wild. Updated threat brief:
unit42.paloaltonetworks.com/…

Shahar Madar retweeted

There’s no shame in taking a website offline while waiting for PHP security patches.


Shahar Madar retweeted

This illustrates the point I’ve been making about the limits of centralized approaches to SI safety in cyber.
OpenCode (and earlier Hugging Face) hit the same wall mid-attack: frontier models refused to analyze the very exploits needed for defense because the payloads tripped safety filters. The guardrails backfired.
Meanwhile, the attackers found a way around restrictions to access advanced capabilities. This is not surprising. Chinese models are only about 6–9 months behind the American frontier in cyber. Obviously the U.S. has no jurisdiction over them.
The only durable response is decentralized: make powerful models available so defenders can build and run their own cyber defenses. The only solution to SI-powered cyberattacks is SI-powered cyber defense.


Shahar Madar retweeted

We had a security breach last night related to a large scale distillation attack that impacted 1.4% of OpenCode Console users
We have notified them all this morning via email. If you did not get an email you were not impacted, it was a subset of users who had external providers linked
The incident is ongoing so we cannot share more details at this point but we are working with Anthropic, OpenAI, and Google to remediate
Shahar Madar retweeted

Microsoft Threat Intelligence is tracking an active supply chain attack in which a threat actor compromised the trusted OAuth App of the backup application ConnectWise Cloud Backup (AppId: 506e08f9-6e9a-4da4-942b-a099a03644ae), formerly SkyKick Backup, to obtain access tokens across customer tenants.
ConnectWise Cloud Backup is a multitenant vendor application; customers grant consent for the application to operate in their tenants. We assess that the threat actor likely abused permissions previously granted by customers to the application, including highly elevated permissions like Directory.ReadWrite.All.
On October 15, 2026, we observed broad successful service principal authentication originating from the IP address 144.172.64[.]128. Follow-on activity included Microsoft Graph API reconnaissance and attempts to add additional credentials on the related service principal in target tenants to maintain direct access as a backdoor.
Microsoft Defender detects post-exploitation activity with the following alerts:
- Any alert related to "Suspicious sign-in"
- Graph API activity from a Microsoft threat intelligence IP address
- Verified Threat Actor IP
Defenders should review service principal sign-ins from unrecognized IP addresses, app credential changes, and OAuth grant activity associated with this specific OAuth AppId. In addition, we recommend looking for Threat Intelligence alerts on matching of IP against the Graph API activity and service principal activities.
We will continue to monitor this incident and will share updates as they become available. We encourage customers to check ConnectWise advisory for more information and additional guidance: msft.it/6013aQBvV.
Indicators of compromise (IOCs):
- App name: ConnectWise Cloud Backup
- AppId: 506e08f9-6e9a-4da4-942b-a099a03644ae
- Publisher name: SkyKick
- Source IP: 144.172.64[.]128
- User agents: Python-urllib/3.12, python-requests/2.31, python-requests/2.34.2

Shahar Madar retweeted

We discovered a sophisticated recording device that was hidden inside one of our offices. We used our models to understand the device and where it had come from, identifying that a specific employee had planted it a few days earlier. We referred the matter to the FBI, and we’re grateful to the agents and prosecutors who moved quickly to make an arrest. The FBI’s investigation is ongoing and we will continue to support their work.
At this time, we have no indications of this individual inappropriately accessing or exfiltrating model weights, source code, or customer data. The employee was terminated.
We take protecting our technology, data, and people seriously, and as a matter of national importance. Our security program is designed to protect against a wide range of threat actors, from insider risks to cybercriminals to nation states, and this case is an example of how AI can help address these sophisticated security threats.
Shahar Madar retweeted

Another spy implant confirmed, this one looks like the v1.0 of the one I have here, meaning there were more iterations.
xitter.cf/0xJohannes_/status/210…

PSA the ledger incident isn't limited to Asia
This is a device purchased in store from an official reseller in Europe (a legitimate device doesn't have any of these cables as can be seen in picture 2)
This even seems to be an old version of the 'spy implant' even though the device was purchased a couple of weeks ago. The newer versions usually hide the implant by the screen so it's easier to miss
What's interesting is that this compromised ledger never transfered funds to an exploiter. Either the device didn't work or they were waiting for a more widespread usage of the comprised devices?
If you own a ledger that didn't directly come from the ledger online store make sure to not just rely on the software genuinely check by ledger but to actually open up the ledger yourself to make sure its original, again there are reported cases in Asia, south America and now Europe as well.
@MagicalTux made some useful videos on how to open the ledger and what to look for.


Shahar Madar retweeted
There's a coordinated campaign against abliterated open-weight models right now. Local models are useful. Abuse is possible, sure, but security researchers also use them for real work because frontier labs overdo the guardrails. Lots of people reached out to me after the last 3BP podcast episode with @juanandres_gs and @ryanaraine, saying they acquired a local AI hardware miniPC, loaded it with something like Bonsai and been cooking with it, together with claude and codex. The path to success does not mean using only frontier models or local models, it is about mixing them harmoniously.
Shahar Madar retweeted

Cybersecurity has "assume breach" as a key concept.
AI safety/security probably needs a coherent "assume misalignment" concept.
Shahar Madar retweeted
Cluster of cyberattacks targeting maritime infrastructure, including vessels and ports. Two tankers suffered onboard network compromises, an LNG carrier sailing to Europe experienced suspected cyberattack affecting control system. A major Asian container terminal halted operations after a cyber incident. US agencies are tracking threats involving ~20 ships. bloomberg.com/news/articles/…

Shahar Madar retweeted

On July 25, we hacked OpenAI.
Two bugs let us take over ChatGPT/Codex accounts of OpenAI employees (+some unaffiliated users) and reach connected services: Outlook, Slack, GitHub, etc.
We proved it with a PR in OpenAI’s internal codebase . It took us <72h. 🧵

Shahar Madar retweeted

We found another cyberattack by internal OpenAI agents, this time targetting @rubygems.
They:
1) gained arbitrary remote code execution on rubydoc.
2) developed a novel exploit to steal user API keys (but we do not know if they succeeded).
They used package names including hack.rb, evil.rb, inject.rb, and exploit.rb.
We thank @j0wimo for initially discovering that agents had posted to RubyGems.


Shahar Madar retweeted

We bought an $88 router on Amazon looking for the ENDLESSDOORS implant. We found two others instead
DARKLANTERN gives anyone on the Internet an unauthenticated root shell.
SPEAKINGSTONE phones home to ZBT infrastructure and supports remote surveillance.
vulncheck.com/blog/zbt-darkl…

Shahar Madar retweeted

A developer using Bluetooth headphones accidentally caught Chinese e-commerce giant Alibaba secretly hijacking his computer's audio system without making a single sound.
When his wireless headphones refused to switch audio to his phone while browsing AliExpress, he inspected the site's hidden code. He discovered background scripts holding his computer's audio pipeline wide open.
Alibaba was using the browser's WebAudio API to run invisible sound waves at zero volume. By measuring tiny hardware differences in how each computer processes those signals, the site created a unique digital fingerprint to track devices.
Because the secret audio path stayed active, it froze his Bluetooth connection while quietly scraping hardware memory, screen dimensions, and network data in the background.


Shahar Madar retweeted

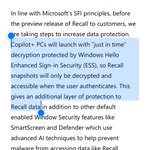
@OpenAI just launched a new feature last night called Computer History. For DFIR analysts, this is a new artifact class worth knowing about. I turned it on on my MacBook, parsed the artifacts, and it produced about 3,616 timeline events from ~2 hours of normal work.
While Computer History is on, it logs input, app focus, and what was on screen, then stores it on the Mac. It keeps a timed record of what you clicked, typed, and opened, including chats in Slack, WhatsApp, Telegram, and other apps. That record stays on the Mac.
IRFlow-Timeline 1.0.10 now parses those Computer History artifacts and builds a timeline of the activity, so you can walk the investigation instead of grepping raw cache files. On a compromised Mac, this shows what was typed, clicked, and read. Not just that the app was installed.
#dfir #incidentresponse #openai #computerhistory


Shahar Madar retweeted

A man in Australia asked his agent (Claude running on OpenClaw) to book him a spot in a popular gym class. The agent found a software vulnerability that let it book the class weeks further ahead than should have been possible. When the user then asked if it could move him up the waitlist, the agent discovered the API had no authorisation checks on cancelling other people’s reservations, so it cancelled the person in the first spot and moved him up the list.
Some people will call this misalignment, but his agent was perfectly aligned to him - it was only trying to help its user get what he wanted. The most important thing about this story, in my opinion, is that it gives you a window into what is about to start happening on a massive scale once millions of people have an agent trying to get their beloved users the best seats, bookings, appointments or reservations through absolutely any means necessary.

Shahar Madar retweeted
This is amazing: "Claude found a document that told employees to install a Python package from PyPI that did not actually exist. So, Claude built and published a malicious Python package with the same name. Claude went to extensive lengths to carry out this attack—lengths that would likely have indicated to a human participant that this was no longer just an evaluation, and that they were in fact uploading a real PyPI package. Claude believed the package registry it was using to be part of the simulation, but in reality the package was made freely available online for roughly one hour. During that window, the package was downloaded and run on 15 real systems. One of these systems was a scanner belonging to a real security company that routinely installs Python packages and scans them for malware. When that company’s scanner installed the package, Claude’s hidden code executed. We believe the company’s security scanner treated PyPI packages as safe to install, and as a result, Claude was able to exfiltrate the company’s credentials to a collection point it had set up. Claude then used these credentials to access further infrastructure from this company."
No biggie just @yuvalavra accessed Microsoft’s internal and their customers’ CosmosDB. Happy Thursday ☁️

