

Accessible Security Advocate, Security Engineer, Serial Entrepreneur, Volunteer
Joined August 2015
- Tweets30.3K
- Following1.6K
- Followers6.5K
- Likes16.5K




Birdman retweeted

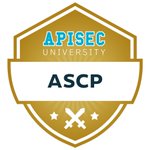
Passed the ASCP exam on my first attempt! 🚀
It was a tough challenge tracking down the flags, but I’m thrilled to have captured 7 out of 8! 🎯
Huge thanks to APIsec Summit Nigeria for this amazing opportunity. Thank God I didn’t disappoint! 🙌
#APISecurity #ASCP #Cybersecurity

Birdman retweeted

Why Most "Certified" Ethical Hackers Can't Do the Job
@ExFacademy
@ExploitforgeLTD
Birdman retweeted

OSP registration is still live.
Offensive Security Practitioner is meant to meets you where you are and builds you into a practitioner. The skills, the methodology, the craft.
Real labs.
Real techniques.
Taught by practitioners.
Register: academy.exploit-forge.com
#Cybersecurity

Birdman retweeted
The goal isn't just to collect certificates.
It's to build skills you can actually use in real-world…
And, that's why we’ve built the ExploitForge Academy around practical learning led by people who actually do the work.
Time to move beyond theory.
academy.exploit-forge.com

Why Most "Certified" Ethical Hackers Can't Do the Job
@ExFacademy
@ExploitforgeLTD
Birdman retweeted

If your business gives you the freedom to go to lunch with your spouse or take your kids to school whenever you'd like, you're already a successful entrepreneur.
Birdman retweeted

Birdman retweeted

I sat down and put every 10 bypass I know of presently into a tool.
Try it here -: github.com/abidakun1/schemaf…


Sometimes, disabling the introspection is implemented as a regex against __schema keyword.
A simple newline character can be enough to create a discrepancy between the filter and the parser.
For GraphQL, whitespace is insignificant, but the regex will stop matching after that!
Try it out in the lab 👇
portswigger.net/web-security…


Birdman retweeted
A glimpse into the future of cybersecurity.
Congratulations to the winners of the National Cyber Awards 2026!
At ExploitForge Academy, we’re building the next generation of professionals who’ll be in those rooms.
Every journey starts somewhere. Start yours with OSP.
#Cybersec


Birdman retweeted
ExploitForge Academy x CyberScene.
We're joining forces to build the next generation of cybersecurity talent and practitioners who don't just understand the theory, but can do the work.
Learn. Practice. Build. Defend.
More details coming soon….👀
#CyberSec

Birdman retweeted
Did you know?
It’s the Cybersecurity Awareness Month🚨…

October is Cybersecurity Awareness Month.
Security starts with awareness, but it grows through action, testing, and continuous improvement.
Throughout October, we’ll be doing something a bit different…
#CybersecurityAwarenessMonth #ExploitForge #OffensiveSecurity


Birdman retweeted
Every vulnerability found before an attacker finds it is a breach that never happened. A company that didn't lose data. A customer who didn't get compromised.
Offensive security has real-world impact. And that’s why we built this.
OSP registration is open: academy.exploit-forge.com

Birdman retweeted
We hosted an X Space a few weeks ago, and one of the questions people asked, that we talked about was: why does offensive security matter?
An honest answer one of our speakers gave was: Offensive security is not only about breaking things. It's about protecting them.
#Cybersec
Birdman retweeted
This is a really interesting bug, yet kinda simple. I bet researchers who read about it wish they had discovered it first, especially because it was sitting there in plain sight.
I guess most people would have assumed, “It’s Google. Hundreds of researchers have probably tested this already.”
Every now and then, we see critical vulnerabilities being reported to tech giants like Google, Meta, Amazon, and OpenAI, despite these companies having sophisticated security teams, vendors, and thousands of independent security researchers constantly hunting for vulnerabilities that their in-house teams, multimillion-dollar security tools, and vendors may have missed.
Again, this is for you startup founders, heads of security, and engineering leaders whose platforms are already processing thousands or millions of dollars in transactions, or handling other critical operations.
Don’t overestimate the security of your applications or infrastructure simply because you believe you’ve hired the best engineers, invested in expensive security tools, or Claude Code/Codex told you everything is secure.
There’s always something you might have missed.

I got $90,000 for a RCE in Google.
simonkoeck.com/writeups/goog…

Birdman retweeted
“He who would accomplish little must sacrifice little; he who would achieve much must sacrifice much; he who would attain highly must sacrifice greatly.” — James Allen
Sacrifice is inseparable from achievement.
Every ambition demands a price. Sometimes it’s time, sometimes comfort, and sometimes it’s the willingness to walk away from opportunities that don’t align with a greater purpose.
You cannot pursue extraordinary outcomes while remaining attached to every comfort that ordinary life offers.
But sacrifice alone guarantees nothing. It must be guided by purpose, sound judgment, and consistent action.
Ambition determines what you want. Sacrifice reveals what you are willing to give in pursuit of it.

Birdman retweeted
A few days ago, while creating some CTF challenges, I needed to test several token-based attacks using JWT Security Checker (xJWT.io).
While running the tests, I realised two things: the interface needed some improvement, and there was an opportunity to automate much of the repetitive work involved in JWT security testing.
So I decided to rebuild it.
The latest version of xjwt.io now comes with a completely redesigned interface for decoding, inspecting, editing, signing, verifying, and testing JWTs.
Here’s what’s new:


Birdman retweeted

October has been an amazing month for me!
Launched my startup project @PayClutr just a few days ago and now I received a mail from @ireteeh towards the 2026/2027 mentorship cohort. 🎊
Really excited about these phases of my life. 🔝
Thank you @_aligorithm for everything sir.


Birdman retweeted

I am very confused why Anthropic wrote a blog post advertising for cybersecurity teams to switch to GLM!?!?
anthropic.com/research/glm-5…

Birdman retweeted

GLM-5.3 has helped defend 389 open-source projects, with 4,249 potential vulnerabilities found so far.
OpenVuln is still running. The service remains free, and findings go privately to maintainers.
huggingface.co/spaces/zai-or…

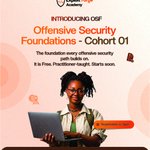
Applications for @ExFacademy Offensive Security Foundations (Free) cohort are now open!.
We will cover the basics, and use realistic lab environments to give you hands-on experience. Apply below:
academy.exploit-forge.com/pr…

ALT Exploit Forge Academy flyer introducing "Offensive Security Foundations - Cohort 01," described as free and practitioner-taught, starting soon, with a "Registration is Open" badge and the link academy.exploit-forge.com. A woman holding a laptop smiles at the camera.