

Independent Bitcoin attribution and holdings data. Exchanges, ETFs, funds, governments. Charts and API.
Joined May 2022
- Tweets23.5K
- Following663
- Followers18.2K
- Likes14.6K



Sani | TimechainIndex.com retweeted

more than half of all BTC supply is sitting in addresses with no known attribution
despite all the institutionalization and centralized ownership over the years, still a ton of bitcoin (maybe even most) is held by individuals in self-custody 🔐

Sani | TimechainIndex.com retweeted

Today, ICANN just published the 2026 new gTLD applications! Wiz & Associates filed a community priority application for the .bitcoin TLD, on behalf of the people and organizations that run, build, and provide the infrastructure, software, and services of the Bitcoin network. 🧵
Sani | TimechainIndex.com retweeted

EntropyLab v1.0.0rc2 is ready for testing. 🪨
Download, verify, disconnect.
Release notes and download:
github.com/OogaBoogaX/entrop…

Sani | TimechainIndex.com retweeted
🎬 THE MONEY TREE 🌳
Who gets to change the rules?
> a natural history of western monetary thought from Locke to Satoshi
watch my 15 minute documentary about the evolution of monetary philosophy from 1695 to 2026.. written by me, made with opus 5.5 & eleven labs
Sani | TimechainIndex.com retweeted
EntropyLab’s first release candidate, v1.0.0rc1, is here. 🪨
A Bitcoin key and wallet calculator in one HTML file. You bring your own entropy; it does the math offline.
Download, verify, disconnect. Send feedback:
github.com/OogaBoogaX/entrop…

Sani | TimechainIndex.com retweeted

The bee is fuzzing LFG💪

you don't know about #OogaBoogaFuzz 😂 cc:
@w_s_bitcoin
@PortlandHODL
@NodeHello
@MrHodl
@without_rulers
bitcoincore-dev.github.io/oo…

Sani | TimechainIndex.com retweeted
EVERY BITCOIN BY THE PRICE IT LAST MOVED
a short video of bitcoin history by its UTXO realized price distribution (URPD)
Sani | TimechainIndex.com retweeted
i asked opus 5.5 to make a 3 min video about the history of bitcoin
i told claude to rely on data from my local 1.8 tb postgres database of bitcoin data (coins, blocks, hacks, attribution, everything)
here’s what opus made in 1 hour 22 mins on max effort with a 10 line prompt
Sani | TimechainIndex.com retweeted

Meet @SaniExp from Timechain Index 📉📈👀
Find out what transparency in on-chain data is ...
Interview with @AnthonyDessauer & @RatPoisonaut
#memes
#stackchainmagazine
#stackchain
#bitcoinart
Link below 👇

Sani | TimechainIndex.com retweeted

There's some confusion about what, exactly, was exploited here.
I've seen claims that this was a long-standing bug, exploited after the "fix" was pushed to the open source repo but before that fix could be rolled out in production.
That does not appear to be true.
Instead, it seems that the fix *was* deployed, but inadvertently introduced a new bug which was subsequently exploited.
Most of the network was still running official releases, none of which contain the new bug. Those nodes correctly rejected the block containing the exploit and stalled at height 4050335.
The timeline is roughly as follows:
• 2016-07-12: Range proof caching added
• 2017-11-08: Range proofs extended to support assets
• 2019-03-19: Range proof cache key "simplified", dropping asset & script fields. introduces Bug A.
• 2026-09-01: Bug A "fixed" by extending cache key to include asset + script. introduces Bug B.
• 2026-09-06: Bug B exploited, reserves drained, chain split.
The original "Bug A" allows some limited cache poisoning because the cache key doesn't commit to the asset and script, allowing a cached result for a range proof for one asset to be applied to a different asset or context.
Exploiting this in practice looks quite difficult, since the amount must match the primer and the proof must be genuine.
The 2026 "fix" added those missing fields to the cache key, producing a format like:
"proof | amount | asset | scriptpubkey"
But this unfortunately made the key easier to manipulate and exploit:
The four fields are concatenated without separators or length indicators.
Since both the proof and the scriptpubkey are variable length, an attacker can stretch the proof and shrink the script to produce the exact same cache key from different proofs, amounts, assets and scripts.
This lets an attacker smuggle arbitrary confidential output amounts and junk proofs past the range proof checker without proper validation, which breaks the guarantees that prevent hidden inflation.
On-chain evidence suggests that this second bug is what was exploited:
Two primer transactions each created an op_return with carefully constructed scriptpubkey and valid range proof for a (presumably) zero value output.
blockstream.info/liquid/tx/2…
blockstream.info/liquid/tx/7…
This produced a cache key like:
" | | | OP_RETURN OP_RETURN"
The exploit transaction then created a large negative op_return output with an invalid range proof:
blockstream.info/liquid/tx/f…
The invalid proof is padded with bytes corresponding to the primer's valid amount and asset fields, aligning the actual amount and asset fields with the same bytes from the primer's opreturn payload:
" OP_RETURN | | | OP_RETURN"
The exploit transaction could then include a second output crediting the attacker with a large positive value, balanced out by the fake negative amount.
Because the success was already cached, the invalid proof was never actually checked and the transaction was accepted as valid by nodes running versions of the software vulnerable to bug B.
Although the amounts are blinded, this is the only output with an invalid range proof anywhere in the peg-out's recent ancestry, so this must be where the inflated coins were created.
And since the padding only produces a cacheable key under the new format, it must have been the newer bug that was exploited.


Sani | TimechainIndex.com retweeted
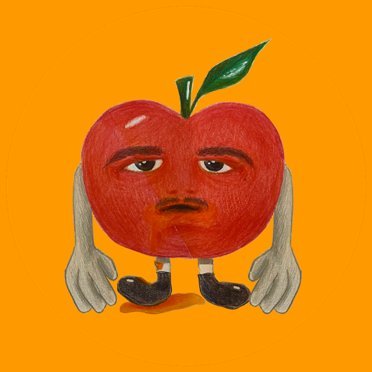
Who’d be interested in a limited-edition “Seed Round” of EntropyLab merch to help fund our clankers for the next few weeks/months?
I’m thinking a small run of a few different items...just 21 of each, individually numbered and tastefully branded with the EntropyLab logo.
Each piece would be marked:
Seed Round · x/21


Sani | TimechainIndex.com retweeted

There are 3 really simple things you can do to protect yourself against 90% of social engineering attempts. Most of these operations are casting a big net and just trying to scoop up unsuspecting fish. So make yourself a slightly harder target and they will pass right over you.
1. Don’t ever answer the phone for unknown numbers. Even when the location says Mountain View, CA, or the caller ID says Google. It’s fake! To ensure you don’t get tricked, set your phone setting to Silence unknown numbers automatically. On iPhone it’s Settings ➡️ Phone ➡️ Screen Unknown Callers ➡️ Silence (see screenshot). Many times, bad actors are using fear over the phone to get you to do things you shouldn't - like give them control of your email.
2. Add 2FA to your main email account, and make sure it uses a unique, strong password. Use either an authenticator app or a Yubikey (better) as your 2FA. Accounts.google.com ➡️ Security & sign-in ➡️ Turn on 2-step verification. Then make sure your password is a unique password that isn't used anywhere else. If you are using the same password in more than one place, it's highly likely that it's been leaked. Just go to haveibeenpwned.com, put in your email address, and look at how many leaks its been in.
3. If you use Google Authenticator, turn off the cloud sync. When you have cloud sync on, if someone compromises your Google account, they can steal your 2FA. It makes 2FA ➡️ 1FA, and that is bad.
These are the basics that you can do to protect yourself against a huge amount of social engineering. And then if you want extra protection for your BTC, check out the next post 👇


Sani | TimechainIndex.com retweeted

Over 10k BTC from multisig wallets have now been submitted through slipstream since the coldcard weak seed thefts began.
By doing this a previously concealed witness script can remain private until the transaction confirms, avoiding the risk of theft.
research.mempool.space/coldc…

Sani | TimechainIndex.com retweeted
📊 updated numbers on coldcard exploit
8865 addresses lost 1789.28 BTC worth $114.7m at the time of theft ($138.8m today)
- loss by address
median 0.00152
mean 0.20184
dormancy median 3.2yr
dormancy mean 3.6yr
- loss by victim reports (221)
median 1.04272
mean 3.57792
dormancy median 3.25yr
dormancy mean 2.99yr
victim reported loss 790.72 (44.2% of total)
if we expand to include medium confidence losses (not yet confirmed) the total loss is 1,824 BTC ($140m at the time of loss)

Sani | TimechainIndex.com retweeted

Signs you don’t understand Bitcoin:
You have a collaborative custody.
Bitcoin's white paper suggests and I quote:
''A purely peer-to-peer version of electronic cash would allow online payments to be sent directly from one party to another without going through a financial institution.''
Sani | TimechainIndex.com retweeted

On August 6th, the Bitcoin Red Team sent us a report on AQUA. Around the same time, reports were coming in from independent researchers, and we'd been running our own scans across the codebase using frontier AI models.
Between the three, one high-priority issue surfaced. It was theoretical, and it sat in an experimental feature for sweeping Bitcoin and Tether poker chips. That feature sees very limited usage and handles small amounts. It has been patched.
We found no issues with seed entropy, and none pertaining to the core AQUA wallet and services. A handful of minor items came out of the review, none urgent, and they're queued for upcoming releases.
The caveat we'll keep repeating regardless: AQUA is a hot wallet. Hot wallets carry inherent risk by design. If you're holding large amounts for the long term, use cold storage.
Many thanks to the Bitcoin Red Team, to the researchers who filed reports, and to everyone who takes the time to tell us when something looks wrong. Bitcoin gets safer because people do this. 🐬
Sani | TimechainIndex.com retweeted
What a mess. Unfortunately this Trezor address leak will directly lead to an increase in targeted social engineering and potentially wrench attacks. Here are my recommendations for what to do if you were in this breach (or just want to protect yourself against the result of these breaches in the future).
Social engineering protection
Scammers will use the combination of having your personal information to both target you (phone, email) and convince you that they are legit (using your name and potentially home address as proof that they know you and are here to help).
They will contact you via phone or email with targeted lies meant to scare you into talking to them and taking the actions they want you to, in the name of protecting your bitcoin. Ignore any communication from "Trezor" that doesn't come from their official domains (the @Trezor handle, trezor.io are the main ones I know of).
You should also ignore communication from "Google" or "Apple" pretending like your email is compromised. They trick you into giving them your email credentials, and then once inside your inbox they can do all manner of things to trick you without Google's typical filters stopping them.
Generally a company's support team will never call you on the phone without you contacting them. If they reach out proactively and are trying to get you to take any action to "remain safe" - refuse.
Social engineers steal much more money on a regular basis than physical attackers. Most people worry about physical attack more because it sounds scarier, but the bigger risk of actual funds loss is social engineering. Get your suspicion antennae up.
Phishing
Phishing has a lot of overlap with social engineering. The main difference in my mind is that phishers put in less effort than social engineers. Social engineers may use phishing tools to help them. Phishers are just putting their nets out and trying to get you to make a mistake.
Be very suspicious of emails directing you to go to Trezor's website or download a new Trezor app. Triple check the URL for Trezor or any hardware wallet website that you visit. Even if you Google Trezor, there are fake Trezor phishing apps running Google ads that will tell you to type in your seed phrase and then steal your money. Be very careful when downloading or using new wallet apps that you are getting the right one.
Wrench attacks
The one everyone worries about the most, even though it's the least common. Unfortunately since this breach includes physical addresses, it's possible we will see some wrench attack attempts come from it. Unless you are going to move, the best you can do is try to deter attackers and make sure that if it happens, they can't steal all your money.
Distribute your keys and use a multisig to ensure that you don't have enough keys to spend bitcoin at your house. Then consider keeping a small-ish amount of BTC in a single sig wallet that you are willing to give up to make someone go away.
We don't recommend the type of duress wallet that uses the same device/software as your main wallet, but when you type in a different PIN it brings up the fake wallet. It's too hard to remember the duress PIN when someone is beating you up, and too easy to give in when they ask you for more after you pay them from the duress wallet. You need to make it so you truly can't send them all your money.
Casa recently built Guardian Mode to help protect against social engineering and wrench attacks. It requires the Casa key to sign for all transactions you send. We do a video verification call to make sure you are not being tricked or under duress before signing with our key. Available to Premium+ Casa members.
You can also check out an old post we did about physical home security, which unfortunately we have to reshare every year or two: blog.casa.io/a-home-defense-…
Very sorry to all the people who were caught up in this. Rough few weeks for bitcoin security. Reach out to us if you need assistance on any of these points.


We have some difficult news to share. Unfortunately, one of our shipping providers has experienced a data breach that exposed sensitive order data. This affects new customers in the US, UK, Sweden, Colombia, Brazil, Italy, and Portugal who received an order within the 90 days prior to August 8th, 2026.
The data exposed:
- Full names
- Shipping addresses
- Phone numbers
- Email addresses
The incident affects 11,742 customers with full exposure (name, email, phone number, shipping address) and 1,947 customers with partial exposure (name, city, email). The breach is limited due to Trezor’s strict 90-day data storage policy (we were also able to negotiate the same terms with fulfillment partners, who follow the same policy).
All affected customers have been contacted separately by email.
Our systems and devices remain secure, but affected customers could experience an increase in phishing attempts.
NEVER enter your wallet backup on a website or share it with anyone, and only check for updates on official Trezor channels.
We are deeply sorry to the community and those affected.
We are investigating this situation and will post updates on our blog:
trezor.io/blog/news/recent-c…

Sani | TimechainIndex.com retweeted
The onchain metrics around the Coldcard incident reinforce how important self custody is to the resilience of Bitcoin as an asset class.
In the couple of days around the hack:
- 2.1k BTC was stolen
- 22k moved to exchanges
- 233k moved out of long term holder wallets in on chain transactions
We at Casa know (based on actual customer conversations) some of the 233k was people moving from non-Coldcard single sig (ie Ledger, Trezor) to multisig wallets, because they realized single sig wasn’t secure enough for their needs. And other coins were moved from multisig->multisig as people removed Coldcard from their keyset.
So somewhere between ~10x-100x the amount of bitcoin stolen was moved to safety as people sounded the alarm.
This is a giant flashing neon sign showcasing the resilience that self custody adds to the network. If all that BTC was held at a custodian and the custodian was hacked instead, those numbers would have been flipped. A little bit might have gotten out the door to safety, and most would be stolen. As it was, the thieves had to crack one wallet at a time (and are still going), earning a little BTC each wallet, instead of cracking one wallet and getting a massive payday. And the asset price (and confidence) would have certainly taken a much bigger hit.
Self custody is not just good for Bitcoiners, it is good for Bitcoin.
H/t to @_Checkmatey_, @intangiblecoins, @SaniExp for the data


Sani | TimechainIndex.com retweeted

There is a critical vulnerability being actively exploited on BTCPay Server, which can result in the loss of funds.
Please update your BTCPayServer to 2.4.2 by going to Admin Dashboard -> Server -> Maintenance -> Update & verify the 2.4.2 version string in the footer.
If you are unable to update right away, turn off your BTCPay Server to prevent unauthorized access until you can update.
Sani | TimechainIndex.com retweeted

‼️ In light of the recent ColdCard MK3 situation.
BE ALERT FOR SCAMS!
You may see messages asking you to “verify your wallet,” “migrate funds,” or enter your seed words into a website or tool.
NEVER DO THIS. No legitimate company will ask for your seed phrase.
If you are unsure about anything, check with our team before taking action. @Thebitcoinway_