

https://xitter.cf/t.co/YMiKMjgKt7
Frankfurt/SF
Joined February 2009
- Tweets214
- Following881
- Followers338
- Likes39





Sergej Epp retweeted

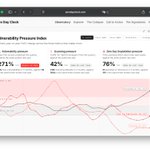
The window to patch software bugs is collapsing
Of the bugs hackers actually exploit, ~87% are now being attacked on or before the day the bug is public knowledge
That share was 23% in 2020
Charts of the Week: a16z.news/p/chart-of-the-wee…

Sergej Epp retweeted

Friday afternoon @gadievron says "I'm working on a CISO community document for Monday. Want to collaborate? Releasing Monday." I said "Sure." (I have a problem with that word.)
@AnthropicAI had dropped Mythos on Monday. @cloudsa is running an emergency CISO Zoom on Tuesday. @SANSInstitute was already building BugBusters this Thursday with Ed Skoudis, Joshua Wright, and Chris Elgee. The entire community was asking the same question: what do we actually DO about this?
Three nights later we have a 30-page strategy briefing with 60+ contributors. "Sure" turned into barely sleeping Friday, Saturday, Sunday while @gadievron and @rmogull dragged this thing into existence. (My son checked to see if I was still breathing around hour 40. I think he was mostly concerned about if Uber Eats delivered Five Guys yet.)
The contributing authors list reads like someone raided a cybersecurity hall of fame: Jen Easterly, Bruce Schneier, Chris Inglis, @philvenables, Heather Adkins @argvee, @RGB_Lights, @sounilyu, @jimreavis, Katie Moussouris @k8em0, Jon Stewart, Maxim Kovalsky, David Scott Lewis, Joshua Saxe, John Yeoh, Ramy Houssaini and James Lyne. Every single one said yes within hours.
Cloud Security Alliance @cloudsa, @SANSInstitute, [un]prompted, @OWASPGenAISec -- four organizations that don't usually build things together at this speed. This is the start.
SANS reviewers who showed up: Chris Cochran @chrishvm, @edskoudis, Viswanath S Chirravuri @vchirrav, @bettersafetynet, Ciaran Martin
Thursday @edskoudis, @joswr1ght, and @chriselgee stop talking and start showing.
Live AI-assisted vulnerability discovery against real code. No slides about the future. Terminals and bugs. (The kind of demo where something breaks and that IS the point.)
Full reviewer list is in the doc. If you know someone on it, send them a note. They earned it.
But an even bigger thank you -- seriously -- from the entire cyber security community needs to go to @gadievron for once again bringing the avengers together -- like in Endgame (is that what Mythos is?) -- and you all know the scene -- but we need someone to create the meme with Gadi Evron with his shield and Mjölnir saying "Avengers..... assemble!" because that is exactly what he does. A lot it seems.
Read it: labs.cloudsecurityalliance.o…
Going to sleep now. Setting my alarm for Thursday. (Not joking.)
#CyberSecurity #AISecurity #SANSInstitute

Sergej Epp retweeted

An Expedited Strategy Briefing on Mythos, Glasswing, and building a security program for what comes next, by 250 CISOs, and the wider community.
It is still a draft, with some design incomplete, but we felt it was imperative to release.
Link:
labs.cloudsecurityalliance.o…
Sergej Epp retweeted

Zero stolen credentials to full AWS admin.
Eight minutes.
CVE to exploitation used to take 18 months.
Now it's under a day.
A SOC analyst isn't losing because they lack tools.
They're losing because the loop is too slow.
#cloudsecurity #CISO @EppSecurity @sysdig
Sergej Epp retweeted

You can now train @physical_int style robots in 1 day for only $5k. Anvil’s devkits have all the hardware, software, controls, cameras, and more ready-to-go. (1/5)
Sergej Epp retweeted

Meet Corridor: the security layer for AI coding. Now generally available.
@CorridorSecure is the first security tool that moves at the speed you build – enforcing security guardrails in real time.
Get two weeks free, with plans starting at $20/month.


Sergej Epp retweeted

Mehr als 70(!) führende deutsche IT-Sicherheitsforscherinnen kritisieren die #LucaApp.
Darunter Professorinnen des CISPA Helmholtz Center for Information Security, der Ruhr-Universität Bochum, der TU Darmstadt, des neu gegründeten Forschungsinstituts Code.
zeit.de/digital/datenschutz/…

Sergej Epp retweeted

Super excited to keynote the LogPoint ThinkIn conference in June (lnkd.in/e-Z8dDj). I'll be talking about the evolution of #log analysis and #SIEM: From past to future. What has worked and what will the future hold? What do you think? Any opinion on the topic?
Sergej Epp retweeted

Per @EppSecurity: "The traditional, centralized SOC will struggle to deliver value in light of these trends. We need a new model. A cyber fusion center might be the solution." cisostreet.com/cyber-ops-mus… #cybersecurity #SOC #fusion #cyberfusion #devops
Sergej Epp retweeted

As 5G deployments begin in Europe, securing networks, data, IoT devices and enterprise services is essential. Read the new blog by @EppSecurity , Palo Alto Networks CSO for Central Europe, "How Regulation Is Impacting 5G Security in Europe." blog.paloaltonetworks.com/20…
Sergej Epp retweeted
It seems that @virustotal started to show @sigma_hq matches for (some) samples this morning
Since Sigma matches can be generated from log entries, samples have to go through behavioural analysis

Sergej Epp retweeted

Without excessive (!) cynicism and cursing, what useful things can you tell people who want to keep *all* the security controls/tools they have on-premise when moving to the cloud? #question
Sergej Epp retweeted

"Mein Lehrer wollte, dass ich auf die Hauptschule gehe. Erst durch das Einschreiten meines deutschen Nachbars konnte ich aufs Gymnasium." — Heute ein Hoch auf unsere 🇩🇪Nachbarn!
Prof. Dr. Uğur Şahin
Entwickler des Impfstoffes gegen Covid19
Sohn von türkischen Gastarbeitern

Sergej Epp retweeted
#KrbTgt passwords are like underwear - you may not see a reason to change it, but you should do it frequently

Sergej Epp retweeted

The number of firmware vulnerabilities has skyrocketed in recent years. Are you asking your CISO the right questions about the risks to your organization? Ideas @EppSecurity
bit.ly/2It0BKr #cybersecurity