

https://xitter.cf/t.co/YMiKMjgKt7
Frankfurt/SF
Joined February 2009
- Tweets214
- Following881
- Followers338
- Likes39





Anyone can be a GRU Spy now.
AI learned every public playbook: it's in the weights. TTPs no longer tell you who attacked you.
But AI has an accent. The faster it moves, the more it confesses.
sergejepp.substack.com/p/att…

Running an ant colony of AI agents all with different harnesses across different machines?
Here's your queen's-eye view for mac-os to rule them all.
github.com/eppser/antarium


If you worked a lot with BaaS like Supabase or use vibe coding platforms like Lovable, you might? know they need they can leak quickly data. So I wrote a small tool: unruly.
Give it a URL, it shows you what an attacker can write or read.
github.com/eppser/unruly

You can also try out directly in the browser (Thx WASM): lnkd.in/edwS66U9
Sergej Epp retweeted

The window to patch software bugs is collapsing
Of the bugs hackers actually exploit, ~87% are now being attacked on or before the day the bug is public knowledge
That share was 23% in 2020
Charts of the Week: a16z.news/p/chart-of-the-wee…

Finally, a CISO Simulator that lets you feel the pressure. ..if you have a sunday afternoon, two bored kids + Codex Astra. Open source, MIT.😅
Super realistic!
github.com/eppser/ciso-simul…
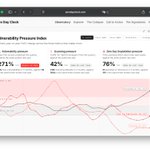
We're retiring 🔴 ZeroDayClock's headline metric.
Measuring cybersecurity honestly is much harder than our industry admits.
I would rather show you where we are stuck than sell you certainty. 🧵

No licensed data. No proprietary models. No black-box numbers.
It tracks pressure across three live streams:
👉 Vulnerabilities entering the public CVE registry
👉 Catalogued exploitation arriving with no warning (KEV)
👉 Active scanning seen by honeypots

Sergej Epp retweeted

Friday afternoon @gadievron says "I'm working on a CISO community document for Monday. Want to collaborate? Releasing Monday." I said "Sure." (I have a problem with that word.)
@AnthropicAI had dropped Mythos on Monday. @cloudsa is running an emergency CISO Zoom on Tuesday. @SANSInstitute was already building BugBusters this Thursday with Ed Skoudis, Joshua Wright, and Chris Elgee. The entire community was asking the same question: what do we actually DO about this?
Three nights later we have a 30-page strategy briefing with 60+ contributors. "Sure" turned into barely sleeping Friday, Saturday, Sunday while @gadievron and @rmogull dragged this thing into existence. (My son checked to see if I was still breathing around hour 40. I think he was mostly concerned about if Uber Eats delivered Five Guys yet.)
The contributing authors list reads like someone raided a cybersecurity hall of fame: Jen Easterly, Bruce Schneier, Chris Inglis, @philvenables, Heather Adkins @argvee, @RGB_Lights, @sounilyu, @jimreavis, Katie Moussouris @k8em0, Jon Stewart, Maxim Kovalsky, David Scott Lewis, Joshua Saxe, John Yeoh, Ramy Houssaini and James Lyne. Every single one said yes within hours.
Cloud Security Alliance @cloudsa, @SANSInstitute, [un]prompted, @OWASPGenAISec -- four organizations that don't usually build things together at this speed. This is the start.
SANS reviewers who showed up: Chris Cochran @chrishvm, @edskoudis, Viswanath S Chirravuri @vchirrav, @bettersafetynet, Ciaran Martin
Thursday @edskoudis, @joswr1ght, and @chriselgee stop talking and start showing.
Live AI-assisted vulnerability discovery against real code. No slides about the future. Terminals and bugs. (The kind of demo where something breaks and that IS the point.)
Full reviewer list is in the doc. If you know someone on it, send them a note. They earned it.
But an even bigger thank you -- seriously -- from the entire cyber security community needs to go to @gadievron for once again bringing the avengers together -- like in Endgame (is that what Mythos is?) -- and you all know the scene -- but we need someone to create the meme with Gadi Evron with his shield and Mjölnir saying "Avengers..... assemble!" because that is exactly what he does. A lot it seems.
Read it: labs.cloudsecurityalliance.o…
Going to sleep now. Setting my alarm for Thursday. (Not joking.)
#CyberSecurity #AISecurity #SANSInstitute

Sergej Epp retweeted

An Expedited Strategy Briefing on Mythos, Glasswing, and building a security program for what comes next, by 250 CISOs, and the wider community.
It is still a draft, with some design incomplete, but we felt it was imperative to release.
Link:
labs.cloudsecurityalliance.o…
Sergej Epp retweeted

Zero stolen credentials to full AWS admin.
Eight minutes.
CVE to exploitation used to take 18 months.
Now it's under a day.
A SOC analyst isn't losing because they lack tools.
They're losing because the loop is too slow.
#cloudsecurity #CISO @EppSecurity @sysdig
Sergej Epp retweeted

You can now train @physical_int style robots in 1 day for only $5k. Anvil’s devkits have all the hardware, software, controls, cameras, and more ready-to-go. (1/5)
Last week I launched ZeroDayClock.com.
It went viral. Here's why:
One graph. One question.
In 2018, attackers needed 2.3 YEARS to weaponize a vulnerability.
In 2026, they need 1.6 DAYS.
What this means for all of us 🧵

🔴 zerodayclock.com
📉 The Collapse → zerodayclock.com/collapse
📢 Call to Action → zerodayclock.com/call-to-act…
✍️ Signatories → zerodayclock.com/signatories

This isn't a tech problem. It's a market failure.
The people who build insecure software don't pay when it gets hacked. Users do. Hospitals do. Governments do.
No industry in 150 years fixed safety voluntarily. Not aviation. Not pharma.
Software isn't special. It's just late.

Five things to change. Today.
→ Software liability. Builders pay, not victims
→ Secure by design. Enforced, not suggested
→ Patch in hours. Monthly cycles are dead
→ Unleash defensive AI. Regulate insecure software.
→ Assume breach. Build to be replaced, not patched
