


DefCon-UA retweeted

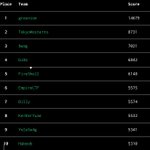
After 12 hours, #HackIT CTF Scorecard stands as following with 'Billy' leading the fray with 3993 points followed by 'KerKerYuan' and 'TokyoWesterns'.
36 more hours to go

We are organizing HackIT CTF 2018, Sep.8 8:00-Sep.10 8:00 (UTC). Please join ctf.hackit.ua/
DefCon-UA retweeted

Use @CHIPSEC to check for firmware vulnerabilities. This vuln can be checked via common.uefi.s3bootscript: github.com/chipsec/chipsec/b…
DefCon-UA retweeted
Extracting NTLM creds from secure VM in Win10 VSM/Credential Guard via FW vuln (see ~31m30s) focus.intelsecurity.com/focu…

Check ctftime.org/ - dcua at the first place in 2016.wow.awesome congratz dcua, you rock. keep it up. thanks @MykolaIlin and othr
DefCon-UA retweeted

Congratz to @LMeteleva and @movcharuk for winning CONFidence 2014 DS CTF!

DefCon-UA retweeted

Hmm, the same MITM technique on iOS from @pod2g at #HITB2013KUL already disclosed year ago at #ZeroNights by @pl0lq slideshare.net/siegin/ios-mi…
DefCon-UA retweeted

warl0ck gam3z @BsidesDC is officially over, congrats to dcua, zorro1 and null for the first 3 places #randomhashtag
DefCon-UA retweeted
@BsidesDC #randomhashtag congrats to player dcua for completing the warl0ck gam3z challenge in 37 hours and 1 minute warl0ck.gam3z.com/bsides


DefCon-UA retweeted
slides "Diving Into IE 10’s Enhanced Protected Mode Sandbox" by @MarkYason Nice stuff! #HITB2013KUL conference.hitb.org/hitbsecc… [pdf]


DefCon-UA retweeted

Exploiting Samsung Galaxy S4 secure boot: blog.azimuthsecurity.com/201…
DefCon-UA retweeted

Slides and articles on dreamboot and security of Android application: goo.gl/Miu7K #SSTIC cc @andremoulu @deesse_k