

Web3 Cybersecurity | $300M+ in Crypto Recovered Security Risk Management, Threat Intelligence, Incident Response
Joined March 2024
- Tweets260
- Following53
- Followers6.5K
- Likes66




Pinned Tweet
Most teams are defending their protocols with yesterday's news.
That’s because today’s available data forces a choice you shouldn’t have to make. The data is either "fast" but lacks real depth, or is "deep" but arrives far too late to matter.
In reality, most of what’s available today isn't fast enough to stop a nation-state actor at the moment of impact, and it’s not as deep as the marketing claims. In this space, if your intelligence doesn’t move at block-speed and isn’t defensible under scrutiny, you’ve already lost.
We aren't just pointing out the gap; we’re closing it.
Starting today, we are offering access to our real-time Threat Intelligence Platform — free for one year. (sign up by March 15th with the link in the comments)
For the first time, you can plug directly into a secure, live stream of zeroShadow intelligence. It is the same human-vetted data our investigators use to track illicit activity and persistent threats, delivered through an architecture that actually moves as fast as the attackers do.
Here is the value we’re bringing to your stack:
• True Block-Speed Intel: Real-time attribution delivered while it’s still actionable, not hours after the bridge is crossed.
• Regulator-Aligned Screening: OFAC+ and OFSI+ extend official lists by tracing sanctioned assets beyond common obfuscation, aligning your screening with investigative methods used by regulators and law enforcement.
• Active Investigative Depth: Direct output from our investigations into nation-state actors (DPRK), drainer networks, and laundering infrastructure.
• Uncompromised Privacy: A secure way to query threat intel without ever exposing your raw data or your strategy.
• Compliance Precision: Dedicated tools that allow CCOs to manage Web3 risk with the rigor of traditional finance.
We are proud to go to market with @lifiprotocol, @1inch, and @megaeth, who are already using this intel to secure their ecosystems.
Register with the link in the comments before March 15th to receive our “Core Data Cars"—including our proprietary zS Investigation leads and OFAC+/OFSI+ tracking—free for one full year.

🚨If you are ever targeted in a wrench attack or threatened with physical violence for your crypto: comply.
Your life is more important than your assets.
Once you are in a safe place, speed is everything.
Call the police immediately, then contact @SEAL_911 on Telegram t.me/seal_911_bot.
Share the transaction hashes and attacker addresses as fast as possible so they can trace the movement and relay the data.
In a recent incident, this sequence made all the difference.
A victim was subjected to a violent robbery and had their funds stolen.
Once they reached safety, they contacted SEAL 911 with the transaction details.
SEAL verified the incident and pushed the attacker addresses directly into TIPzs, zeroShadow's threat intel platform that feeds live incident data straight to exchange screening systems.
Seconds later, the criminals attempted to swap the stolen assets at an exchange.
Because TIPzs pushes threat data to connected platforms in under two seconds, the intelligence landed ahead of the deposit.
The exchange caught the incoming transaction and froze the funds on arrival.
SEAL 911, zeroShadow, the exchange team, and law enforcement are now coordinating to follow the legal process and help the victim recover their assets.
Prioritize your physical safety first.
After that, fast reporting is what makes intercepting and freezing the stolen funds possible.
Thank you to SEAL 911, the exchange team and law enforcement for working together with us and showing how the private and public sectors can work together and do our part to effectively help those who are victimized and deserve all the help they can get.

🧵Bitget suffered not one, but two zero-day exploits during their 24th September hack of $387M USD. Although further details may yet arise, the use of a zero-day exploit shows a growing sophistication in the way that DPRK target victims and extract value. Is Web3 security doomed? [1/3]

We reported the increased use of supply chain based attacks in our March 2026 blog post with Sodot (now @moonpay), noting at least 53 attacks using a third party access point in 2025. That trend has not only continued but grown. Besides Bitget, notable other entry points this year included the HTTP client from Axios in April and Gnosis Pay on Safes in June. [2/3]
Teams should focus on strengthening detection, containment and operational resilience to minimize the impact when preventative controls fail. With these practices in place, you can do a lot to harden your security posture against zero-day threats. Read our blog for specifics zeroshadow.io/blog/bitget-ha… [3/3]

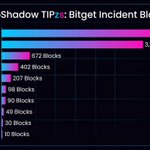
Huge thank you to all our TIPzs network partners who are working around the clock to support Bitget in their hour of need.
This anonymised chart represents thousands of direct blocks executed across our network to help protect the ecosystem. [1/5]

Our friends at Chainflip xitter.cf/SavcatEth/status/21048… and NEAR Protocol xitter.cf/AlexAuroraDev/status/2… have already shared their frontline work.
Seeing engineering teams mobilize to protect Bitget for no financial gain shows what true community defense looks like. [4/5]

TOKEN2049 Singapore 🇸🇬
We're excited to be on the ground for one of the biggest events of the year.
See you there 👋
zeroShadow retweeted

20 BTC returned 🎉
A lot of moving parts between @SEAL_911 @zeroshadow_io @D_A_R_TRescue and an anonymous whitehat who is real MVP here. steptoe.com/en/news-publicat…

zeroShadow retweeted

Compromised by 🇰🇵: December 2024
Telegram taken over: August 2026
Going 20 months undetected is a new record for me. It's crazy how long these guys will wait.
Props to @_clemens__ for spreading the word to protect others 🤝

I have been hacked by the DPRK. Here's how it happened:
In December 2024, a contact that i had met in person several weeks earlier messaged me on telegram asking for a meeting, just like my fake account is now doing. Upon joining the call, the audio wasn't working and then my contact pinged me to update my video call software (Microsoft Teams, which i usually never use), as soon as I clicked that link, my entire device was compromised.
Text book social engineering and urgency in a key moment were all that was needed to get comfy on my device. Although I deleted all files and did several malware sweeps, I did not fully factory reset my device.
21 months later, this piece of malware became active and took over my PC and the result is 8 years of telegram history and contacts now in the hand of a group linked to north korea.
I sincerely hope none of you have tried joining any of the calls with "me" or worse fallen into their trap. A huge thank you to @tanuki42_ who has been tracing this groups activities and has been extremely helpful in getting my compromised accounts deleted after telegram support proved useless.
If you think this couldn't happen to you, here is who you are dealing with: xitter.cf/tanuki42_/status/20975…
securelist.com/bluenoroff-ap…
zeroShadow retweeted

15 firms are undergoing accreditation with SEAL Certifications and taking on audit engagements right now — smart contracts, incident response, treasury security, multisig ops, and more!
If your protocol hasn't scoped an audit yet, reach out directly to a Certification Partner today:
securityalliance.org/our-wor…
@AdevarLabs @audit_wizard @BlockSecTeam @chain_security @Composable_Sec @ConsensysAudits @DefiSafety @hackenclub @HackenProof @SecurityOak @opsek_io @sigp_io @Wonderland @zellic_io @zeroshadow_io

Over 50 BTC from the ColdCard Exploit was rescued by whitehats and was since deposited into the Crypto Recovery Trust, a purpose-built Wyoming statutory trust created and advised by national security attorneys at Steptoe LLP.
If you were a victim of the exploit, please check if your wallet qualifies for recovery via cryptorecoverytrust.com/
Read the full details at
assetrecovery.io/blog/coldca…

zeroShadow retweeted

"We'll publish a full postmortem once the investigation is complete.
And a huge thank you to every partner who jumped in immediately to help us through this: @solana, @raincards, @Helius, @MetaDAOProject, @zeroshadow_io, and @asymmetric_re."

UPDATE: Refunds are processed in full, with an extra 10% cashback.
The Solana contract has been updated. We haven't seen any further related activity, and we're constantly monitoring it.
If your Solana card balance was withdrawn a few hours ago, we've restored the full amount and added 10% cashback on what was withdrawn. Open the app and cross-check your balance.
Here's exactly what was affected and what wasn't:
1. This was limited to card contracts on Solana holding balances added through Avici's Top Up flow.
2. Your regular Avici Solana and EVM wallets were never affected. Those wallets are self-custodial and stayed under your control the entire time.
3. EVM card balances, onramps, offramps, and swaps were not affected.
4. Funds outside these Solana card-balance contracts were never exposed.
We made a very deliberate choice to keep your Avici wallet separate from your card balance. It's why you have to manually Top Up before spending. Combining both would've made the app easier to use, but we didn't do it because we believed keeping them separate was safer.
That separation is why this stayed limited to the affected Solana card contracts while wallets and everything else in Avici stayed untouched. That doesn't make what affected users went through okay. We're sorry for the stress and uncertainty this caused.
We're not proud that this happened. We are proud that Avici is built onchain, where balance movements are immediately visible and independently verifiable instead of hidden behind a private ledger. In traditional fintech, the number shown in an app can stay unchanged while what is happening underneath remains invisible. Here, anyone could see the movement onchain as it happened.
We're pushing the frontier of onchain finance, and that road was never going to be easy. Moments like this are painful and humbling, but they show us what has to improve and will make Avici stronger. We're not stepping back. We're going to keep pushing forward.
Rain, our card issuing partner, covered all reimbursements in full. Huge credit to their team for moving quickly, working closely with us, restoring every affected balance, and fixing the issue.
We'll publish a full postmortem once the investigation is complete.
And a huge thank you to every partner who jumped in immediately to help us through this: @solana, @raincards, @Helius, @MetaDAOProject, @zeroshadow_io, and @asymmetric_re.
Thank you for staying with us through the uncertainty and stress this caused today.

Real time monitoring workflows can vary significantly depending on the protocol type.
• A foundation cares more about bridge inflows and outflows, validator anomalies, and large treasury movements.
• A lending protocol typically cares more about oracle deviation, bad debt, and flash loan driven exploits.
• A trading firm typically cares more about its own wallet activity and the specific contracts it touches.
That's why over the first half of 2026, our team has leveraged multiple products to accomplish these varying engagements:
• @HypernativeLabs: broad, chain-wide coverage with custom agents across EVM and non-EVM networks, plus wallet security for retail and enterprise.
• @TenderlyApp: transaction simulation, state-differential comparisons, and incident war rooms when something needs a closer look.
• @range_org: traces cross-chain and interchain flow, with particular strength on non-EVM chains and stablecoin monitoring.
While these platforms are powerful on their own, the value zeroShadow adds is the fine-tuning underneath: writing custom monitoring in a protocol's own dev language, setting thresholds against its real economic model, and regression testing alerts before they go live.
We wrote up the full breakdown, including how that calibration recently caught a multisig issue before it became a $4M loss.
Read more in our blog below:
zeroshadow.io/blog/blockchai…

zeroShadow, in collaboration with @_SEAL_Org, have identified that the recent AFX Bridge Exploit is highly likely linked to UNC4899 (North Korean subgroup TraderTraitor). Through extensive on-chain analysis, a link has been identified between the gas funding of this exploit to that of the recent KelpDAO exploit. A number of data points were also identified, which are consistent with this threat actor and recent exploits. zeroShadow will continue supporting this research and sharing known illicit address information to help stop the movement of these funds.

UPDATE: Three crypto exploits in a single day, $35.55M in total losses.
@AFX_XYZ: $24.15M
@VerusCoin: $7.55M
@BSquaredNetwork: $3.86M

zeroShadow retweeted

An update on where things stand:
What happened
On July 15, Ostium’s LP (liquidity provider) vault was exploited for 23,752,746 USDC. Based on our ongoing investigation, the attacker compromised off-chain infrastructure related to the system that feeds prices into the protocol. The attacker then submitted illegitimate price reports that were manipulated to appear as valid, opening and instantly closing a series of large positions to extract an artificial profit from the vault. By design, trader collateral sits in a separate, isolated contract and is not affected, with all positions remaining open.
Our response
We are working with Mandiant, zeroShadow, Collisionless, and SEAL 911, alongside law enforcement, and coordinating with exchanges, bridges, and stablecoin issuers. Within 60 minutes of the first exploit transaction, we coordinated to pause trading and freeze all trading contracts. Currently, all of our engineering efforts are focused on isolating and hardening the infrastructure needed to enable a secure re-launch.
What is next
Impacted liquidity providers and the safe resumption of trading remain our top priority, and we are working around the clock towards the path forward. As a reminder, we will give at least 24 hours notice before trading contracts are unfrozen. Upon re-open, trader positions will be marked to the price at re-open, independent of interim price movements.
Please trust only official channels. We will never DM you first or ask for your keys, seed phrase, or funds.
If you have any leads, information, or resources to help with the investigation, reach us at: [email protected].
zeroShadow retweeted

since launching @SEAL_911 on 2 August 2023, we have:
- handled over 4,000 tickets incident tickets
- coordinated over 250 war rooms
- helped rescue more than $200 million
SEAL 911 is powered entirely by _volunteers_ and represents what a true public good can achieve. we're grateful that @OctantApp selected SEAL 911 for Epoch 12. check out (and donate ofc) all of the awesome projects via epoch.octant.app and the SEAL 911 specific link: epoch.octant.app/rounds/0xf9…


We're excited to share Epoch 12: Octant is for everyone.
Allocation window opens at 12:30 pm ET today (16 June) and will close at 11:30 pm ET on 30 June. You can allocate on: octant.app
This epoch marks a few big changes.
This is our first epoch introducing ProperQF.
This is our first epoch with zkproofs in voting.
This is our first epoch open to ETH contributions.
This is our first epoch on v2.
So, let's get into it.
Epoch 12 is our 13th funding round. We’ve got 200 ETH in our matching pool this time.
As a GLM locker, you can allocate your WETH rewards to yourself and/or to projects that are part of this epoch. The matching pool will be quadratically split based on your allocations.
For ETH contributions: 50% of the contribution will be converted to $GLM and burnt, and the remaining 50% will be allocated to your project selection. Part of this is to discourage sybil, and the other part is because our funding comes from @golemfoundation's treasury yield and GLM is core to the mechanism. We will be noting addresses who attempt to sybil and penalize them by removal in upcoming epochs.
We've done a few deep dives on properQF and built a simulator you can use to model the final allocations: qf.octant.app
Now for the fun part. We've got an incredible group of projects joining us in Epoch 12:
@AestusRelay
@BluefilterC
@crypto_altruism
@dappnode
@eas_eth
@ECHInstitute
@etheconomiczone
@ethStaker
@EthereumRemix
@FundingCommons
@GiliEcoTrust
@greenpilldevs
@growthepie_eth
@hypercerts
@l2beat
@OSObserver
@ProtocolGuild
@RevokeCash
@rotkiapp
@SEAL_911
@shefiorg
@ShutterNetwork
@solidity_lang @argotorg
@torproject
@zachxbt
Allocation dates: 16 June - 30 June (11:30 PM EST).
Every allocation makes a difference. Make yours count. Allocate now: octant.app
