
BS-free offensive security tweets. I host @secTalksNL & @securityCTF. Strong exploit dev fetish. Baker of 0days.
The Netherlands
Joined December 2016
- Tweets3.8K
- Following2.5K
- Followers4.8K
- Likes595




No hype & No AI slop:
We launched VibeSecurity.org to help startups and scale ups fix their security posture by identifying what's hackable early on. This is not only AI, but also human guidance on each step.
Sample report available here: vibesecurity.org/sample-repo…
retweeted

Introducing PageBreak, an agentic vulnerability discovery tool using deterministic validation to achieve a near-zero false positive rate.
How it works: blog.google/security/agentic…
For real-world vulnerabilities PageBreak has discovered 👇
bughunters.google.com/blog/p…

Hackers of NL,
this one is for you
As a winner of the previous editions. I highly recommend this contest. It's for a good cause, great way to tap into the community and show your skills.
#netherlands #hacking #infosec

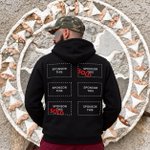
I'm offering sponsored logos on my hoodie while hacking in this contest, which gets a lot of media attention.
send your logo here:
[email protected]
space starting at 499EUR
you can buy multiple
(only 4 left!)
#cybersecurity #netherlands #thehague


each time we send an email to msft email (outlook, azure, etc) their spam filter mark our domain hacktivity.eu as a spam just because it contains "hack" in it.
All other services are OK.
so,
pro tip: if you start a security company don't name it hack-something.

my research paper got accepted to @Bsideslisbon this year. See you there.
teaser: using ai for hacking the physical (red teaming and beyond)
Started as a joke but sold quickly:
Offering 6 places to sponsor your logo on my hacking hoodie. I will be in the biggest cyber security events during the cyber week in #Netherlands with lot of media and attention including One Conference and Hack The Hague
[email protected]


still cannot believe this is a free tool!
find subdomains via SSL certs:
crt.name/
credits: Malvin of @hadriansecurity


Call for Speakers for #DefCamp 2026 is open on Sessionize and I've just submitted a session!
Teaser: It's about mixing the physical security attacks with ai
sessionize.com/defcamp-2026/
@DefCampRO #ro


Made a free tool because we kept getting asked "how do I know if my VPN is actually leaking." One click shows your real IP, DNS, WebRTC and timezone exposure exactly like a website would see it. No account, no catch. chromewebstore.google.com/de…


🤖 Made with AI

@TallyForms , a (>5m ARR) bootstrapped scaleup, got breached just few hours ago. Probably because of an outdated metabase instance.
If you are vibe coding - Please check your security posture as soon as you can. It's definitely not worth it for you to lose your customers trust.
World Wide Worm 101:
1. Shodan WordPress filter: http.component:wordpress (results 50k hosts)
2. Extract the list
3. Pwn via wp2shell poc - github.com/Icex0/wp2shell-po…
4. Let it rain shells <3
Looking for exposure assessment? Hire us at hacktivity.eu
#wp2shell #infosec

Update: I just polished one of the community's favorite libraries on Windows Privilege Escalation for penetration testers and red teamers.
Focused on practical attack paths & real-world privilege escalation techniques seen in my enterprise assessments.
hacktivity.eu/windows-prives…

Can a small, self-hosted LLM outperform state-of-the-art models at evasive malware development?
outflank.nl/blog/2025/08/07/…
credits: @kyleavery, @OutflankNL, @BlackHatEvents
#ai #exploits #offsec

retweeted

New Blog Alert! 🚨
Introducing Early Cascade Injection, a stealthy process injection technique that targets Windows process creation, avoids cross-process APCs, and evades top-tier EDRs.
Learn how it combines Early Bird APC Injection & EDR-Preloading: outflank.nl/blog/2024/10/15/…
