

Digital security insights from a hacker’s perspective
Amsterdam / London
Joined August 2021
- Tweets330
- Following40
- Followers2K
- Likes57





Hadrian retweeted

Manually auditing unfamiliar codebases for security vulnerabilities without a strong methodology can be tedious... 😓
OpenHack by @hadriansecurity is a lightweight, file-based workspace for source-guided whitebox security reviews, helping you systematically trace, annotate, and track vulnerabilities across large codebases! 🤠
Check it out! 👇
github.com/hadriansecurity/O…


🚨 Microsoft has updated its July Patch Tuesday, and among these is the zero-day vulnerability CVE-2024-38112, which enables attackers to spoof web content, deceiving users into interacting with malicious resources.
Additionally, many more vulnerabilities pose an immediate risk to systems. Click the link to read the full list: lnkd.in/drECG2gU
💡 Although there's no proof of concept for this vulnerability and it's only been exploited in lab conditions, a public exploit could emerge soon. It's advised to patch this vulnerability promptly.
👉 Learn how to mitigate this vulnerability in our latest blog: hadrian.io/blog/openssh-vuln…
#CyberSecurity #Vulnerability #PatchNow

🎊 Celebrating one year of the National Anti-Scam Centre! Let's continue protecting ourselves from scams by staying informed and vigilant.
🔒 Stay safe and scam-free!
#CyberSecurity #AntiScam #DigitalSafety
🔥 Fireside Chat: The State of Retail Security Webinar is NOW LIVE!
#HadrianSecurity #CyberSecurity #Retail

🚨Must Know: qTox’s RCE Vulnerability🚨
A critical vulnerability has been unearthed in qTox's latest version 1.17.6, a favored communication platform among malicious hackers due to its anonymity features. But who's gaining the upper hand?
👇 Read Below
🔒 Ethical hackers, armed with newfound knowledge, have seized the opportunity to disrupt cybercrime networks. By leveraging their understanding of RCE, they've dealt a significant blow to malicious actors, hindering their operations.
📈 🎉 As 2024 kicks into high gear, we took some time to reflect on the amazing achievements of 2023.
Thank you to our team, our clients, our investors and advisors.
Here's to surpassing last year's excellence! 🚀
4️⃣ Mass Attacks Targeting Network Zero-Days
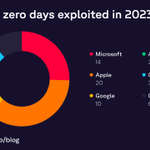
🕑56 #zerodays exploited in the wild in 2023; a notable increase.
Chinese hackers identified as top state-sponsored actors in 0-day usage.
Mitigate risks by promptly patching, monitoring relevant CVE feeds, and optimizing #firewalls.

5️⃣ Accelerating Momentum of Supply Chain Attacks
Software #supplychain attacks rising; diverse methods include typosquatting, targeting open source components and more.
⚠️Software Bill of Materials (SBOM) crucial for transparency and vulnerability checks.
