Reverse engineer / malware analyst. On the hunt for domain generation algorithms. Current side project: https://xitter.cf/t.co/Cv3COq0ZmR

Schweiz
Joined August 2013
Today, I'm releasing the first version of a small web 🚀: rosti.bin.re/ It provides IOCs and YARA rules collected semi-automatically from public blog posts and reports of almost 200 cybersecurity sites. I hope it proves useful to some of you ... 🙏✨ #ThreatIntel
16
123
4
367
32,663
Johannes Bader retweeted
According to @GovCERT_CH , an unknown threat actor has sent out postal letters (yes, *postal* letters ✉️) to recipients in Switzerland that pretend to originate from @meteoschweiz, luring the recipient into downloading and installing a rogue App 🔥🕵️‍♂️ The QR code in the letter leads to a malicious App that impersonating the "AlertSwiss" App of the federal administration. However, the App in fact is a version of Coper (aka Octo2) #malware, infecting mobile phones running Android 📱🤖 Payload delivery URL: 🌐 urlhaus.abuse.ch/url/3290212… Malware sample: 📄 bazaar.abuse.ch/sample/4928c… Coper botnet C2: 🔥 threatfox.abuse.ch/ioc/13448… ➡ ncsc.admin.ch/ncsc/en/home/a…
29
6
76
27,603
What's happening? #FlareOn11 is happening! Time to update #BinaryRefinery and snag some flags! ✨ github.com/binref/refinery/ ✨ flare-on11.ctfd.io/challenge…
17
46
5,035
Johannes Bader retweeted
We're proud to be a @Quad9DNS partner, helping make the Internet a safer place!
4
1
13
5,940
Could you please share your IOCs in any format that is NOT low screenshots @Cloudflare 🙏? blog.cloudflare.com/disrupti…
1
1
396
Johannes Bader retweeted
Nice #MooBot botnet caught by @banthisguy9349 😂 Botnet C2 domain: 🔥 putin.zelenskyj .ru Pointing to: 45.88.90.30:43957 (AS203168 Constant MOULIN 🇧🇪) DNS resolution provided by Cloudflare 🔎 Payload URLs: 🌐 urlhaus.abuse.ch/host/45.88.… Payload: 📄 bazaar.abuse.ch/sample/21f1c…
4
8
3
31
10,437
Johannes Bader retweeted
I wrote a blog post about MalpediaFLOSSed, a collection of ~4 million strings extracted from 1800+ malware families and upgrading its GUI plugin to work with IDA, Ghidra, and Binary Ninja at once! Kudos to @hyun____22 for Hyara, which pioneered such cross-tool compatibility!
1
31
87
13,337
Johannes Bader retweeted
3
1
2
869
Johannes Bader retweeted
I wrote a short blog post on MCRIT, the one-to-many code similarity analysis framework that we released as open source recently at @Botconf.
[blog post] MCRIT: The MinHash-based Code Relationship & Investigation Toolkit danielplohmann.github.io/blo…
1
23
37
4,749
#BinaryRefinery 0.5.10 can deobfuscate this sample with little effort. Only had to add one new unit for StrReverse constant folding. Not a silver bullet, obviously, but why write those regular expressions yourself when you can make me do it for you?
CyberChef for Malware Analysis - DCRat Loader youtube.com/watch?v=rpp6BZYI…
1
5
14
2,678
Johannes Bader retweeted
🛠️ .NET malware decompiling challenges: Obfuscations of strings/constants can be tedious. Automate w/ IDA Pro's Python 🐍 interface for MSIL binary patching, even for simple cases: threatcat.ch/blog/undo-dotne… #CyberSecurity #MalwareAnalysis #IDAPro #DotNET
26
1
85
11,235
Johannes Bader retweeted
New video on the Domain Generation Algorithm of the file infector m0yv. We've sinkholed multiple domains & show how infections dramatically increased in the last 400+ days 📈. #m0yv #DGA youtu.be/3RYbkORtFnk
1
5
6
1,447
Johannes Bader retweeted
Just updated the "malwarebazaar" Python module to include a Python and CLI client for @abuse_ch #YARAify and added a "richer" output. You can find it on Github (github.com/3c7/bazaar/releas…) and on PyPI (via "malwarebazaar"). #threatintel #malware
2
33
111
16,532
Johannes Bader retweeted
Fortinet released security updates for FortiOS to fix a heap-based buffer overflow vulnerability (CVE-2022-42475). Apply patches asap. Read more at: go.dhs.gov/Z8v
1
48
9
70
Johannes Bader retweeted
We published a tech paper on the #ConfuserEx obfuscation mechanism of a Ginzo .NET sample. This class of obfuscator is known as code flatteners. We describe how it can be dealt with using a Python script + IDA Pro Blog: 👉govcert.ch/blog/unflattening… Paper: 👉govcert.ch/whitepapers/unfla…
1
114
1
286
Replying to @chrissanders88
Since there's probably a few big CyberChef aficionados here, I'll go ahead and pitch my little rival project, the binary refinery: 🏭 github.com/binref/refinery/ It's (almost) like CyberChef, but it's a cross platform command line toolkit.
3
20
2
51
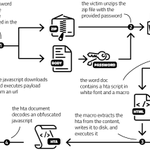
New blog post: Analysing TA551/Shathak malspam with binary refinery bin.re/blog/analysing-ta551-… I show how the open source framework "binary refinery" can be effective in analysing multistage TA551 malspams with encrypted ZIP, Word document, HTA and Javascript.
1
64
1
194
Domain Generation Algorithms are straightforward to program and usually bug free. Not so the new #DGA of #BazarLoader, which goes haywire during the summer months: bin.re/blog/a-bazarloader-dg…