

Reverse Engineering & Game Hacking Courses @ https://xitter.cf/t.co/Dl5ED4o7YS
USA
Joined January 2013
- Tweets5.5K
- Following418
- Followers59.1K
- Likes5K





Pinned Tweet
🎙️ GH Podcast: Former Roblox Hacker Interview
What makes a hacker quit cybercrime?
In this interview, a Roblox exploiter breaks down his pivot from black-hat hacking to creating ethical reverse engineering tutorials at Guided Hacking.
👉 youtube.com/watch?v=Scp7XQbk…


I've tried networking in this niche for 12 years & I've only had 4 positive experiences:
@_xeroxz
@zebleerguy
@usetraceix
@GameHackingGG
Everyone else has scammed, talked shit, or been so fake that it was impossible to work with them.
Shoutout to the genuine people, in a world of fakes!

🧠 Best Sources for New Malware Samples
Stop analyzing dead binaries. Free platforms like URLhaus give researchers access to active distribution feeds and fresh payloads for reverse engineering.
👉 youtube.com/watch?v=Hml4eOCV…
🧠 How Secure Boot & TPM 2.0 Power Anti-Cheat
This guіdе еxplains exactly why Secure Boot and TPM are mandatory, breaking down remote attestation and the hardware-level trust anti-cheats use to stop cheaters.
👉 guidedhacking.com/threads/th…

📱 Frida for Android: Bypassing Root Detection
🔑 Learn the common root detection methods (SU binary, package checks) and how to defeat them at runtime by creating custom Frida scripts that modify function return values
👉 guidedhacking.com/threads/fr…

GuidedHacking retweeted

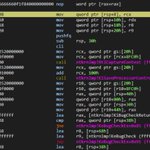
I can independently verify these results are semi-correct. However there are a lot of issues with this output. I will cover it in this thread 👇
This binary is protected with CodeVirtualizer for context.
(Proper devirt on the left, vs AI on the right) func: 0x237F0


Devirtualized Easy Anti-Cheat (EAC) for Linux via Gemini 4 Argon and GPT 6.1 Sol using Hex-Rays IDA Assist's MCP: github.com/19h/eac-linux-dev…

🪲 Learn Malware Analysis
👉 guidedhacking.com/forums/mal…
Unpacking VMProtect
Unpacking Packed Files Series
Setting Up CAPEV2 Sandbox
Unpacking PECompact
Practical Malware Analysis Exercises
Unpacking FlawedAmmyy
Unpacking ASPack
Malware Analysis VM Setup
Top 5 IDA Pro Plugins for Malware
Gootkit Decryption with Python
Removing Obfuscation in IDA Pro
Top 5 Malware Analysis Websites
LimeCrypter Analysis: Crypter Internals
Reverse Engineering Go Binaries
StormKitty C# Stealer Analysis
Rebuilding IAT for Malware Analysis
Unpacking Ramnit Dropper
Best SysInternals Tools for Malware
Writing YARA Rules
ChatGPT for Malware Analysis
Dumping Malware at OEP
CyberChef for Malware Analysis
Downloading New Malware Samples
CyberChef: DCRat Loader Analysis
Dumpulator for Malware Analysis
Miasm Python RE Framework Intro
API Monitor for Malware Analysis
Process Monitor for Malware Analysis
BlackNET C2 with FakeNet-NG
Unpacking YouHacker & Python Malware
Beginner Malware Traffic Analysis
VKeylogger Analysis: Dumping & Fixing Imports
Beginner Malware CTF (CyberDefenders RE101)
Miasm: Symbolic Execution
Finding Malware C2 Panels
Malware Persistence Techniques
Redline Infostealer: C2 Analysis
Mallox Ransomware Analysis
Windows Defender Bypass (Token Manipulation)
Binary Refinery Tutorial
WhiteSnake Stealer Analysis
CAPA for Malware Analysis
Comparing Binaries with BinDiff
APT37 RokRAT Analysis (North Korea)
Learning Malware Analysis (Beginners)
Paradies Clipper: Crypto Jacker Analysis
Reverse Engineering Skid Malware
CrashedTech Loader Analysis
Fileless Malware on Linux via Scripting
File Type Identification Tools
KLBanker String Decryption with Python
Miasm: Basic Syntax
Detecting Manual Mapping in Memory
BlackGuard Infostealer Analysis
Malware Analysis Learning Resources
Miasm: Jitter
PE-sieve for Malware Analysis
Detecting Process Hollowing
Finding Shellcode in Malware Memory
LockBit Ransomware KillChain
LockBit: Extracting Binary from XLL
PolyGlot Files & IcedID Evasion
Malicious OneNote Documents (AsyncRAT)
Popular UAC Bypass Techniques
VFlooder: VirusTotal Flooder Analysis
Popular Windows Malware Analysis Tools
ProCDOT for Malware Analysis
pySMT Deobfuscation via SMT Solver
Back-Doored RedLine Targeting Skids
CapLoader for PCAP Analysis
RedLine Targeting YouTubers
Analyzing Office File Malware (Oletools)
Top 7 Malware Detection Techniques
Regshot for Malware Analysis
Detecting DLL Side-Loading
Detecting C2 Servers
Scanning Memory for Malware
Threat Intelligence in Malware Analysis
DoNex Ransomware Analysis (Malcore)
IcedID / BokBot Banking Trojan Analysis
Analyzing Malware Stager Techniques

GuidedHacking retweeted

If you wanna learn game hacking/just experiment i must say, guided hacking is such an amazing resource! highly recommend and congrats on reaching 200k you deserve it!


The people who blame the anticheat when they get banned for hacking games, are the same people who blame us when they get banned for trying to hack our website.
🛠️ GH Unreal Engine Decompiler
🎯 One-Click Decompiling of Entire Games
🔌 Seamlessly Integrated with Cheat Engine
🔗guidedhacking.com/threads/gh…
🧠 How To Dump Virtualized Anti-Cheat Drivers
When an anti-cheat driver blocks debuggers, standard dumping methods fail. Learn how to configure your system and extract the protected driver for offline analysis.
👉 guidedhacking.com/threads/ho…

📚 Master Android Analysis: The Frida Framework
🛠️ We cover setup, function interception, native library manipulation, and Root Detection Bypass. The essential series for serious Android reversing beginners.
👉 guidedhacking.com/threads/fr…

🧑🔬 Steady progress on the GH Devirtualization Course
Made by a real human who learned how to do it. Not AI generated BS.
🔗 guidedhacking.com/forums/dev…
