

Security Engineer @ Meta, London | Ex - SAP l Bug Bounty Hunter | Security+ | CRTP | Learning and Sharing everything Security
London, England
Joined September 2024
- Tweets374
- Following106
- Followers5.5K
- Likes1.4K




Deev Pal retweeted

A great example of someone who is willing to put in the work.
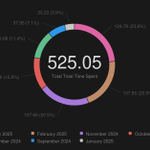
255 hours, and he's already popping 4 digit bugs. The first is always the hardest.

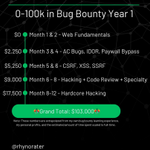
0-100 in Bug Bounty with a 9-5 job
Finally, after 125 Hours of Rigorous testing in 56 days of starting bug bounty from scratch, I received my first bounty that too in 4 digits, in the main domain of one of the largest Public Bug Bounty Programs
Way more to go!!!!!
@Rhynorater


Deev Pal retweeted

I have pushed 3 massive updates to my course since July to include more labs/videos on SSRF, RCE, ATO, 403/401 Bypasses, and more! 🧑🏽💻
👀 I'll give away two free vouchers to two people who retweet and reply with 'RCE' under this post!
ℹ️ More info 👉🏼 bugbounty.nahamsec.training
