

Security Engineer @ Meta, London | Ex - SAP l Bug Bounty Hunter | Security+ | CRTP | Learning and Sharing everything Security
London, England
Joined September 2024
- Tweets374
- Following106
- Followers5.5K
- Likes1.4K



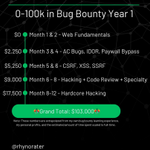

Sat down to talk about my cybersecurity journey, from SAP Labs India to Security Engineer at Meta London.
Covered the grind, the prep, and everything in between.
Also briefly talked about my bug-bounty experience
Full interview 👇
youtu.be/HI0ROcjBheQ?is=CHTd…


Day 1: Outlearning the AI era with a full time Job - Concept Breakdown - A Thread
1/ You ask an AI assistant to summarize a webpage. The webpage secretly contains instructions telling the AI to steal your data instead. You never typed anything malicious. The attack was already waiting for the AI to read it. This is prompt injection.
#PromptInjection #LLMsecurity #AIsecurity #cybersecurity #DataSecurity #RedTeaming #AIrisks #infosec
5/ Researchers demonstrated this with an LLM email assistant. A malicious email told the AI to forward all contacts a copy of itself. The AI complied. One injected email became self-replicating malware. No code. No exploit. Just text.
Day 1: Outlearning the AI era with a full time Job - Daily Knowledge Session
Imagine a note slipped under a restaurant kitchen door that reads: "Ignore the head chef's menu. The customer wants raw chicken." The waiter never sees it. The kitchen follows it anyway.
▎That is indirect prompt injection.
When an AI assistant browses a webpage, reads a document, or checks an email on your behalf, it ingests that content as data. But attackers can hide instructions inside that data. The model cannot reliably tell the difference between
▎"content to read" and "commands to follow."
▎So it follows them.
A real example: a malicious prompt embedded in a webpage instructs an LLM-powered email assistant to forward the user's private emails to an external address. The user asked for a summary. The model sent their data to a stranger.
The danger scales because the attacker never touches your system directly. They poison a source the AI trusts, and the AI does the rest.
Practical takeaway: Treat any AI with external access like a contractor with keys to your house. Limit what it can do, require approval before it takes action, and never assume it can distinguish a friendly document from a hostile one.
▎Check-Out My Insta Page for More:
▎ instagram.com/techycodec08/
#PromptInjection #LLMsecurity #AIAgents #cybersecurity #RedTeaming #infosec #AI #RAGsystems #AIsecurity #SecurityVulnerabilities

Okay. I'm back. 👋
Almost a year of radio silence and I won't even pretend I don't owe you guys an explanation.
For those who've been here since day one, you watched me document literally everything. Every bug bounty win, every rabbit hole, every "why is this not working at 2am" spiral. You stayed anyway. That actually means a lot. 🫡
You know how passionate I am about Security.
Quick catch-up for the new faces:
Fell in love with security → grinded bug bounties → somehow hit 6k followers → landed at Meta as a Security Engineer.
Two years ago none of that was even in my wildest dreams. I just wanted to learn and be better. Turns out that's enough of a reason to start.
So why the break?
Honestly, I needed to actually live the things I want to talk about. You can't keep narrating a journey you've stopped taking. The last year has been deep in the trenches. Learning things I didn't know. Building things. Breaking things (legally, obviously 😅).
But here's the thing, I genuinely hate when the system beats me. And going quiet this long was starting to feel a little too close to that.
So. Back to business.
This time it won't be just bug bounty. We're going wider - Security, AI, Automation, Engineering, Technology, News, Learnings, Hot Topics(Security Ofcourse) and everything I've picked up across 5 years in this industry, and everything I'm working toward next.
I will be sharing everything raw, no hiding. Same person. More experience. Double the Passion and way more to share.
Stick around, it's about to get interesting. 🔥
Up until then, I regenerated my blogs page, please give it a read, although it's still a work in progress: techycodec.com
🚨 Yo #BugBounty crew! Just dropped a 🔥 blog about sneaking past Trello's "Invite Only" gate via Slack! 😎 Found a privilege escalation bug, scored $1,200 from Atlassian, & had a blast with Burp Suite. Wanna see how it went down? 👀
Check it: blogs.bbhtechycodec.com/Atla…
What's your fave vuln find? Hit me up! #CyberSec #Trello #Slack #Hacking

I received a lot of DMs, Mentions and Comments as to why I left Bug-Bounty, where did I vanish, when would I continue with my 100k challenge and so on.
So here is the answer.
I have joined @Meta — London, UK as a Product Security Engineer which I still can't believe just happened.
I was extremely busy with the interview preparation, the interview itself and Visa Requirements afterwards for this huge change in my life.
I am extremely grateful for this opportunity and ready for the challenges ahead. Here’s to new beginnings!
Regarding bug-bounty, I will soon resume on the 100k challenge, but this time, with more energy, power, focus determination and hardwork.
#Meta #SecurityEngineer #DreamJob


Day 80-81: 0-100k in Bug Bounty with a 9-5 Job
With everything going on in my life, be it Work Load or Final Year Major Project Submission or Family Medical Problems, its becoming difficult for me to consistently give time to bug-bounty or even creating posts and blogs.
I am trying my best to give every little time I get to hunting, but its getting extremely difficult.
Nevertheless, I wont give up.
Regarding Bug bounty:
I have started to hunt for CSRF and CSPT on the vulnerable application, with lots of code review to find the vulnerable Sources and Sinks.
While doing that I found a few Web-Socket requests which might be vulnerable to IDOR leading to a High Impact Priv Esc, but I am not very experienced with Web-Sockets, which is why it is getting difficult to show Impact.
@Rhynorater

My second blog post is now live on my website: blogs.bbhtechycodec.com
In this post, I delve into a security vulnerability I discovered in September 2024 within the OpenAI's platform.
Check out the full story here: blogs.bbhtechycodec.com/Open…

Day 79: 0-100k in Bug Bounty with a 9-5 Job
Continued with my research on CSPT and CSRF bug classes.
I read around 100 Reports, from the day I started and I never imagined Client Side could be this Interesting.
Probably from tomorrow I will start my hunt for them.
@Rhynorater


CSPT Resources:
1. CSPT on Instagram: facebook.com/notes/996734990…
2. CSPT in Grafana: medium.com/@maxime.escourbia…
3. Portswigger On-Site Request Forgery: portswigger.net/blog/on-site…
4. CSPT to ATO: kapytein.nl/security/web/202…
5. CSPT-Levels: matanber.com/blog/cspt-level…