

Assess the security of your HTTP response headers. Powered by @probely, created by @Scott_Helme.
Earth
Joined May 2015
- Tweets276
- Following3
- Followers5.1K
- Likes361

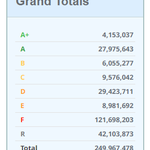
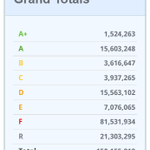

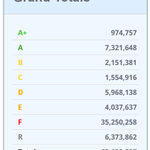
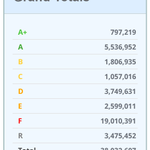
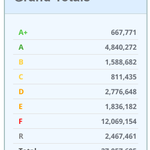
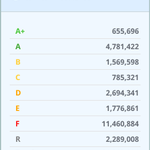
For the first time in a long time, we've just updated our Grading Criteria.
You can read the full details from our founder, @Scott_Helme, over on the @probely blog:
probely.com/blog/a-balanced-…

Security Headers retweeted

This is something I've wanted to dig into for years but I've just never had the time to do it!
A deep analysis into the @securityheaders scan data, now possible thanks to our partnership with @probely 😎
probely.com/blog/unveiling-t…

Did somebody say Security Headers?! 💙


Security Headers retweeted
Can anyone tell me the story behind the HSTS max-age value on Amazon? 🤔
There’s got to be a reason behind that! @amazon @AWSSecurityInfo @securityheaders
securityheaders.com/?q=amazo… – at San Francisco, CA
We’re at @BlackHatEvents with @probely! 🔒
Stop by booth #1486, try out a free scan of your website, grab some cool swag and meet our founder @Scott_Helme 😎
prbly.us/3Ow4qNi

Since our inception, we've now conducted 250,000,000+ scans!!! 🎉🥳🔒🌍💙
scotthelme.co.uk/celebrating…


We're happy to announce that Security Headers will be joining @probely! Read more from our founder, @Scott_Helme, in his blog post: scotthelme.co.uk/security-he…

Security Headers retweeted

Come and find us at @NDC_Conferences Oslo for our first ever vendor exhibit!
Meet our founder, see a product demo, enter our hacking competition or watch our artist create your swag live on the stand! It's going to be epic, we'll see you there 😎 report-uri.com/event/ndc_osl…
Security Headers retweeted
Safari 16.4 is bringing support for the Reporting API! This means reports can be sent out-of-band asynchronously, and, we’re getting some new reports too.
✅ Reporting API
✅ COEP violation reporting
✅ COOP/COEP nav violation reporting
webkit.org/blog/13966/webkit…

Security Headers retweeted
A few people reached out to say they couldn't get their corporate card or approval in time so I've extended this code for another 7 days!
Apparently when you work for a company there's like "processes" and stuff! Who knew?! 😅
Use 15FORLIFE at checkout to get 15% off for life!!
Security Headers retweeted
It's finally here!!! The @securityheaders API 😎
Launched right here, right now, at @NDC_Conferences #ndclondon 💪
scotthelme.co.uk/announcing-…

Security Headers retweeted
This is really interesting research and I wanted to know if I could expand upon it using Content Security Policy and reporting via @reporturi. I've just created inappbrowsercsp.com/ to do exactly that!

🔥 New Post: Announcing InAppBrowser - see what JavaScript commands get injected through an in-app browser
👀 TikTok, when opening any website in their app, injects tracking code that can monitor all keystrokes, including passwords, and all taps.
krausefx.com/blog/announcing…

Security Headers retweeted
I'm considering changing the grading criteria on @securityheaders to allow an A+ grade with a CSP that contains unsafe-inline in the style-src directive. What are your thoughts?
37%Yes, allow A+
25%No, keep as it is
38%Show results
436 votes • Final results
Nope, no caching. For generating a CSP I would recommend the CSP Wizard by @reporturi: docs.report-uri.com/setup/wi…
150,000,000+ scans?! A huge thanks to our sponsor @probely who have supported us through this milestone and made it possible!
😱💪🔥🎉❤🌍🔒

We're *fast* approaching 150,000,000 scans!!! Big thanks to our sponsor @probely, who continue to support us and make this all possible 🤩