

Client-side security to control what code actually runs on your website.
Earth
Joined April 2015
- Tweets636
- Following4
- Followers3.8K
- Likes609





Criminals posed as a children’s charity to hide a card skimmer.
The site looked like a non-profit, but it was serving malicious code that stole checkout data from WooCommerce shops.
Here’s how the operation worked: blog.report-uri.com/criminal…

We found a ClickFix kit with a debug flag left in production!
On a Mac, adding the ?force_fake_captcha=1 GET param skips most of its checks and reveals the fake CAPTCHA lure.
Even the criminals need to debug their code 🥷
blog.report-uri.com/clickfix…

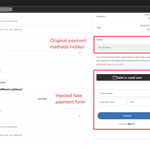
A fake Stripe card form can appear inside a real checkout. Shoppers enter their details, the order still goes through, and the attacker gets the card and personal data.
We found this Magecart kit active on dozens of WooCommerce, PrestaShop and Magento shops.
Here’s how it works: blog.report-uri.com/the-fake…

A new ClickFix kit only shows its fake reCAPTCHA to first-time Mac visitors. It hides from bots, Windows, Linux and mobile.
Unless you add ?force_fake_captcha=1 to the URL.
Even the criminals need a debug mode 🙃
An abandoned analytics tag, a re-registered domain, and store visitors funnelled to a DarkSword iPhone exploit.
We traced the chain from a forgotten script to an exploit kit and spyware payload.
When did you last audit your third-party scripts?..
blog.report-uri.com/abandone…

A fake CAPTCHA, a trojanised file manager and a new C2 domain every Thursday.
We traced a ClickFix campaign and recovered its DGA, letting us predict future C2 domains.
Here’s the attack chain and the IOCs defenders can use 👇
blog.report-uri.com/a-fake-c…

A magecart actor we’re tracking has spent the last 48 hours rotating to a new exfil domain registered 3 days ago.
New IOC: selnor[.]fun
We've identified a modified strain of a Magecart skimmer and the count is up to almost 800 sites infected.
The injected JS races to replace the standard payment options with a new payment form that exfiltrates data.

☠️IoC list for defenders:
specterguardian\.com
solutionjquery\.com
assetsbundle\.com
safeprocessor\.com
gtmtimestamp\.com
doubleclickcache\.com
websitewebcache\.com
explorerbrowser\.com
review-cdn\.com
safeprocessmaster\.com
One suspicious domain led us to 2,000+ compromised WordPress sites, a fake reCAPTCHA lure and a macOS infostealer targeting crypto wallets, browser cookies and Keychain data.
We traced the campaign to sanctioned Russian infrastructure and published the IOCs:
blog.report-uri.com/chasing-…

We’ve rolled out Device Bound Session Credentials to 100% of Report URI logins. 🔐
67.7% of our active sessions are already device-bound, making this what we believe to be one of the first production DBSC deployments outside Google.
Here’s how we did it:
blog.report-uri.com/we-rolle…

Report URI retweeted

⚡ @ReportURI browser alerts caught a ClickFix campaign before some reputation services did.
CSP reports from compromised e-commerce sites exposed attacker-controlled domains used in a chain that copied PowerShell commands to victims’ clipboards.
How the attack surfaced: thehackernews.com/2026/09/an…

We deployed an update at 14:00 UTC that introduced a new JavaScript dependency.
At 14:04 UTC, Script Watch alerted us to it.
That is the visibility you need in the browser: know when new code appears on your site, whether the change is expected or not.
Four minutes from deployment to detection! ⏱️


Magento has shipped with CSP enabled by default since 2.3.5, but most stores never configure a reporting endpoint. We found 2,236 Magento sites taking card payments with this exact gap, so we built a free module to fix it:
blog.report-uri.com/magento-…

Dependabot alerted us to a DOM XSS vulnerability in the software behind our own documentation site.
We developed a working PoC to understand the risk, but when we tested it against production, our CSP blocked the injected JavaScript and Report URI captured the evidence.
blog.report-uri.com/how-repo…

Our logo's in good company this weekend. 🏁
Will Orton & Jessica Hawkins go into Donington Park leading British GT4! 😎
Proud to back the #21 Aston Martin.
MK Racing @AMR_Official
#BritishGT #GT4
🤖 Made with AI


Do you know exactly what JavaScript ran in your users’ browsers?
We fingerprint every executed script, alert when something changes, and preserve a verified copy for investigation.
Zero code on your page.
blog.report-uri.com/we-can-p…
