
Founder of @melapresshq
Wijchen, Nederland
Joined February 2008
- Tweets2.4K
- Following70
- Followers468
- Likes3.2K




Is it still worth learning tools such as WP-CLI in the age of AI and agentic tools?
Everyone is talking about how #AI can automate everything, so why bother learning the tools?
Last week, I discussed this with Marcel Tanish on the Melapress #podcast . Marcel highlighted the truth that many people tend to ignore: AI agents can also make mistakes, especially when they lack context or the user doesn't fully understand what they're asking the AI to do.
How did Marcel come to this conclusion? He has years of experience using WP-CLI to manage complex WordPress websites, and he's seen this happen firsthand.
The key takeaway is that AI can do the work for you, but that doesn't mean you shouldn't understand what it's doing.
A very interesting discussion, especially if you're increasingly using AI to manage your #WordPress websites.
#wpcli

AI can generate WP-CLI commands, but do you know what they actually do?
In episode 61 of The Melapress Show, @robertabela and Marcel Tannich discuss WP-CLI, troubleshooting WordPress issues, automation, and using AI safely.
🎥 Watch the full episode:
As promised, here's a short video showing how easy it is to migrate from the discontinued Wordfence Login Security plugin to WP 2FA.
With the new importer in WP 2FA 4.2.0, users are automatically migrated the next time they log in, together with their existing 2FA settings and backup codes.
No downtime, no need to set up 2FA again.
If you prefer written instructions, we've also published a step-by-step guide covering the migration process, how to monitor its progress, and when it's safe to remove the old plugin:
> melapress.com/support/kb/mig…
If you missed our panel discussion about this year’s #WordPress Security Survey, you are missing out.
A few days ago, we hosted the discussion with @kathyzant, @danielebesana, @stealthcopter, and Thomas Raef. They all approach website security from different angles: governance, hacked website cleanup, application security, bug bounties & malware.
That meant we could go beyond the survey numbers and discuss how the findings compare with what they actually see in practice.
Here is the panel discussion --> xitter.cf/melapressHQ/status/210…
If you would like to see the 2026 WordPress Security Survey results before listening to the panel discussion, you can find them here --> melapress.com/wordpress-secu…

What does the state of WordPress security look like in 2026?
Tomorrow, we’re publishing a recorded panel discussion with @robertabela, @WeWatch, @stealthcopter, @kathyzant & @danielebesana on the findings of the 2026 Melapress Security Survey.
🕓 Save the date: Sept 29, 16:00 CET
#WordPress #WordPressSecurity #Cybersecurity #MelapressShow

I'll be speaking at @CMSconf_ in Gdynia this November!
I’m looking forward to meeting new people from other CMS communities, but also to catch up with familiar faces from the #WordPress community, all of whom will be speaking; Mike Miler, @Bovelett, @rmelogli, @RaitisSevelis, @DjevaLoperka, Marcel Bootsman, and many others.
I'll also be giving a talk about WordPress session hijacking, and why securing the login process alone isn't always enough.
If you're attending, come say hello!
And if you haven't booked your ticket yet, you can get €30 off your ticket with this coupon code: CTRL-ALT-DISCOUNT.
#CMSConf #WordPress #WordPressSecurity

Earlier this week we released WP 2FA 4.2.0. It includes a number of improvements and bug fixes, as well as a security fix.
However, the main addition is an importer for Wordfence Login Security.
Wordfence Login Security, a free 2FA plugin, was discontinued a few weeks ago. We don't want users to be left without #2FA, so we've built an importer to make moving to WP 2FA as straightforward as possible, without any downtime.
If you're using Wordfence Login Security, simply install WP 2FA. It will automatically detect the plugin and prompt you to start the migration.
Users are migrated together with their backup codes, so they don't need to configure 2FA again or change how they log in. From their point of view, everything continues working as normal. No user action is required.
Administrators can also follow the migration progress and see how many users have already been migrated.
You can install the free edition of WP 2FA directly from your WordPress dashboard. Go to Plugins, click "Add Plugin", search for "WP 2FA", and install it.
Once activated, follow the step-by-step wizard.
If you need help with the migration, we're also offering one-to-one email support to free edition users until the end of this year.
Don't leave your #WordPress #website users without 2FA. Keep your website secure.
Four in five #WordPress developers in our 2026 Security Survey had experienced at least one known security incident. Of those, 72.2% had experienced two or more.
That doesn't mean 80% of WordPress websites experience security incidents. Developers often work across multiple websites, and some are brought in specifically after a website has been compromised.
What it does show is that security incidents are something many WordPress developers face in their work, even when they know what they're doing.
We've analyzed the findings in our new Developer Security Benchmark:
melapress.com/wordpress-deve…


WP Activity Log has changed a lot since I first started working on it back in 2013.
What started as a side project is now our main plugin at @melapressHQ, with far more features, settings and options.
Now we're working on its next big change: a completely new UI.
We're at the beta stage and I'd really like feedback from our customers and free plugin users, before we go further and finalize the new UI.
If you'd like to test it, email me at [email protected] and I'll send you the latest beta.

Tomorrow's episode of the @melapressHQ
Show is about something we all agree is important, yet often leave until later (or never gets done): documentation.
I'm joined by @DjevaLoperka, a long-time #WordPress #documentation contributor. Milana sees documentation as part of the engineering process, not something you write once development is finished.
I agree with her, even though unfortunately I don't always follow that approach myself.
During this episode we couldn't not talk about AI, the FAIR project, and Doc2Me, a project Milana started at the CloudFest Hackathon to explore automating some of the repetitive parts of software documentation.
Documentation might not be the sexiest thing on the internet, but when you tried a new software or needed to do something at a new job and it was missing, you definitely noticed.
If you can relate, then watch the episode which will be streaming tomorrow at 16:00 CET / 10:00 AM Eastern.
🗓️ New Melapress Show episode: tomorrow at 4:00 p.m. CET
In the next episode, @robertabela speaks with @DjevaLoperka, a WordPress Documentation Team representative and WordPress Engineer at XWP, about why code alone is not enough and how documentation can become a more natural part of the software development process.
They also discuss:
▫️ Why good documentation is never really “finished”
▫️ Why documenting decisions can save time later
▫️ How WordPress handles documentation during release cycles
▫️ Where AI can actually help with documentation work
How can teams make documentation easier to maintain and more useful over time? Watch the full conversation tomorrow at 4:00 p.m. CET. 🙌

Today at 4PM we’re streaming our panel discussion about this year’s #WordPress Security Survey results.
This year we brought together people who see security from very different angles: @kathyzant, @danielebesana , @stealthcopter, and Thomas Raef.
Between them, there’s more than 30 years of experience in WordPress security, governance, hacked website cleanup, application security, bug bounties, & malware.
The mix of penalists' experience made for a very interesting discussion; people discussing the same numbers but from a different perspective.
If you would like to read the survey results before listening to the panel discussion, head to melapress.com/wordpress-secu…
Link to the panel discussion in the tweet below.

What does the state of WordPress security look like in 2026?
Tomorrow, we’re publishing a recorded panel discussion with @robertabela, @WeWatch, @stealthcopter, @kathyzant & @danielebesana on the findings of the 2026 Melapress Security Survey.
🕓 Save the date: Sept 29, 16:00 CET
#WordPress #WordPressSecurity #Cybersecurity #MelapressShow
I had a very interesting discussion with @kathyzant on the latest @melapressHQ Show.
Kathy has years of experience in WordPress & #security, including working with the likes of Wordfence and SolidWP, so we covered quite a lot.
One important point that we discussed: your website doesn't need to be popular to be a target. Attackers often want the server resources behind it, not your brand. And now, with WordPress websites increasingly connected to AI services, they can become an even bigger goldmine, and therefore a bigger target.
We also discussed session hijacking, AI connectors, API keys, prompt injection, least privilege, and why AI doesn't replace good security governance or human oversight.
If you manage #WordPress websites, this episode is well worth a listen.
Watch here --> xitter.cf/melapressHQ/status/210…
Even a low-traffic website has server resources that can be used to send spam, redirect visitors, distribute malware, or support other attacks.
In episode 59, @kathyzant explains why every WordPress website has value to attackers and what small businesses can do to reduce the risk.
Watch the premiere today:
xitter.cf/i/broadcasts/1lJQRWAgn…

A full new UI for Melapress Login Security is coming, similar to the one we recently released for WP 2FA.
In the meantime, version 2.4.0 already makes #policy management easier: #password, user session, device & login policies are now separate groups that admins can enable or disable independently.
Stay tuned and follow the @melapressHQ account to get notified when the new UI is available.
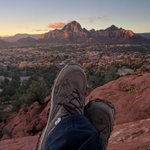
In 2017, I visited Sedona with my friend Dan.
At the time I was working almost full-time at Netsparker, WP Activity Log was still a side project, I had two children, and I wasn't sure whether the plugin would ever become a proper business.
A few weeks ago I visited Sedona again. This time I was in the US for @WordCampUS, @melapressHQ has grown into a team of eight, and I now have three children. My US trip partner in crime, @adispiac from @TranslatePress suggested we rent a car and visit the Grand Canyon and Sedona, so we did.
Seeing the same place again nine years later was a bit strange.
There isn't some big business lesson behind it. It simply reminded me why I left my job in the first place: I didn't know whether Melapress would work, but I knew I didn't want to keep wondering what would have happened if I'd tried.
Sometimes you have to find out. So if you have a dream, if you want to do something, as we say in mountain biking, just send it!
My thoughts: robertabela.me/sedona-nine-y…


There’s an interesting contradiction in our 2026 WordPress Security Survey.
Security concern is very high: 7.85/10 on average, with 37.5% rating it a full 10/10.
Yet only 27.9% have a breach recovery plan, only 26% provide team security training, and 37% of those concerned about defacement or reputational damage don’t use activity logs or monitoring.
So, security awareness is not the problem. The bigger challenge is turning that concern into practical preparation: having a plan for when something goes wrong, training the people involved, and having enough visibility to understand what happened.
Full report: melapress.com/wordpress-secu…
#WordPress #WordPressSecurity


Old WordPress user accounts are open doors to cyber criminals.
It’s a common scenario; a third party developer or agency finishes their work, but their admin account stays active on the client website, often with a weak and shared password.
Here is a security best practise; use a temporary login link instead. Set the role, expiry, and usage limit with Melapress Login Security:
melapress.com/support/kb/mel…

Last week on The Melapress Show I spoke with @frantorres about something most #WordPress users take for granted: the plugin repository.
We search for a plugin, install it & move on. But a lot happens behind the scenes: reviewing and approving plugins, checking for #security issues, and keeping such a huge repository running.
With supply chain attacks becoming more of a concern, that work isn't getting any easier.
Thanks to people like Francisco and the WordPress Plugins Team, we have this resource available to us. Definitely an episode worth listening to if you use WordPress. And whenever you can, don't forget to show your appreciation to this team.
Episode available on our X -- > xitter.cf/melapressHQ/status/209…
Half of all new WordPress plugin submissions never get approved, not because they're rejected, but because the author never replies to the first review.
Today, @frantorres from the WordPress Plugins Team joins us to explain what actually happens between submission and approval.
🎥 Watch the premiere today:
xitter.cf/i/broadcasts/1nGeLMnjz…

Known device detection in Melapress Login Security 2.4.0 is now more reliable. It uses a secure device cookie instead of the browser User-Agent.
Admins can also set how long a device stays recognized, while users can view & remove known devices from their profile and get notified about unrecognized logins.
Keeping your #WordPress website users informed should be part of your website #security strategy.
Now that I’m part of the WordPress Nijmegen Meetup, I have another excuse to promote our upcoming events.
On 14th September, Anna Valenti will be talking about “The After Click Era - the end of search and beginning of distribution.”
Very timely considering how AI is changing search, marketing and how we measure what is working and what is not.
If you’re in Nijmegen, Gelderland or the region, come and join us. The talk is in English, so expats, there is no excuse.
Event info: meetup.com/nl-nl/wordpress-m…
Security statistics are important, but behind every compromised website there’s someone investigating what happened, recovering the site, explaining the incident, and dealing with the consequences.
That’s why we launched the Wall of Security Stories: to give those real experiences a place to be heard:
melapress.com/security-stori…

We released Melapress Login Security 2.4.0 with more checks around sensitive #WordPress user account changes.
Admins can require the current password before a password change, require security questions before an email change, and users can be notified when a new login happens while they already have an active session.
A few more ways to keep user accounts in check. Help your users help you with WordPress #security.
At @WordCampUS 2026 I spoke about session hijacking and one of the blind spots in #WordPress security: what happens after a user has successfully logged in?
The talk covers stolen sessions, session management, user visibility, user education, and what we can do to improve post-login security and user visibility on WordPress websites. This is now more important than ever, considering that session hijacking attacks became the primary attack vector in 2025.
If you missed it, watch my talk: youtube.com/watch?v=z5_hxy2E…
Download the slides & read more about this topic: melapress.com/talks/wordpres…
#WCUS #Security
