

Provider of service to protect websites from being exploited due to vulnerable WordPress plugins.
Joined January 2016
- Tweets6.4K
- Following19
- Followers299
- Likes45



Pinned Tweet
Our weekly update post on what on how our customers are helping to make WordPress plugins more secure is mostly about vulnerabilities that haven't been fixed.
A vulnerability in the 300,000+ install Formidable Forms did get fixed this week, though. pluginvulnerabilities.com/20…
How Our Customers Helped Make WordPress Plugins More Secure, Week of March 1 pluginvulnerabilities.com/20…
AI Helps to Detect Incomplete Security Fix Being Made to 1+ Million Install WordPress Plugin WP File Manager pluginvulnerabilities.com/20…
WooCommerce Vulnerability Listed as Being Fixed in Upcoming Release Was Already Fixed pluginvulnerabilities.com/20…
Authenticated Information Disclosure Vulnerability in Download Manager pluginvulnerabilities.com/20…
One of the reasons there are too many updates for WordPress plugins is that developers are not being proactive about security. Not only are they not getting security reviews to catch issues, but when they are reported to them by others, the fixes are frequently incomplete.

We send an email requesting feedback after a cancelled subscription. Today I received this sensible but depressing response from someone who moved to Shopify due to the maintenance overhead of using WooCommerce with multiple plugins. We do need to consider this as a community and try to make things easier for site owners.

We found incomplete fixes with three plugins being used by our customers in the last week.
One developer got an additional fix out very quickly, so quickly they didn't fully address the insecurity.
The other two haven't released additional fixes. pluginvulnerabilities.com/20…
If WordPress plugin developers want to be proactive, we offer to do security reviews of plugins.
(We also offer free help dealing with vulnerabilities found by others.) pluginvulnerabilities.com/wo…
Another week, another post about how we are helping make WordPress plugins more secure.
This week we caught incomplete vulnerability fixes in Download Manager and Brave Conversion Engine. Unfortunately, they still haven't been fixed. pluginvulnerabilities.com/20…
The developer of Brave Conversion Engine still hasn't fully fixed a previous incomplete fix from November!
They fixed the one example we provided of the remaining issue, but didn't resolve any of the others.
You can sign up for a free trial of our service to see if you are using plugins known to be vulnerable.
We currently have data on plugins with at least 8.2 million installs that are known to be vulnerable and still in the WordPress Plugin Directory! pluginvulnerabilities.com/pr…
We had a confused WordPress plugin developer claiming that we were overstating the impact of a vulnerability we reported to them. But we hadn't reported the vulnerability them, we only knew about it because some of their plugins, but not others, had gotten the fix. 1/3
It must have been one of competitors that was overstating the risk, which often happens.
The best way to avoid that is for developers to make sure their WordPress plugins don't have security issues they can overstate the risk of. 2/3
With our security reviews of WordPress plugins, we not only look for vulnerabilities, but also less serious issues that often get overstated by other providers.
Getting one is a great way to make your plugin more secure and avoid issues like that. 3/3 pluginvulnerabilities.com/wo…
Plugin Vulnerabilities retweeted
If you care about security, you really should avoid dealing with 10Web, as they handle security terribly.
As an example of that, take this apparent zero-day in of their plugins that was exploited last year. That could have easily been avoided. pluginvulnerabilities.com/20…

NinjaFirewall is Providing Misleading Information on Vulnerable WordPress Plugins pluginvulnerabilities.com/20…
Privilege Escalation Vulnerability in Brave Conversion Engine pluginvulnerabilities.com/20…
Authenticated Persistent Cross-Site Scripting (XSS) Vulnerability in Download Manager pluginvulnerabilities.com/20…
Cross-Site Request Forgery (CSRF) Vulnerability in IP2Location Country Blocker pluginvulnerabilities.com/20…
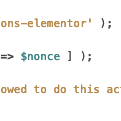
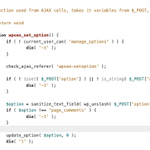
Yesterday, we had what appears to be a hacker calling this AJAX accessible function in the 2+ million install Essential Addons for Elementor on our website. (We don't use the plugin.)
Would they want that nonce for something? Or are they looking to exploit an unrelated vuln?

ALT public function eael_get_token() { $nonce = wp_create_nonce( 'essential-addons-elementor' ); if ( $nonce ) { wp_send_json_success( [ 'nonce' => $nonce ] ); } wp_send_json_error( __( 'you are not allowed to do this action', 'essential-addons-for-elementor-lite' ) ); }
Settings Change Vulnerability in ThemeIsle SDK pluginvulnerabilities.com/20…