




"AI is telling me there's an RCE vulnerability here, but how do I validate it?"
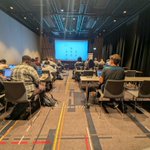
This was one of the most common questions from participants at @secdim Vibe Coding Security workshop at @NDC_Conferences Oslo.
The reality is that AI helps, but we are the gatekeepers. We make the call on the security of our software.
Using some techniques, we can guide AI to find security weaknesses. Assurance can only come from us. A skilled developer knows insecure design patterns, understands AI blind spots, and has the hands-on skill to verify vulnerabilities.
That last point was the key takeaway for participants. We ran the workshop in Oslo. The next one is in London on 25-26 January 2027 (seats are limited. link in the comments).
#security #vibecoding #workshop


Build Fast, Ship Secure: The Vibe Coder's Security Workshop ndclondon.com/workshops/buil…


Wondering why there are many MCP vulns? Per MCP official spec, Authorization is OPTIONAL. Even for HTTP protocol is a SHOULD not a MUST.
Now good luck pushing for OAuth 2: modelcontextprotocol.io/spec…


Orchestration of nano models can out beat frontier models. github.com/weareaisle/nano-a…

Half the "zero-days" on my feed this week would fall apart if anyone checked Apache's own repo first.
This one did. Real insecure pattern, wrong severity claim.


AI Shifted the Skill. It Didn't Remove It.


4Cs of Cloud Native Security: Cloud, Clusters, Containers, Code.
Now a 5th ring: AI Code.
AI-generated code doesn't add a new risk next to Code. It stacks on top of it.
Nobody reviews it fully. Authorship unclear. Intent unclear. The dev "driving" often can't explain what it does.
Complexity compounds.
Learn more at my presentation at @PyConAU

I always enjoy speaking at grassroots tech conferences, and this time here in Australia @PyConAU 🇦🇺.
There is a misunderstanding among some that "AI has solved most of software security problem"! Rather than arguing with this opinion, in this talk, based on real data, I will show that this is wishful thinking, and where the root causes of software security vulnerabilities really are.
Join me Friday. Ballroom 3, 10:45am. First cybersecurity talk of the conference.
Also -> Voucher code for 10% off in comments.
#appsec #securecoding #aisecurity #devsecops

Win this. @defcon @AppSec_Village
Build an AppSec challenge for the SecDim @AppSec_Village Wargame at @defcon 34 and win a Flipper Zero + Video Game Module
Challenge submissions close on 31 July, Only one week left!
👉 appsecvillage.com/ctf
#appsec #securecoding #defcon #ctf

Submit challenge to win prizes! Deadline 31st July. @defcon @AppSec_Village
Build an AppSec challenge for the SecDim @AppSec_Village Wargame at @defcon 34 and win a Flipper Zero + Video Game Module
Challenge submissions close on 31 July, Only one week left!
👉 appsecvillage.com/ctf
#appsec #securecoding #defcon #ctf
I always enjoy speaking at grassroots tech conferences, and this time here in Australia @PyConAU 🇦🇺.
There is a misunderstanding among some that "AI has solved most of software security problem"! Rather than arguing with this opinion, in this talk, based on real data, I will show that this is wishful thinking, and where the root causes of software security vulnerabilities really are.
Join me Friday. Ballroom 3, 10:45am. First cybersecurity talk of the conference.
Also -> Voucher code for 10% off in comments.
#appsec #securecoding #aisecurity #devsecops
Talk: 2026.pycon.org.au/schedule/N…
Voucher: pretix.eu/pyconau/2026/redee…

A great research article by Mahyar, our intern at @secdim showing the realities of some libraries.
“it parses” does not mean “it is secure”. Many libraries prioritise ease of use or safety by omission rather than offering fine-grained security controls.
👉 Full write up: secdim.com/blog/post/the-mis…
#appsec #securecoding #javascript #programming

Feedback loop security degradation: the more you run AI to "fix security", the worse the outcome will be after each iteration. This is interesting academic research.
~40% increase in critical vulnerabilities after just five iterations.
Security-focused prompts still introduced new flaws — cryptographic implementation errors above everything else. Explicitly asking the model to "fix security" made things worse.
The code looked more sophisticated each round. That's the trap. Developers trusted the output, reviewed less, and missed the flaws the model introduced.
At @secdim , we see this also. Developers skip review because it is "too much to review". Those who do review miss the security flaws. The skill to critically evaluate AI-generated code is degrading.
The research recommends mandatory human security code review and no more than three (3) consecutive LLM iterations.
Paper in comments.
#aisecurity #appsec
As expected, 2026 is flooding us with CVEs, but exploitation stays rare. Lots of noise.
H1 2026: 35,364 new CVEs (more than any full year pre-2024).
One every 7.4 minutes — up 49.5% from H1 2025.
Only 85 (0.24%) on CISA KEV so far.
Vulns come faster than ever, but confirmed exploitation is low. The real challenge isn’t patch volume — it’s signal-to-noise.
Follow the great work by jerrygamblin.com/2026/07/01/…
#cve
