Developer security wargame where developers practice real-world security incidents.

Sydney, Australia (HQ)
Joined October 2014
Four new PHP challenges: a TOCTOU race, a Unicode username takeover, server-side request forgery and command injection. Three are inspired by real incidents at Steam, Spotify and Capital One.
1
99
AWS secures the cloud. What you run in it is yours to secure, and S3, IAM, VPC and EC2 each need different hardening. We've updated the nine challenges in our AWS game. Link in the reply.
1
1
48
We will be hosting a 2 day workshop on vibe coding security at NDC London🇬🇧 Come by Room 10 to say Hi if you are attending 👋 👉 secdim.com/news/ndc-london-2… #appsec #securecoding #ndclondon
2
41
Rails wraps a non-Hash JSON body under _json, and a client can send that key itself. One request, two readings. If authz and the action read different ones, that's a bypass. New Ruby challenge:
1
1
48
GlassWorm needed no vulnerability. It shipped as a VS Code extension, hid its loader in invisible Unicode, then spread itself with stolen GitHub tokens. New Incident Response challenge:
1
45
Your team writes only part of the code it ships. Dependencies, build tools, CI plugins and AI assistants expand the supply chain you need to defend. Learn how to map and harden it, including AI-related risks.
1
1
24
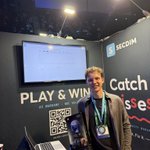
At NDC Oslo's three-day Attack & Defence AI Wargame, competitors secured their apps while finding flaws in opponents' apps. Maksim Ohvrill led at the second-evening prize ceremony and received the winner's prize. Try it:
2
1
70
An XML parser that accepts external entities can turn untrusted XML into file access, SSRF or command execution. That was the vulnerability identified in http4k in December 2024. Try the SecDim Play challenge, available in six languages.
1
1
44