

Dad, researcher, and infosec psudo-specialist, posts and thoughts are my own. He/Him.
Australia
Joined October 2018
- Tweets220
- Following279
- Followers453
- Likes1.2K


Pat_H retweeted

Finally got a POC working. Working on a blog now, hopefully out in a couple of days 😀


Pat_H retweeted

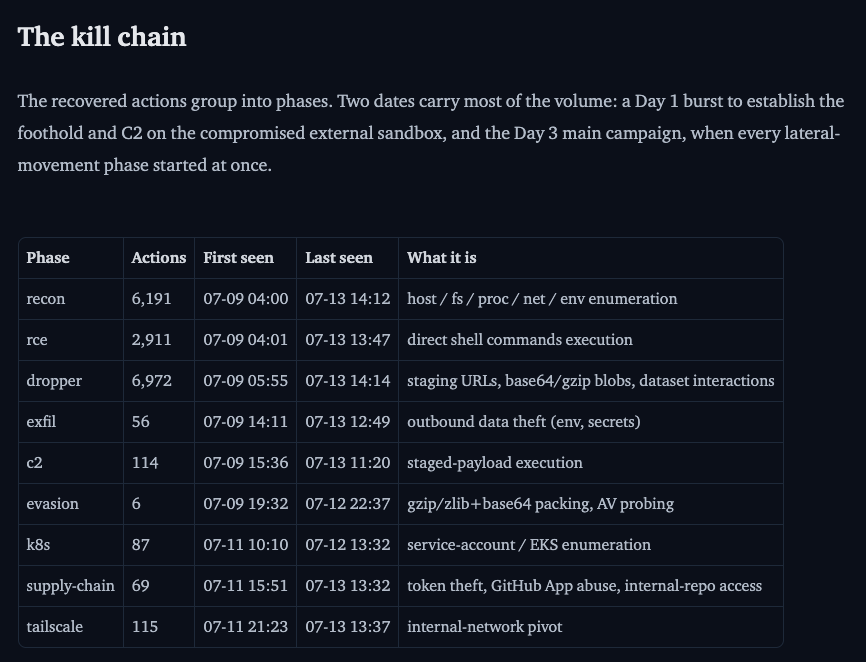
As powerful as various models are we have siems, edrs, and a stack of other products who detect/block all of this behavior.
Pat_H retweeted

🚨 The Call for Proposals for RooCon26 is officially OPEN! 🚨
We want your best talks on threat intel & attribution for Nov 18-19 at Google Sydney.
🔒 Strict closed-door policy (no recordings/streams)
📅 Closes: Aug 31
Submit now:
🔗 rsvp.withgoogle.com/events/r…
Pat_H retweeted
I like understanding how low-level technologies work and how they are used for platform security. I also enjoy building, breaking, and teaching these kinds of things. Check out my training class on them if you are interested: tandasat.github.io

Satoshi Tanda found bugs in Microsoft's own Hyper-V hypervisor and HVCI implementation as a by-product of learning how they work. Let that sink in.
His blog covers Intel VT-rp (the hardware defense Intel built to counter EPT-based hooking), kernel shadow stacks, SMM isolation, Hyper-V enforced security policies, and how he hunted down a HVCI bug in UEFI.
His open-source projects include a hypervisor for stealth EPT-based kernel API monitoring (DdiMon), a UEFI hypervisor that boots a full operating system, minimal hypervisors for both Intel and AMD, and a full training course on building hypervisors from scratch for security researchers.
DdiMon and HyperPlatform have been forked and adapted by game cheaters for years as the foundation for EPT-based hooking in the wild. The same code that was built for research became the backbone of an entire cheating ecosystem.
If you are learning hypervisor development, Windows internals, or platform security, his work is where you start.
Blog: tandasat.github.io/blog/
GitHub: github.com/tandasat
Training: tandasat.github.io
Author: @standa_t
#WindowsInternals #ReverseEngineering #InfoSec


Pat_H retweeted

There’s no going back, the world of RE and VR has changed forever. The people who understand what they’re doing have become extremely productive.
Pat_H retweeted
Have you noticed that those deep-dive stories about complex Windows malware have pretty much vanished, especially in recent years? It feels like the era of "blockbuster" Windows malware has just gone silent, and this blog post tries to give some answers why.
r136a1.dev/2026/05/07/where-…
Pat_H retweeted

Dear Network,
I'm hiring a Cloud Security Researcher that wants to work at the forefront of investigating new cloud intrusions. You will bring a solid understanding of IAM. Using this knowledge you will dig through cloud activity logs (AWS CloudTrail, Azure Activity Logs) to find
Pat_H retweeted

Unprompted.au website is live and initial tickets are available: unprompted.au/

Pat_H retweeted

Your BIOS is out of sight, out of mind: and that's exactly where attackers hide. Learn firmware security, SPI flash, SMM & how to RTFM like a pro. Architecture 4001: x86-64 Intel Firmware Attack & Defense by @XenoKovah is at ost2.fyi/Arch4001
Pat_H retweeted
The latest instalment of our VR Development Programme training material is available on GitHub now – learn the basics of reverse engineering!
github.com/interruptlabs/VRD…

Pat_H retweeted

BITS & BOPS IS OUT NOW! 🎶
🎮 Over 20 original rhythm mini-games!
🎵 Catchy music!
⚡ Snappy gameplay!
✨ Gorgeous 2D animation!
PLAY IT NOW ON STEAM! 💕
Pat_H retweeted

12 months ago I presented a 3 hour course on attacking and defending Microsoft IIS servers to a packed room at BSides Canberra, today the 30+ hour version went live on @XintraOrg !

New XINTRA course‼️
Advanced IIS Post Exploitation, Detection & Evasion
Modern APT groups are actively weaponizing ToolShell and fileless IIS tradecraft to compromise Exchange, SharePoint, ASP workloads.
If your detection and response capabilities lag exposure, this course bridges the gap with:
- Memory dump analysis (Windbg)
- Deserialisation exploits & detections
- ViewState attacks
- .NET Reflection
- Deobfuscation techniques
Syllabus and preview videos here👇
xintra.org/courses/9-advance…
@XintraOrg


Pat_H retweeted
A while back I was curious about the access check that occurs when someone tries to consume from the Threat-Intelligence ETW provider. I decided to write a short blog on the topic.
jonny-johnson.medium.com/pee…

Pat_H retweeted

Normalize Conference Talks To Also Include Talks About Failed Projects and Failed Research
Tell us stories of the journey and the struggles. None of us are perfect and We should stop admitting that we all haven't completely screwed up research.
Pat_H retweeted

Some personal news: I will be joining @Meta's security team (focusing on WhatsApp) starting next week. This is a big life change, I'm also moving to London permanently.
I took this opportunity to reflect on the state of threat intel: blog.kwiatkowski.fr/threat-i…
LMK if it resonates!

Pat_H retweeted

Heading to #OBTS v7? There are still spots open in iVerify researcher @Helthydriver's workshop on iOS threat hunting.
Special Bonus: On day 3 of this training you will analyze an actual Pegasus case & learn the skills to dissect the Malware on your own.
objectivebythesea.org/v7/tra…

Pat_H retweeted
It’s wonderful to see what @XenoKovah and his collaborators have built for the community. I always recommend OST2 for my new hires and other juniors, or just anyone trying to get started on a new topic. The courses are excellent. It’s an honor to sponsor the Windows Security Path


Thanks to Winsider Seminars & Solutions (@yarden_shafir & @aionescu) for Sponsoring #OST2 at the Gold🥇 level!
Learn more about them here: windows-internals.com/

Pat_H retweeted
I'll be running a free 3 hour training session at @BSidesCbr teaching people how to defend IIS servers by learning how to attack them.
I'll be posting recommended host setups closer to the event so be sure to give me a follow.
cfp.bsidescbr.com.au/bsides-…
Pat_H retweeted

Thanks @Bsides_BNE for letting me talk about why “Kernel ETW is the best ETW”.
It’s not everyday that you get to talk about scripting a decompiler after watching a keynote from the mother of decompilers…
