
🦅 The changelog says "bug fixes." The diff says "security patch." We track CVE-less fixes so defenders don't fly blind. New drop every Thursday. @78_lab
Joined June 2026
- Tweets159
- Following2
- Followers69
- Likes1




PatchHawk looks for security fixes in software updates. For selected cases, we share the code change and steps to reproduce the bug: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more fixes explained through code. #PatchHawk #78ResearchLab

Firefox 151.0.3 includes Mozilla's fix. On Linux, Firefox uses the system FreeType library, so updating Firefox doesn't update that library. PatchHawk compared the releases. We matched the change to this CVE and ran the Docker test ourselves. mozilla.org/en-US/security/a…

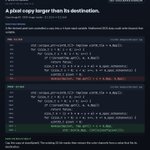
FreeType later changed SHZ, the instruction that moves points in a glyph. It now picks the right set of points and stops at the end of that set. The two cards show the code. This fix came after 2.14.3. github.com/freetype/freetype…


In Docker, we used a small program to load Mozilla's font through FreeType's public FT_Load_Glyph API. ASan found no issue with 2.14.2, but caught a read past the end of a buffer in 2.14.3. Mozilla also reported a write past a buffer. bugzilla.mozilla.org/show_bu…
The change is easy to miss. In 2.14.2, FreeType made room for the glyph's existing points, plus four more. In 2.14.3, it only made room for four. That wasn't enough for some glyphs made from other glyphs. github.com/freetype/freetype…

PatchHawk finds security-relevant fixes in release diffs. Selected PoCs include write-ups, repro steps, and pre/post comparisons: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more fixes explained with real code and verifiable PoCs. #PatchHawk #78ResearchLab
The PoC is now public: github.com/78ResearchLab/Pat…
It includes the 345-byte JXL input, Docker reproduction scripts, 0.11.1/0.11.2 djxl logs, and the Valgrind trace. The README states the tested 32-bit scope and limitations.
Upstream named the fix in v0.11.2: github.com/libjxl/libjxl/rel…
Patch: github.com/libjxl/libjxl/pul…
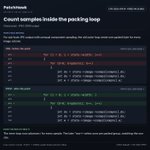
PatchHawk flagged the arithmetic change; its PoC attempt was incomplete, so we verified the CLI and Valgrind results manually.


PatchHawk finds security-relevant fixes in release diffs. Selected PoCs include write-ups, repro steps, and pre/post comparisons: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more fixes explained with real code and verifiable PoCs. #PatchHawk #78ResearchLab
Both reproductions use FFmpeg's CLI entry points and are packaged in Docker. They show sanitizer-detected writes; we did not demonstrate code execution or an unsanitized crash.
Ogg PoC: github.com/78ResearchLab/Pat…
Filter PoC: github.com/78ResearchLab/Pat…
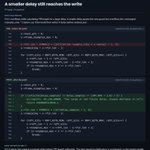
Now the filter. On 9.0.1, firequalizer=delay=30000 overflows the FIR-length calculation under UBSan. 9.0.2 rejects that value. But a later signed multiplication, nsamples_max * 2, is still there.
Patch: github.com/FFmpeg/FFmpeg/com…

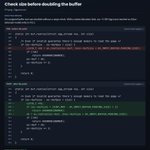
In the Ogg demuxer, buf_realloc() doubled an unsigned buffer size without checking the limit first. Near UINT_MAX/2, that can wrap. On 9.0.1, our raised-limit run hit an ASan invalid write (WRITE of size 31895). On 9.0.2, it returns ENOMEM.
Patch: github.com/FFmpeg/FFmpeg/com…
