
🦅 The changelog says "bug fixes." The diff says "security patch." We track CVE-less fixes so defenders don't fly blind. New drop every Thursday. @78_lab
Joined June 2026
- Tweets159
- Following2
- Followers69
- Likes1


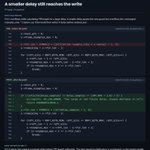
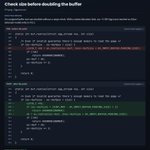
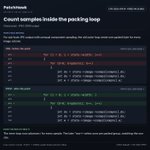
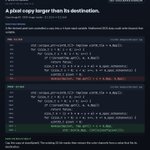


Firefox 151.0.3 includes Mozilla's fix. On Linux, Firefox uses the system FreeType library, so updating Firefox doesn't update that library. PatchHawk compared the releases. We matched the change to this CVE and ran the Docker test ourselves. mozilla.org/en-US/security/a…

PatchHawk looks for security fixes in software updates. For selected cases, we share the code change and steps to reproduce the bug: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more fixes explained through code. #PatchHawk #78ResearchLab

The PoC is now public: github.com/78ResearchLab/Pat…
It includes the 345-byte JXL input, Docker reproduction scripts, 0.11.1/0.11.2 djxl logs, and the Valgrind trace. The README states the tested 32-bit scope and limitations.
PatchHawk finds security-relevant fixes in release diffs. Selected PoCs include write-ups, repro steps, and pre/post comparisons: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more fixes explained with real code and verifiable PoCs. #PatchHawk #78ResearchLab
Both reproductions use FFmpeg's CLI entry points and are packaged in Docker. They show sanitizer-detected writes; we did not demonstrate code execution or an unsanitized crash.
Ogg PoC: github.com/78ResearchLab/Pat…
Filter PoC: github.com/78ResearchLab/Pat…
PatchHawk finds security-relevant fixes in release diffs. Selected PoCs include write-ups, repro steps, and pre/post comparisons: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more fixes explained with real code and verifiable PoCs. #PatchHawk #78ResearchLab