




Cool! Any chance you could figure out how to enable the Unity debug menu? My daughter never told me how she got into it, and I think she’s forgotten how to reproduce it 😆


1
1
165
What if Huaqiangbei tech just feeds image data directly over MIPI?

Today, we're launching ZCAM, an iPhone camera app to Prove What’s Real.
ZCAM cryptographically signs photos and videos at the moment of capture. Anyone can independently verify the content came from a real device and hasn't been altered or AI-generated.
1
331
outoflegend retweeted

Fixed in 2018, but many user wallets got hacked in 2023. @teawaterwire and I are one of them. The Lubian hack is not related with Trust Wallet. This is the FUD part. However, Trust Wallet team lied about many things in their statement.
Trust Wallet admitted their product had a vulnerability in 2018 but vehemently denies that it affected their users in the mass wallet theft incident of 2023. They claim to have notified all affected users back in 2018 to migrate their assets, which is clearly a lie fabricated for PR purposes.
We previously disclosed the vulnerability in Trust Wallet for iOS from 2018. Any security issue related to Binance easily turns into FUD, which in turn triggers a knee-jerk reaction from Trust Wallet. It's actually normal for any software to have security vulnerabilities; what matters most is how they are handled properly.
Here is our previous disclosure post about the Trust Wallet iOS vulnerability: xitter.cf/ErrNil/status/17482033…
And here is Trust Wallet's announcement after the issue gained traction: xitter.cf/TrustWallet/status/175…
After the last incident, I was quite disappointed with Trust Wallet's response and lost interest in following up on the case. However, whenever I see PR statements that I find obviously incorrect and illogical, I always feel uncomfortable and have to speak my mind. So I'm taking this opportunity to discuss some of these points, just to leave a record.
Trust Wallet mentioned that the number of affected users at the time was about 10,000 early adopters, and that they had notified each one and provided an asset migration plan. They claim no users suffered losses and all affected wallets have been deprecated.
In fact, this is highly counterintuitive. Trust Wallet was extremely popular in 2018, which led to its acquisition by Binance. In such a situation, notifying 10,000 users about a security issue with their wallets and getting them to migrate would have been a tricky affair. If they had really done it, it would have almost certainly made the news. My own first Trust Wallet address was also generated in 2018 and was drained in the July 2023 incident. I have no memory of ever receiving any notification. This user's situation is the same as mine: xitter.cf/teawaterwire/status/17…
Trust Wallet mentioned that since July 2018, all new wallets created by Trust Wallet users are no longer affected by this vulnerability.
This is also patently false. How can you guarantee that every single one of those 10,000 users updated their software to the latest version? If someone downloaded the problematic version at the time and never updated the app, then all addresses created with that version of the wallet would be permanently insecure and vulnerable to theft.
Trust Wallet mentioned that the comprehensive evidence suggests the 2023 attacks did not originate from a Trust Wallet vulnerability, but were more likely caused by a combination of multiple sources. They state they have full confidence that the 2018 vulnerability was not the root cause of this incident.
This is a very clever, but highly inaccurate, turn of phrase. In reality, while the 2018 Trust Wallet vulnerability was not the *sole* root cause of all the wallets drained in July 2023, it was a major contributor. The reasons are as follows: real Trust Wallet users were affected; the affected addresses could be reproduced using Trust Wallet's code from that time; and the activity timeline of the affected wallets highly correlates with Trust Wallet's code commit history. We discussed this in more detail in our original disclosure article, so I won't repeat it here.
Trust Wallet mentioned that in addition to fixing the vulnerability, the founder of Trust Wallet proactively contacted affected users to provide them with a secure migration path, ensuring no users remained at risk. They also state that the relevant affected addresses have all been confirmed to no longer hold any balance.
The part about confirming the relevant addresses no longer hold a balance is the most ridiculous part, because these addresses were cleaned out in July 2023.
I am also a heavy Trust Wallet user. The theft from my first Trust Wallet address in July 2023 prompted me and my colleague @outoflegend to conduct an in-depth investigation.
However, what truly made me lose my "Trust" in it was Trust Wallet's subsequent response and handling of this vulnerability. I can partly understand, as every wallet provider wants to have a perfect security record. I sincerely hope Trust Wallet can do better, provide more evidence, and dispel the community's doubts.
I have deliberately not deleted my first Trust Wallet address; I just added "Rekt" to its name.
@cz_binance @heyibinance I have great respect for you. Were you also deceived by your team, or were you in on it too?
I hope they/you can provide any valid evidence that they notified 10,000 users to migrate.
This quoted post is unavailable.
Lateral control completed.
BMW accepts steering angle control, I think OpenPilot can handle a U turn😄 @comma_ai
Many thanks to the author of this blog post @PD0WM , it was very inspiring: icanhack.nl/blog/audi-flexra…


Hello @comma_ai , BMW porting is on the way.
Use 2 cheap FlexRay transceivers and 1 Raspberry Pico2 to perform the MITM, it’s super low cost.
github.com/dynm/pico-flexray…
14
859
Hello @comma_ai , BMW porting is on the way.
Use 2 cheap FlexRay transceivers and 1 Raspberry Pico2 to perform the MITM, it’s super low cost.
github.com/dynm/pico-flexray…
Many MEV bots monitor addresses with compromised private keys, instantly draining ETH mistakenly sent to them. For example, Hardhat’s default mnemonic, "test test test test test test test test test test test junk", derives the address 0xf39Fd6e51aad88F6F4ce6aB8827279cffFb92266.
With EIP-7702, anyone can set code for these addresses, effectively installing a hook. If ETH is sent to such an address, a fallback function can automatically redirect the funds to another address. For instance, this transaction (etherscan.io/tx/0xa85d9502f8…) demonstrates this behavior.
Check etherscan.io/address/0xf39Fd…: the latest delegated address is 0x930FcC37d6042c79211EE18A02857Cb1Fd7F0D0b, which implements the fallback function.
The alarming part? Setting code for an address only requires a signature, included in the authorization_list of a type 0x04 transaction. This transaction’s to field can be any address, meaning there’s no direct on-chain interaction with the target address. You can’t easily detect if an address has been set with code by checking its transaction history.
Imagine this scenario: you create a new wallet, but its keys are accidentally leaked. Someone sets malicious code on your address. Later, when you receive ETH, the funds are automatically drained without your knowledge.
I urge wallet developers to implement a check using eth_getCode to alert users if their EOA has unexpected code, enhancing security against such risks.
@officer_secret @blockaid_ @elyx0

outoflegend retweeted
Must-watch 38C3 @ccc talk on low entropy vulnerabilities
Props to Milk Sad team (@JohnNaulty, Christian Reitter & team) for their groundbreaking research 🔍
Proud our Trust Wallet research w/ @outoflegend @SECBIT_IO got featured
🎥: media.ccc.de/v/38c3-dude-whe…

Hi @zkbankai, we've just submitted our proposal for the Soulforge grants: github.com/zk-bankai/soulfor…

I also didn't expect that the tau of Ethereal Quest's SRS was Googled, constructing a fake proof.

Congrats on the success of this event. The participants were truly impressive, each bringing a unique and remarkable perspective to the same challenge. Learned much from their excellent write-ups. I contributed this puzzle: github.com/p0n1/familiar_str…. One participant's approach even led me to discover an unexpected bug in my code.

2
437
outoflegend retweeted
🚨 *Vulnerability Alert:* Trust Wallet's Fomo3D Summer 🚨
🔗 Full Disclosure: secbit.io/blog/en/2024/01/19… 💸 Losses on ETH mainnet alone are staggering – and that's just the tip of the iceberg.
🧵 A thread on the findings and implications for users: 👇 (1/n)
outoflegend retweeted

📢Ready to embark on the exciting zkCTF adventure? Now, hosted by #ScaleBit with a focus on #ZK security, the online CTF (Capture The Flag) is officially open for registration!
🛡️ScaleBit, a subsidiary brand of #BitsLab, boasts professional expertise in ZK technology and is dedicated to ensuring security environments. Collaborating with partners passionate about ZK, zkCTF is designed to attract security experts and developers fascinated by ZK technology and applications, fostering skills, innovation, and a deeper understanding of the rapidly evolving field of Zero-Knowledge Proofs.
🏆zkCTF is open to global developers, and there's no purchase or payment necessary to enter or win. Showcase your talent and innovation! This event features various challenges related to ZK, with a total prize pool of up to 3,500 USDT!
🔗Visit the official website to register and secure your spots to seize the glory!
zkctf.scalebit.xyz/
📅Mark your calendars for the following time points:
- Registration Period: Deadline on Feb 5th, 2024, 1:00 am UTC
- Competition Period: Feb 3rd, 2024, 1:00 am UTC - Feb 5th, 2024, 1:00 am UTC
- Winners Announcement: On or around Feb 6th
🧑💻Join the zkCTF Telegram group for more support:
t.me/ScaleBitAudit
🥳A huge shoutout to our amazing lineup of partners!
- Title Partners: @Scroll_ZKP, @EthStorage, @SECBIT_IO, and @TermStructLabs
- Partners: @gate_io, @HashKey_Capital, @SinohopeGroup, @ambergroup_io, @ChainbaseHQ, @BixinVentures, @zkLink_Official, @ProjectZKM, @ZKTNetwork, @padolabs, @ZKEX_Official, @soraventures, @zkDXio, @xrexinc, @OpenBuildxyz, @MyStarbase_com, @BSPN_TV, @Bubbleai_xyz, @StarkNetAstroCN, @zkBust, @TrustaLabs, @lazyotter_fi, and @137_labs
- Media & Community Partners: @Web3FutureHQ, @OdailyChina, @offchainglobal, @BeWaterOfficial, @BugRap_Team, @blocklikecom, @OurTinTinLand, @1nf0s3cpt, @Antalpha_Labs, @moledao_io, @LXDAO_Official, @kepler42bDAO, @W3CDAO_123, @1783Dao, #DolphinNews, @talk99,
@CryptoWhale1888,@defam_info, and @ProbiusOfficial
💡Inviting all ZK developers and enthusiasts worldwide to join us on this thrilling exploration of ZK. Stay tuned for more updates and partners! Unleash your brilliance — Register without hesitation!

outoflegend retweeted

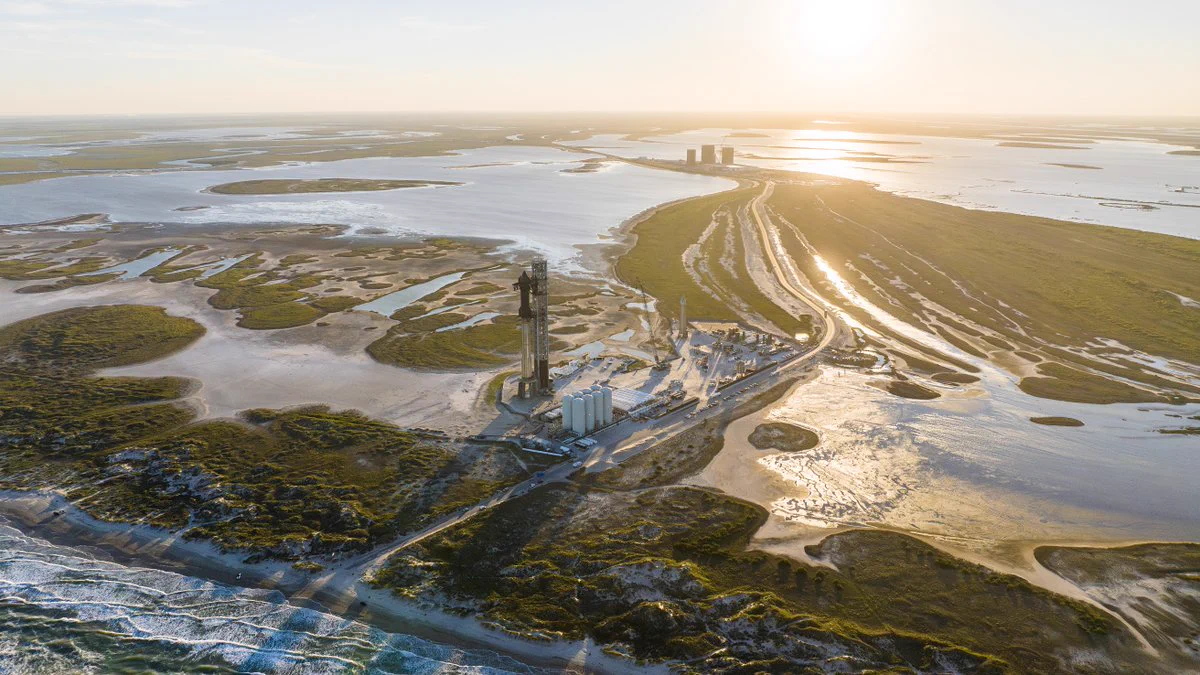
Watch Starship’s second integrated flight test xitter.cf/i/broadcasts/1dRKZEWQv…
I just contributed to the 🕯️ KZG Ceremony 🕯️ using 0x111…1011 to help scale Ethereum
↓ Add your own randomness ↓ ceremony.ethereum.org
213
outoflegend retweeted

BREAKING: Blur just made a game-changing move to bypass OpenSea's blocklist control
As stated in airdrop announcement, Blur is trying new things for an unprecedented launch.
Here's how they did it & the impact their move will have on the NFT market, esp. for creators&traders👇

I've just claimed my Safe governance tokens and delegated my voting power to wentokyo.eth to help steward the public good that is @Safe 🔰🫡
1


@punk3155
's idea has been implemented.
It's yesterday once more.
Using all pre-merge dapps on their own front end with ETHW, simply override the chain id.


1
Now you can foresee what will happen before sending transactions in the real-world.
Add token balance change & approval preview.
Thanks a lot to @eth_tx for their pretty CSS.

1
1