





Interesting preprint: E. Liu et al., "Forward Pass: On the Security Implications of Email Forwarding Mechanism and Policy"¹
A survey of email authentication and forwarding quirks of major mail providers, and how this could be used for spoofing
__
¹ arxiv.org/abs/2302.07287

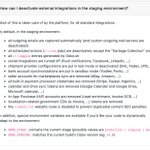
ALT Paper excerpt with figure 3 showing the 4 prevalent email forwarding schemes: PMF, MFEF, REM and REM+MOD

ALT Table 1 from the paper, showing the list of major mail providers and the forwarding scheme they use

ALT Table 2 from the paper showing the list of vulnerable security assumptions and forwarding features implemented by mail providers

ALT Figure 7 of the paper showing an attack scenario leading to successfully spoofing an Office365 domain and passing DMARC checks
According to the authors, any domain hosted on O365 could be successfully spoofed using another O365 domain and a forwarding rule. GMail hosted domains could also be spoofed if they hosted a M-L, for example.
Most impacted providers have apparently fixed the vulnerabilities ✨

ALT Excerpt from the paper showing that the authors disclosed their finding to the impacted providers and received mostly positive answers (and some bounties)
Detecting increasing numbers of credential stuffing attacks via botnets on our website.
Even with our mitigations, the success rate is non-zero. 0.04% again this morning for a campaign targeting AU users.
You can setup 2FA as a portal user too. And unique passwords 🙏
Olivier Dony retweeted
If you've run Debirdify/Fedifinder a while ago, you might also want to rerun it ASAP to catch any new handles before they're gone.
Olivier Dony retweeted
Folks, the time to run debirdify.pruvisto.org or fedifinder.glitch.me is now.
You don't need to have an account elsewhere yet. Download the CSVs while you can, and you can import them later.
go go go go
Have you tried #AdventOfCyber2022 ?
You can discover or brush up cybersecurity 101 skills, like log analysis, brute force, OSINT, etc. Entry-level topics, can play directly on the VM from your browser. It's fun and only needs a few mins a day. Go help 🎅!
tryhackme.com/christmas
Getting reports of malware distributed via fake emails about "software update" for Odoo, linking to zipped .exe files👻
We try to have them taken down asap, but you know better than that anyway :-) Odoo updates are always available through official channels (repos / packages)
Virustotal for a sample one: virustotal.com/gui/file/0a82…
You can always report malware links to Google Safe Browsing to have them blocked in browsers directly: safebrowsing.google.com/safe…

Olivier Dony retweeted

Help your child learn how to explore the digital world confidently with the @Google Interland game.
ALTER TABLE res_partner ALTER CONSTRAINT res_partner_l10n_mx_edi_addenda_fkey
ON DELETE FORGET ABOUT THIS NONSENSE;
-- Not an actual query🙄
Everything about this "l10n_mx edi addenda" stuff looks technically wrong. The naming, the concepts mix-up, the perf consequences, ...
Olivier Dony retweeted
Pleased that we found an agreement in principle on a new framework for transatlantic data flows.
It will enable predictable and trustworthy 🇪🇺🇺🇸 data flows, balancing security, the right to privacy and data protection.
This is another step in strengthening our partnership.

Planning to require 2FA for all external collaborators who get access to Odoo Github repositories. This means all customers who have access to `odoo/enterprise`
If you don't have 2FA yet:
- on Github click on your avatar (top corner)
- "Settings"
- "🛡Password and Authentication"


The sky’s the limit for phishing, human decision is the always weakest link 🙈
Hopefully new technology will void this someday, e.g. adoption/evolutions of WebAuthn, etc

I published a blog article detailing a phishing technique I called Browser in the Browser (BITB) Attack. It's very simple but can be very effective. I also published templates on my Github feel free to test them out.
mrd0x.com/browser-in-the-bro…

Olivier Dony retweeted

Developers, help out @itaryan with her PhD by taking 10-15 minutes to fill out this survey about secure software development: forms.office.com/pages/respo…
Olivier Dony retweeted
Better spell it out: neither Odoo as a product (Community Edition / Enterprise Edition - without third-party Apps), nor Odoo SaaS, Odoo SH or IAP services use any java-based technologies that would be vulnerable or vectors for the log4j exploits (CVE-2021-44228), even indirectly
Better spell it out: neither Odoo as a product (Community Edition / Enterprise Edition - without third-party Apps), nor Odoo SaaS, Odoo SH or IAP services use any java-based technologies that would be vulnerable or vectors for the log4j exploits (CVE-2021-44228), even indirectly
We're monitoring the situation with subprocessors for the Odoo cloud, but we control the software and OS stacks of our data-processing systems, and customer data is encrypted at rest and in transit, so there should be no possibility of impact.
Lecture vivement conseillée! Comment le contrôle sur les traitements de données personnelles des citoyens par l’État belge est supposé fonctionner - et pourquoi il est en train de disparaître. (Pas de paywall)
Merci @philaloux @DegraveElise et tous les autres!

Données personnelles: "il est grand temps que l’on vous dise…" "Les craintes que l’on pensait relever du fantasme se sont avérées fondées". Carte blanche vérité co-signée par un collectif de juristes, d’avocats, de DPO, de médecins... @lesoir lesoir.be/373416/article/202…
Sur le même sujet, le reportage édifiant de @LesNews24 il y a 3 mois: youtube.com/watch?v=3y-6aMKG…
Et l'article: ln24.be/2021-02-23/pourquoi-…