
InfoSec geek for Cloud/Clusters/Containers/things-starting-with-C ex: @BrexHQ & @Cruise. founder @ensignia_dev honk the planet
Tāhuna/Batmania/San Secuestro
Joined April 2009
- Tweets8.1K
- Following5.1K
- Followers3.7K
- Likes25.4K
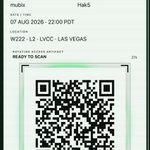

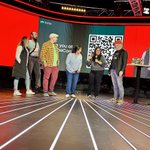


We have received reports that hackers are using genAI to create fraudulent slopcon.org “black badges”, and are charging people for tickets.
Slopcon is a free event & black badges are not a thing. Get Netwise, surf safely.

ALT A fake “black badge” registration with a suspicious QR code belonging to Mubix from Hak5




French retweeted
A bunch of very smart security nerds (and, along for the ride, me) are standing up a conference about AI/security (the intersection of those ideas, not just the security of AI).
unpromptedcon.org/
French retweeted

Accepted! Go 1.26 will include a SECRET package. Don't tell anyone about it 🤫
Just kidding. The package wipes the memory to keep secrets safe — hence the name.
antonz.org/accepted/runtime-…


French retweeted

I'm releasing my latest project today: seccompare.com
Ever wonder if your custom seccomp profile is secure? Or is it actually less secure than RuntimeDefault? antitree.com/2025/07/introdu…


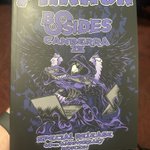
ALT Front cover of the hacker zine Phrack from BSides Canberra conference. Black and purple text with a stylised magpie in a hacker hoodie, wings spread with two laptops


It’s always an honour to see @xntrik on stage, sharing his wisdom & an overview of his career!
His 7-minute drum solo as a metaphor for modern web application security certainly provides a unique perspective! #CyberConMelbourne
cc @AISA_National @CyberSecPeople @RickiBurke

ALT Xntrik on stage
French retweeted

8/ Computer Use Are A Sadness - 🎖️Engagement Award
Exploiting computer use agents using LLM security vulnerabilities for fun and profit
Hijack agents that try to access your computer


Congrats @feross & the @SocketSecurity team 🚀 - exciting to see their plans come to life

🚀 Big news! @SocketSecurity just raised a $40M Series B round to combat next-gen software supply chain security attacks and defend open source.
The round was led by @AbstractVC, with @eladgil, @a16z, and top angels.
We have big plans for the $$$ – see thread ⬇️
🧵 1/10


French retweeted

Last week, our project Docker-OSX's Docker Hub account received a DMCA takedown notice from Apple to remove our Docker images from Docker Hub. The images have over 750k pulls. The GitHub page has 40k GitHub stars. It is a security research project that is geared towards Linux users (and now Windows) being able to participate in Apple Bug Bounty. Apple is obviously well aware of the project, as our project has been active for over 4 years.
You can read the DMCA notice here: bleepingcomputer.com/news/se… via @billtoulas from @BleepinComputer
The project: github.com/sickcodes/Docker-…
Clause 7. b. of the Apple Security Research program explicitly permits breaching Apple licenses including, copying, decompiling, reversing, create derivative works, etc. security.apple.com/terms-and…
The DMCA notice simply asked Docker Hub to cease hosting our automated Docker builds, that are automatically created from Dockerfiles in the GitHub project.
Anyone can build the Dockerfile locally. Yes, it will download the latest macOS installer for each version. Yes, the Docker builds therefore contain macOS (recovery) installer file.
Should I create a second set of Dockerfiles, that will download the macOS installer at runtime in order to comply with the DMCA? This will shrink the image size significantly, and every `docker run` will therefore use the very latest macOS installer for that major version.
bleepingcomputer.com/news/se…
French retweeted

Thrilled to release my latest research on Apache HTTP Server, revealing several architectural issues! blog.orange.tw/2024/08/confu…
Highlights include:
⚡ Escaping from DocumentRoot to System Root
⚡ Bypassing built-in ACL/Auth with just a '?'
⚡ Turning XSS into RCE with legacy code from 1996
French retweeted

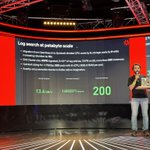
@nffrenchie presenting the talk "Runtime Reachability: Prioritizing Vulnerabilities with eBPF & Continuous Profiling".
#dc32 #defcon32
