




Markus Lassfolk retweeted

Today, I'm releasing the first version of a small web 🚀: rosti.bin.re/
It provides IOCs and YARA rules collected semi-automatically from public blog posts and reports of almost 200 cybersecurity sites.
I hope it proves useful to some of you ... 🙏✨ #ThreatIntel

ALT Screenshot of the "reports" section of Rösti. The page displays multiple reports in a grid format, each with a card-like design. Each card includes information such as the report title, author, publication date, associated threat indicators (IOCs and YARA rules), and source organization.
Markus Lassfolk retweeted

This hack is brilliant, APT28 hopping into a target environment over wifi by compromising neighbouring companies and finding a dual-homed host within range.
volexity.com/blog/2024/11/22…
And yet... they got caught doing this!

New breakout from Hyper-v guest to host.
Details here:
truesec.com/hub/blog/how-to-…

Markus Lassfolk retweeted

Windows 11's new AI Recall feature raises security concerns. Therefore, check this KQL hunting query (see below) designed for Microsoft Defender for Endpoint users to detect any activations of AI Recall on your network which has been created by Steven Lim.
#ThreatHunting

Markus Lassfolk retweeted

A friendly reminder that you are indeed responsible for backups even when using someone else’s data center.

Google Cloud accidentally deleted a company's entire cloud environment (Unisuper, an investment company, which manages $80B). The company had backups in another region, but GCP deleted those too. Luckily, they had yet more backups on another provider.
theguardian.com/australia-ne…

We are hosting our monthly Community Evening in Stockholm (on-premises, not virtual), this time on the subject of 'Operational Technology' with a guest speaker from SANS.
Welcome!
Link for pre-Registering:
lyyti.fi/reg/Truesec_Technic…

Looks like we will have a busy summer...

Nothing to be scared about folks, just another CVSS 9.8 0day disclosed 0days ago that's gonna get code execution in 0 seconds (3 seconds to be more accurate), no limitation, no authentication, no shit, just straight up remote code execution
#IvantiForLife

Has anyone seen any way to visualize for Corp Users any changes IT does to o365/EntraID/Intune?
Im dreaming of an internal website showing anything that has changed, showing any new apps, policy changes etc etc
Markus Lassfolk retweeted
I highly suggest everyone in #CTI to check out the community version of @ValidinLLC.
Free availability of historical DNS data going several years back is absolutely amazing to have at hand.
I use this tool several times a week during my investigations, with great success.

It's here - our long-awaited update is out! This update builds on our massive passive DNS database and is packed with features requested by the community. ❤️ If you're a threat hunter or researcher, this platform is made for you!
validin.com/blog/announcing_…

Markus Lassfolk retweeted

This 👇 is interesting and suggests that we can't anymore consider only the possibility of a common initial access broker #IAB in case of one victim claimed under more than one #ransomware brand.
I've counted 88 cases of cross-claims since Jan. 1st, 2023. Let's take a look...

🌐 On the last day, Lockbit #ransomware group announced sixteen new victims despite operation #Cronos 🚨
More than five of the victims are companies that were already been #compromised by BlackCat (ALPHV) team, whose website was allegedly shut down by law enforcement 👀
#Lockbit with a total of 2533 victims 🥇
➡️ More Info: DARKFEED.IO
#BlackCat

Markus Lassfolk retweeted

I've developed a new Red-Teaming tool called NoArgs. It dynamically hooks into Windows APIs to manipulate and hide process arguments.
By injecting it into a cmd process, it hides the arguments of every newly spawned processes at runtime, without leaving traces for logging applications that rely on information from the Process Environment Block (PEB).
Source and detailed info:
github.com/oh-az/NoArgs


Markus Lassfolk retweeted

This is a great thread on the #PowerShell subreddit. I learned a thing or two. reddit.com/r/PowerShell/s/hd…

Yikes! Imagine the feeling when you have just paid 22M USD in ransom and don't get any keys...

Earlier today @ddd1ms shared information regarding allegations from ALPHV affiliates of ALPHV administrative scamming partners.
A user went online to state they are responsible for ransoming Change Healthcare. They state after receiving payment ALPHV administrative staff suspended their account. They continue to say the suspension was suspicious and March 3rd, 2024 the wallet which received the Change Healthcare funds was emptied.
They conclude the post by unveiling an ALPHV wallet which has received approx. $92,749,381 (or 1401 BTC)
Wallet: 14Q5xgBHAkWxDVrnHautcm4PPGmy5cfw6b
*information and photos via @ddd1ms

Markus Lassfolk retweeted

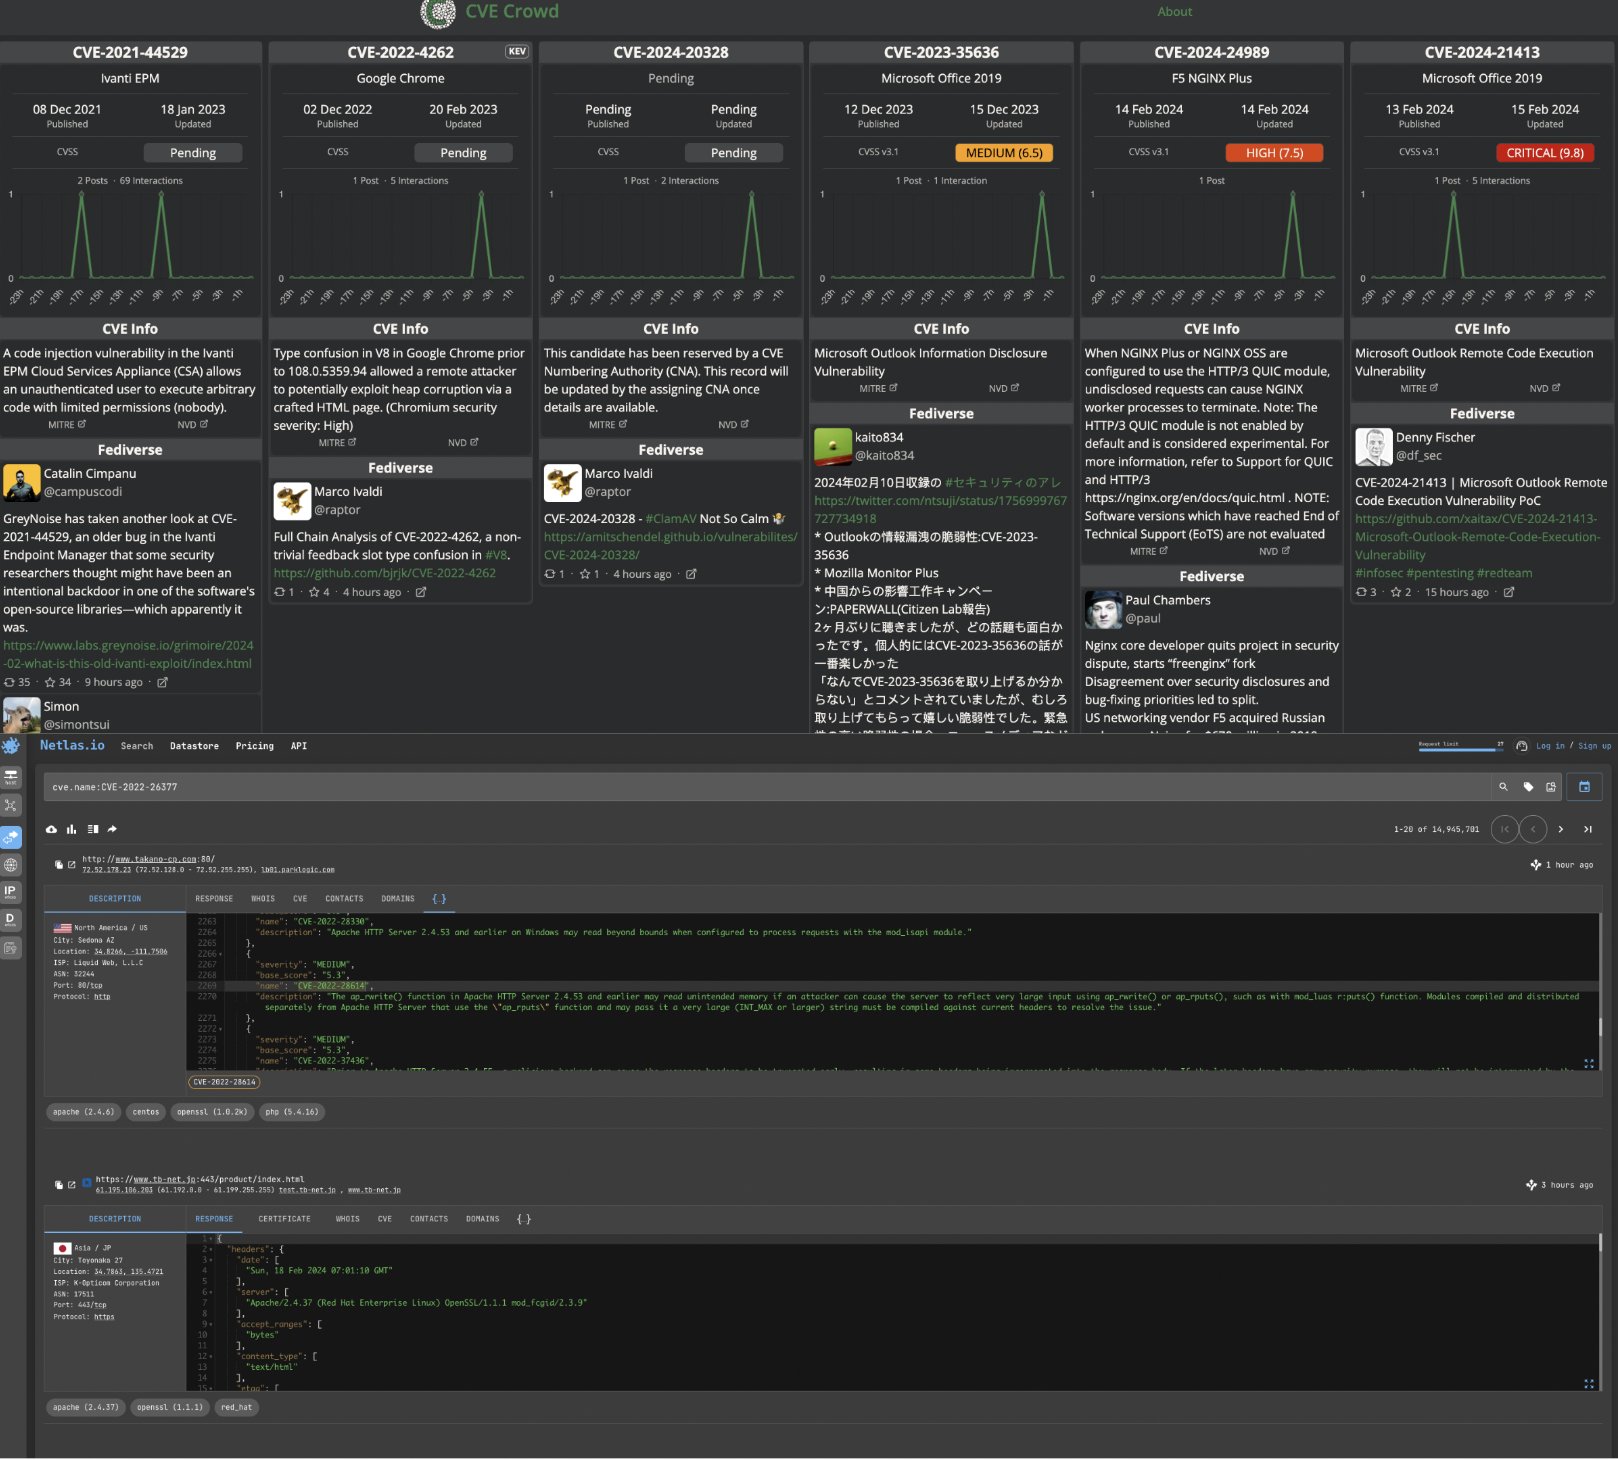
cvecrowd.com
Alternative to Cvetrends (stopped working due to Twitter API restrictions). Shows the most popular CVEs in Fidverse for the last 24 h.
Don't forget that servers with different vulnerabilities can be searched for free at app.netlas.io.
Markus Lassfolk retweeted

These vulnerabilities tracked as CVE-2024-23108 and CVE-2024-23109 (CVSS 10) could potentially allow remote, unauthenticated attackers to execute unauthorized commands through specially crafted API requests
#Fortinet #FortiSIEM
securityonline.info/cve-2024…

Markus Lassfolk retweeted

CISA is requiring all Federal agencies to disconnect Ivanti products by Friday at midnight (Ivanti Connect Secure & Ivanti Policy Secure). This is roughly 48 hours notice, to not patch, but rip it out! Ivanti is an American company. This is unprecedented.
cisa.gov/news-events/directi…
A deep dive by Truesec into the Ransomware group Akira's way of breaking into Enterprise environments , and how to protect yourself
truesec.com/hub/blog/akira-r…

Markus Lassfolk retweeted
QNAP Systems published security advisories for 15 vulnerabilities (from OS command injections to SQL injections), each posing a unique challenge to the integrity of their systems
meterpreter.org/security-ale…