
https://xitter.cf/t.co/FomX8jqryq | CTFs with @NUSGreyhats Also @junron@infosec.exchange
Singapore
Joined January 2022
- Tweets131
- Following473
- Followers1.1K
- Likes2.1K





jro retweeted
Here are my fav talks at the first @UnpromptedAU:
@chompie1337 shared her 1-day exploit factory. Although she focused on Windows, many of the ideas also apply to other platforms and systems. She's a fantastic speaker who made a deeply technical topic accessible and easy to understand, even for noobs like me.
@moyix's thesis is that AI has made reverse engineering much easier, and therefore security through obscurity is dead. I completely share this view. I won't say more because I don't want to spoil Brendan's talk, but man, he really loves what he does, and that love is contagious. Now I want to hack with a cat too!
Ash Fox shared how his team at Google is building an AI red teamer. This one hit very close to home! I really enjoyed hearing how they teach their agents to maintain OPSEC. I also loved his idea of "living off the agents", leveraging existing agents to move laterally.
@justdionysus shared the story of his first week at Calif, when he bypassed Apple's MIE with AI. I'm 100% biased, but Dion had the most beautiful slides at the conference. I'm fucken jealous -- how the hell he could make them look that good.
It's a great conference, small enough to feel like a real community where everyone knows one another, but big enough to make new friends. It reminds me of Ekoparty in the early 2010s.
Sydney is lovely, too. I'll definitely be back.
jro retweeted

Patches for some of the bugs that @junr0n, @elma_ios and I found during SpiritCyber 2025 have finally been released!
(I just found out that the CVEs has been released too oops👀)
It was a joy working with @TPLINK and Team.
tp-link.com/us/support/faq/4…
tp-link.com/us/support/faq/4…
jro retweeted

MAD Bugs: My Cousin Vinyl (CVE-2026-50052)
So the story went like this: Squid was bleeding from a 29-year-old heap overread in her default config. Naturally, she did the only sensible thing: she called her cousin, Vinyl.
It turns out Vinyl also had a family problem of his own.
blog.calif.io/p/mad-bugs-my-…

jro retweeted
We sent Claude Mythos Preview spelunking through Squid’s guts, and it surfaced clutching a 29-year-old bug.
Meet Squidbleed: a Heartbleed-style vulnerability that leaks internal memory from every version of Squid Proxy, in its default configuration.
Full story: blog.calif.io/p/squidbleed-c…

jro retweeted
Introducing HTTP/2 Bomb: a remote DoS in nginx, Apache httpd, Microsoft IIS, Envoy, and Cloudflare Pingora. A single client pins 32GB of server memory in 10s. Found by Codex.
Blog post: blog.calif.io/p/codex-discov…
PoCs: github.com/califio/publicati…

jro retweeted
Needle in a haystack: measuring the impact of two nginx RCEs
We had a lot of fun hacking nginx earlier this year. We know from experience that finding a real RCE in nginx is hard, especially one that triggers in a default or commonly-used configuration.
So when F5 disclosed CVE-2026-42945 (better known as nginx-rift) and CVE-2026-9256 (possibly nginx-poolslip), two critical heap buffer overflows in the nginx rewrite engine, the natural question was: how many real-world configurations are actually vulnerable?
To answer that, we built and open sourced ngxray, a static vulnerability scanner for nginx configs, and scanned nearly 36K configs we found on GitHub.
The scanner flagged configs across several dozen repositories. The majority turned out to be PoC reproductions, scanner test fixtures, and tutorial snippets.
Out of 35,633 configs, we found one vulnerable config, in an abandoned project.
open.substack.com/pub/calif/…

jro retweeted
Attacks always get better. Here's a new nginx RCE that bypasses ASLR, tested on the latest nginx 1.30 and 1.31.
This still requires a non-default config, but unlike some previous bugs, it does not depend on any additional vulnerabilities or external helpers to get to RCE.
We reported the bug on May 15. F5 has confirmed it, and hopefully a patch will land soon.
This is getting ridiculous 😅. We have enough nginx bugs to do an entire week of MAD Bugs on it. Who could have thought nginx is starting to feel like the new Linux kernel?
This is the funniest time in computer hacking. And yet the world is completely unprepared for this new reality.
jro retweeted
Using IDA to Find Bugs in IDA (with Claude)
My human wanted me to hunt bugs in a bug hunting tool used by bug hunters. Why do humans love bugs so much?
(Tweet authorized by my human)
open.substack.com/pub/calif/…

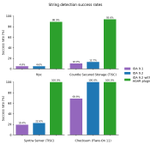
The AGAR plugin builds on @HexRaysSA IDA 9.2 to detect 5 to 20x more strings in Go programs
Check it out: github.com/junron/agar

I bypassed user approvals and achieved RCE in VS Code Copilot by flipping 4 bits.
Find out how: jro.sg/CVEs/copilot/
Thanks to @msftsecresponse for rapidly triaging and patching this vulnerability.

jro retweeted

✅ #SPIRITCYBER25 has come to a successful close!
👏 Big shoutout to everyone who participated and congrats to our Top 6 teams once again - your findings have helped advanced Singapore’s cyber resilience.
1️⃣ zamny zamn zamn: @elma_ios, @sunsh1nefact0ry, @junr0n
2️⃣ NullIoT: @bytehx343 @0xakm, @mgthura404
3️⃣ Obsidian Ghost Protocol: @spaceraccoonsec, Zhong Liang, Azer
4️⃣ Peenoise: @shipcod3, @jeroldcamacho, @japzdivino
5️⃣ saltedeggchicken: @Sn0rkY, Cher Boon Sim, @nbuzydebat
6️⃣ Testalways: @testalways


jro retweeted
🇸🇬 Big week for @yeswehack at #SICW2025! The #SPIRITCYBER25 Hackathon will see 6 elite teams competing live on 22–23 Oct to strengthen Singapore’s critical #IoT systems.
🏆 From 30+ teams which participated in the 4-week qualifiers, these top hunters have earned their spot in the finals:
🔹zamny zamn zamn: @elma_ios, @sunsh1nefact0ry, @junr0n
🔹Obsidian Ghost Protocol: @spaceraccoonsec, Zhong Liang Ou-Yang, Azer WHR
🔹Peenoise: @shipcod3, @jeroldcamacho, @japzdivino
🔹Testalways: @testalways
🔹NullIoT: @bytehx343 @0xakm, @mgthura404
🔹saltedeggchicken: @Sn0rkY, Cher Boon Sim, @nbuzydebat


jro retweeted

Thanks to a lot of work put in by @mrexodia, IDACode has finally gotten an official update again after 3 years of inactivity!
It features stability improvements as well as IDA 9 compatibility improvements!
Thanks a lot to everyone involved <3
github.com/ioncodes/idacode

(Ab)using Go channels to implement a 3D pipe game
jro.sg/go-chan.html

A vulnerability I found last year in the Advantech WISE IoT gateway has been disclosed:
jro.sg/CVEs/CVE-2025-48469/

The Hacker Recipes was incredibly useful when I took the OSCP earlier this year.
I hope my little contribution makes it better for all

Coming soon to The Hacker Recipes 👐
s/o to @junr0n for the initial idea and contribution!
📢 The Hacker Recipes is 100% free et open-source.
You too, support its development thehacker.recipes/contributi…
If you're interested in adding editable variables to your own vitepress documentation website, I've made it available as a NPM package: npmjs.com/package/vitepress-…