
building security at https://xitter.cf/t.co/mBie3u14lP
France
Joined April 2010
- Tweets437
- Following1.1K
- Followers549
- Likes4K

Grégoire Clermont retweeted

By using AI for writing, you’re robbing yourself of the authentic writer’s experience of not writing
Grégoire Clermont retweeted

From 2020-2024, I tracked the SolarMarker malware, and in 2024, monitored a self-infection for months to learn their actions-on-objectives: on-device fraud.
I didn't publish the details of my months long investigation until now. Check the link the the attached comment.

Grégoire Clermont retweeted
CertCentral is now TheCertGraveyard[.]org & CertGraveyard[.]org.
The CertCentral API returns an error directing to use the new domains.
Please give me a like or a share to get the word out.
Also use the site to report and investigate certificates used to sign malware. :)

Grégoire Clermont retweeted

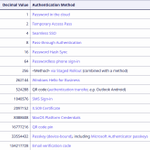
Our latest technical deep-dive unravels the mystery behind the opaque numeric codes (16, 272, 33554432, etc.) you see in #Microsoft365 audit logs.
buff.ly/w04flj1

The #UserAuthenticationMethod field of the Microsoft 365 sign-in logs contains numeric values (16, 272, 33554432...) that were not documented anywhere.
I figured out that it's a bitfield, and recovered the meaning of most of the bits!


The results and methodology are detailed on the @sekoia_io blog:
blog.sekoia.io/userauthentic…
Several bits remain unmapped (bits 5, 7, 9-17, 22, 26). If you observe these values, please share your findings!

UserAuthenticationMethod 16457, of SolarWinds fame (and that doesn't seem to exist anymore) remains a bit of a mystery to me.
I'm not sure if it could be decoded in the same way (bits 0, 3, 6, 14?)
xitter.cf/ItsReallyNick/status/1…

Grégoire Clermont retweeted

"Uncovering the Chinese Proxy Service Used in APT Campaigns" published by Spur. #Kimsuky, #DPRK, #CTI spur.us/how-spur-uncovered-a…

Grégoire Clermont retweeted

I love Cloudflare, but the number of phishing sites I find sitting behind Cloudflare or utilizing Turnstile is excessive.
Grégoire Clermont retweeted

New RE Blog Post: RustyPages-Pt1
the-sequence.com/rustypages-…
We RE a Rust dropper, that sets persistence and runs the downloaded next stage, queries @patrickwardle's tools, and quiets notifications. We included relevant IOCs as we continue our analysis of the loader for Part 2. :)
Grégoire Clermont retweeted

New Microsoft Graph based API for response actions in #MDI
Disable, Enable, ForcePasswordReset and RevokeAllSessions finally available for your automations.
learn.microsoft.com/en-us/de…

ALT POST /security/identities/identityAccounts/{identityAccountsId}/invokeAction

Grégoire Clermont retweeted

Aaand we (or mostly Fabian) made this cool website where you can explore all these first party apps and their scopes at entrascopes.com xitter.cf/fabian_bader/status/19…

One of the results of the joined research with @_dirkjan is entrascopes.com/
Basically the yellow pages for Microsoft first party apps.
#TROOPERS25

Grégoire Clermont retweeted
Coming up on my 1 year anniversary with @HuntressLabs !
Taking this opportunity to go over some things myself and the team have seen in intrusions and drop some tips on basic things you can do to make your network more immune to compromise.
Let's start with initial access
- We see so much VPN compromise, it's by far our number 1 initial access vector - yes 0days for VPN appliance are there, but most of the time the compromise is a result of good ol' fashion credential stuffing or brute force.
- Some VPN appliances have decent log retention, others do not and it really sucks when only ~1 hour worth of logs are available - if you're standing up a SIEM or any kind of log collection effort in your org, make sure that devices which are externally exposed are sending their telemetry to the SIEM. If your VPN appliance has different logging settings, check them out and enable as needed - this telemetry is gold during intrusions.
- In addition to VPN appliances, we see a lot of RDP / RDS machines get compromised - same story here, no fancy 0days, just weak credentials in use. In some cases, MFA is in use, but has either been bypassed for the compromised user or has "failed open" - if you use RDP for your org, make sure that MFA is enabled somehow on it, if it is enabled, test to see what happens when the process that handles MFA crashes or is turned off. Also, make sure you have good procedures in place for turning MFA bypasses back off when they're applied.
- Remember to keep an eye on your web applications, deserialization attacks aren't super common, but happen fairly often. Turn on IIS logging and enable POST request logging if possible. Remember that a standard penetration test often does not deep dive into custom web applications, invest in a good Appsec focused test if you have a custom application exposed externally.
Turning to lateral movement
- Once inside networks, threat actors move very quickly and unfortunately do not run into a lot of resistance. We typically see multiple accounts compromised in rapid succession, suggesting weak or shared passwords in use. You have no idea how happy it makes me to see "LOGON_TYPE_NOT_GRANTED" in the logs - Yes I know segmenting your network is probably a pain, but its a very effective security control.
- In most cases we see, RDP is used for lateral movement and unfortunately, there is often no controls to prevent users from RDP'ing into servers they have no business need to RDP into. Check your Active Directory permissions and see what users can RDP into your file servers and domain controllers, you might be very surprised by what you find!
- Impacket & impacket-related tooling is very popular for lateral movement, if you are in charge of defending a network and have telemetry and a lab environment, try to use WMIExec etc for yourself and compare the telemetry you see versus normal activity, this is a great way to build high-fidelity alerts. Aside from that, remove local admin where possible. Local admin rights enable credential access and lateral movement avenues that would be shut right down were a non-admin account in use.
Looking at Execution / Impact
- Do threat actors use fancy 0days ? Yes of course, but in the cases we work, we rarely see it. Most of the time, "just enough tradecraft" is employed, all a TA needs is FileZilla and 7Zip to ruin your day.
- Tunneling tools like ngrok and plink are very popular, most often, these tools are being used to make RDP externally available to the TA - everyone loves a GUI I guess.
How do adversaries get credentials ?
- Registry credential dumping is extremely popular, same with LSASS credential dumping. Threat actors will also search local file systems and network shares for credentials and - guaranteed - will find them. By segmenting your network, limiting local admin access and hardening authentication silos within your AD environment ( things like a three-tiered admin model, or as close to it as you can get ) will limit the impact of credential theft drastically.
- Brute forcing is old and boring I get it, but unfortunately it works, especially for less-monitored environments, some cases we've seen hundreds of thousands brute force attempts for hours before an account is successfully compromised. Don't sleep on brute forcing, ensure you have account lock out policies in place and some kind of monitoring for brute force attacks.
Miscellaneous tidbits
- Please, please, please - change your default Windows log sizes via GPO. By default, these log channels do not hold a lot of data, if a threat actor undertakes a brute force in the environment, security-relevant telemetry will be clobbered hampering any investigation efforts.
- Have a standard naming convention for your organizations' workstations and servers, this makes it so much easier to orientate everything during an investigation and very often bubbles up malicious activity for workstations that don't fit the standard naming convention.
- Have a plan in place in case of an incident, it's bound to happen and it's better to be prepared. What happens if certain hosts need to be offline, who do you call to get a potential insurance claim started? What is the threshold for a formal IR engagement - deciding all these things under pressure from an incident is not ideal.
I think this post is long enough 😅 so I'll wrap it up 💙
Grégoire Clermont retweeted

Hello Defenders
I've been writing a few blogs about #BEC activities 🎯 — especially focusing on common attack techniques in Persistence and recent trends showing how BEC attacks are evolving. If you're curious, please check them out 🚀
✅ Blog : kijoninja.medium.com

Grégoire Clermont retweeted
Cert Central has an unauthenticated API endpoint to return the database as a csv: certcentral[.]org/api/download_csv
It is currently used in CCCS' AssembyLine as a blacklist.
@SecurityAura has used it for threat hunting.
Looking forward to see what others do with it.

Grégoire Clermont retweeted

some cool #Elastic detections added by @_w0rk3r to identify potential kerberos SPN Spoofing via the CredMarshalTargetInfo primitive (abused in CVE-2025-33073 and also in other Kerberos reflection attacks):
synacktiv.com/publications/n…
github.com/elastic/detection…
github.com/elastic/detection…


Grégoire Clermont retweeted

We are excited to share our latest blogpost on AitM phishing threats - covering common TTPs, the PhaaS ecosystem, the most widespread kits, and multiple detection opportunities!
xitter.cf/sekoia_io/status/19327…
w/ @gregclermont


Grégoire Clermont retweeted

LUCR-3 (ScatteredSpider, UNC3944, OctoTempest) TTP Series continues with:
Topic 2: Data Theft in Github
- Log into the GitHub UI with a browser session
- Generate a Personal Access Token (PAT) //Even though they don't use it!
- Skip git clone, download repos directly as .zip files