

I.T. Telecomunicaciones, creador y ex-organizador de @MorterueloCon, Gordaco de @quebrantarugby, creador de @opensecdevops
Joined November 2008
- Tweets14.9K
- Following1.5K
- Followers2.8K
- Likes25.3K



goldrak retweeted

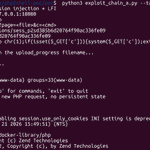
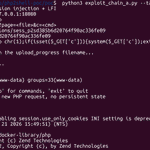
#CVE-2026-109618 PoC #exploit para #php2shell de cosecha propia ejecutado en un entorno controlado XD tras detección con github.com/pentestershell/ph…
👇

dejo esto por aquí:
👇
php2shellbt is a standalone Python scanner that detects the php2shell vulnerability chain in PHP web applications — with zero external dependencies (pure stdlib).
github.com/pentestershell/ph…
De nada XD


goldrak retweeted

shadcn registry for healthcare
👉 organui.com
more like this on → shoogle.dev/directory


goldrak retweeted

Qué contento estoy con mi app híbrida en PHP y Node que estoy desarrollando usando LiteLLM y OpenCode, alojada en mi GitLab self-hosted y con certificados de eMudhra.
goldrak retweeted

Contra todo pronóstico y sin aviso previo, Ondřej Surý ha aplicado los parches CVE-2026-109618 y CVE-2026-109619 tanto para PHP 5.6 como para PHP 7.4. En el log aparece: "Backported from 8.2.35". Nos ha salvado el culo a los que tenemos servidores Debian/Ubuntu.
goldrak retweeted

Los que se reían de PHP esta mañana, revisad vuestro Node.js.
Node.js ha parcheado hoy 4 vulnerabilidades de gravedad alta. El mismo día que PHP. Aquí no se libra nadie.
La más grave, CVE-2026-111497, está en el decodificador Brotli y, según Node.js, permite ejecutar código en remoto.
Pero la que más me preocupa es otra: dos fallos permitían saltarse la comprobación del nombre de host en TLS.
Tu aplicación puede dar por bueno un certificado que no es del servidor con el que habla.
El candado sigue ahí, pero ya no garantiza nada.
Si tienes algo en Node.js:
➡️ Ejecuta node -v. Si es anterior a la v22.23.4, la v24.22.1 o la v26.12.1, actualiza
➡️ Si despliegas con Docker, reconstruye la imagen. Actualizar tu equipo no cambia lo que está en producción
➡️ Si sigues en Node.js 18 o 20, no hay parche para ti: toca migrar
goldrak retweeted

if this PHP vulnerability allows remote code execution, doesn't that mean we can use the vulnerability to auto-patch all vulnerable servers?
goldrak retweeted

You COULDNT HAVE FUCKING WAITED 14 Hours.
i hope your forever blacklisted from cybersec/related industries for dropping a unpatched critical 1day on twitter you fucking idiot
This quoted post is unavailable.
goldrak retweeted
Claude, reescribe WordPress completo en Rust. Sí, también todos los plugins y todos los temas. No, no me refiero al repo local: quiero decir que vayas y sustituyas la instalación de WordPress de todo el mundo servidor por servidor.
Que no tienes acceso, dices? Verás, te cuento…

The NCSC is encouraging UK organisations to prepare for immediate updating of systems using PHP. Where immediate remediation is not feasible, organisations should consider taking the system offline until it can be fully mitigated.
For more⬇️
ncsc.gov.uk/news/critical-se…

goldrak retweeted

Not just PHP. Node.js has also announced security releases for October 21, with HIGH-severity vulnerabilities affecting its 26.x, 24.x and 22.x release lines.
If you run either stack in production, keep an eye on official advisories and apply patches promptly.
Security maintenance doesn't stop at your application code. Your runtime matters too.
Node.js advisory: nodejs.org/en/blog/vulnerabi…

goldrak retweeted
At 14:00 UTC two critical security vulnerabilities will be patched in PHP.
These are extremely serious vulnerabilities affecting every PHP application on the web.
Laravel Cloud customers: we will begin automatically patching your applications as soon as the patch is released. No manual action is required.
Laravel Forge customers: you will need to manually update your server’s PHP version via the server’s Forge dashboard. If you are unable to update your server, it should be powered down.
Laravel Vapor customers: we will begin automatically re-deploying applications running on PHP 8 as soon as the patch is released. No patch is being released for PHP 7 -- immediately update all applications to PHP 8.
goldrak retweeted
A moron has released a POC early for php2shell so here is what you need to do:
If you’re on version prior to 8.2:
Edit php.ini: session.upload_progress.enabled = Off
Then reload php-fpm and restart apache
If you’re on later version:
Update (it’ll be available in a few hours)
In any case, the mitigation for the php.ini should work either way. Not sure if it’ll cover both vulns though so keep an eye on that. I’ll be reporting on follow up activity on windows as a target.
Good luck!
goldrak retweeted

Honestly, it's pretty disappointing to see responsible disclosure fail like this. It takes a lot of effort to release a critical patch.
Leaking the announcement or publishing a PoC before a scheduled patch shows you have no ethics and are only interested in credit for yourself.
goldrak retweeted

The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
goldrak retweeted

ok devs, assemble.. we're live on product hunt
make some noise: producthunt.com/products/dev…

goldrak retweeted

IKEA manuals, but they come to life.
I built the real BILLY instructions in 3D, so you can watch every step happen exactly as drawn. try it: sael.net/flatpack
