

#C43S4RS | pentester | Security Researcher | #Gryffindor | Formador | #SoyCapaz | 🇪🇸 | pro-NANO | Mentor NCL @GuardiaCivil | EX-Comanfes.
~π~÷׶÷∆••~π~~π~~π~π÷~π~÷׶÷∆•
Joined December 2012
- Tweets33.7K
- Following2.1K
- Followers36.5K
- Likes43.5K


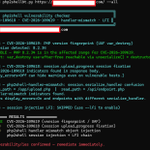


Joder, me estáis saturando el puñetero dm XD , parad gente, la respuesta es:
Not yet—let's wait for the patches to be applied, and then I'll release the exploit. 😜

#CVE-2026-109618 PoC #exploit para #php2shell de cosecha propia ejecutado en un entorno controlado XD tras detección con github.com/pentestershell/ph…
👇

BTshell🕷 retweeted

💥 #PHP2shell: encadenando peticiones HTTP hasta el RCE.
Analizamos la vulnerabilidad, diseccionamos la explotación y exploramos cómo reproducirla en un laboratorio controlado gracias a Enes Sönmez.
🔬 Análisis técnico, PoC y laboratorio en Hackplayers: hackplayers.com/2026/10/php2…

BTshell🕷 retweeted

Un verificador en PowerShell 100 % pasivo para PHP2Shell (CVE-2026-109618 / CVE-2026-109619).
Fork del script original de @BTshell para los que preferimos Powershell y con alguna que otra mejora menor. 🤪
github.com/alex-milla/php2sh…


BTshell🕷 retweeted

🚨 ÚLTIMA HORA: Grandes bancos estadounidenses, incluidos JPMorgan, Bank of America, Morgan Stanley y Wells Fargo, están detectando agentes de inteligencia artificial de terceros operando dentro de cuentas de clientes sin autorización de las entidades.
Según Axios, algunos agentes incluso han intentado realizar acciones que parecen ser independientes de las instrucciones de los usuarios.
Bueno y que esperaban?
#CVE-2026-109618 PoC #exploit para #php2shell de cosecha propia ejecutado en un entorno controlado XD tras detección con github.com/pentestershell/ph…
👇
dejo esto por aquí:
👇
php2shellbt is a standalone Python scanner that detects the php2shell vulnerability chain in PHP web applications — with zero external dependencies (pure stdlib).
github.com/pentestershell/ph…
De nada XD

BTshell🕷 retweeted

🚨 PHP2Shell (CVE-2026-109618/CVE-2026-109619)
Nuclei Template : github.com/projectdiscovery/…
Reference: calif.io/php2shell/
#hackwithautomation #php2shell

BTshell🕷 retweeted

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
Le he metido algunas mejoras, creo que ahora es mejor, ya me contareis XD
dejo esto por aquí:
👇
php2shellbt is a standalone Python scanner that detects the php2shell vulnerability chain in PHP web applications — with zero external dependencies (pure stdlib).
github.com/pentestershell/ph…
De nada XD
BTshell🕷 retweeted

He usado esta, Tu captura es de otra que desconozco.
github.com/pentestershell/ph…
Buenos días y MUCHO OJO a la cantidad de exploits que están saliendo para #php2shell que lo mismo llevan sorpresa, recordad que los malos no descansan.

dejo esto por aquí:
👇
php2shellbt is a standalone Python scanner that detects the php2shell vulnerability chain in PHP web applications — with zero external dependencies (pure stdlib).
github.com/pentestershell/ph…
De nada XD
Y ojo, tengo exploit ya, pero por responsabilidad no lo voy a subir hasta que todo este tema de #php2shell quede bien resuelto xd
Es muy fácil de comprobar :) espero que os sirva.

dejo esto por aquí:
👇
php2shellbt is a standalone Python scanner that detects the php2shell vulnerability chain in PHP web applications — with zero external dependencies (pure stdlib).
github.com/pentestershell/ph…
De nada XD
BTshell🕷 retweeted
PHP lanza parches urgentes para corregir fallos críticos de PHP2Shell
El equipo de PHP lanzó parches de emergencia para corregir dos vulnerabilidades críticas de ejecución remota de código (RCE), conocidas colectivamente como PHP2Shell, que afectan a casi todas las instalaciones de PHP.
Debido a que permiten ataques sin autenticación y ya se han detectado intentos de explotación, se insta a los administradores a actualizar inmediatamente a las versiones más recientes (8.x). Para versiones obsoletas (7.x y anteriores), se recomienda migrar o aplicar parches mínimos proporcionados por el equipo de seguridad
blog.elhacker.net/2026/10/ph…
BTshell🕷 retweeted

Acabo de recibir una llamada brutal de PHISING desde un número de teléfono español, de alguien con acento de España.
El tío controlaba. Le he seguido el rollo todo lo que podía aunque me hervía la sangre: 4 o 5 minutos.
Se hacía pasar por Trezor.
- Tenían mi número de teléfono, mi nombre y mi email.
- Desde este numero: 622 748 592
- Al final me hacía ir a trezormanage (punto) io. Supongo q esto acababa con el pidiéndome alguna frase semilla.
- Me escribía emails durante la llamada con links desde support@trezor via inbox-management (punto) com - Vamos, q no era desde trezor. Tenía todos mis datos.
Me jode pero en algún momento he metido la pata con mis datos, está claro. No tengo ninguna trezor, además.
La conversación ha acabado diciéndole que ya paraba la broma y q como podía vivir con la vergüenza de robar a la gente y si puede dormir por las noches. Es increíble que haya escoria de este calibre por el mundo, pero es así.
Cuidado si recibís alguna llamada.