

L3 and beyond
Joined June 2022
- Tweets1.7K
- Following3.4K
- Followers499
- Likes6.5K




empty retweeted
We are currently experiencing a service disruption affecting multiple services. We can confirm that all our customers’ money and data are safe. We’ve been working to fix the issue since it was identified this morning and apologise to anyone affected and for any inconvenience caused.


empty retweeted
Love Coinbase’s USDC lending and crypto-backed loans, both powered by @Morpho? @Base just made it easy to offer Morpho in your own app.
Your users get access to $5B+ in deposits on Morpho on Base, the deepest USDC lending liquidity onchain.
Coinbase strategy is an absolute positive-sum masterclass:
→ Each new integrator adds liquidity to Morpho, which makes Coinbase’s own consumer lending products better
→ Every Coinbase user who lends or borrows deepens that Morpho liquidity, which makes things better for every partner building on Base.
Each side makes the other stronger.

empty retweeted

Disappointed by the European Central Bank’s (ECB) and European Banking Authority’s (EBA) responses to the MiCA consultation.
They are not only advocating for a prohibition on paying yield on stablecoins, but also for restrictions on CASPs providing access to DeFi, including protocols offering yield on non-MiCA-authorized stablecoins, without providing a clear framework for how access to DeFi should work in practice.
They also suggest that CASPs offering access to DeFi should restrict it to certain groups of users through so-called “suitability tests,” alongside a potential certification regime for DeFi lending protocols.
It is unclear how these requirements would work in practice. If regulators determine which protocols are deemed suitable for European users, the result risks looking very different from the open DeFi that exists today.
Instead, we could end up with more walled gardens that undermine the liquidity and network effects of open financial networks, ultimately limiting Europeans’ ability to access new ways to grow and preserve wealth.
These proposals are presented as measures to “protect consumers.” But excessive restrictions can instead create more friction for innovation and slow the development of open, transparent, and auditable financial infrastructure that can benefit consumers.
The reality is that onchain finance, including stablecoins, DeFi, and tokenized securities, has the potential to reshape financial infrastructure by reducing friction, increasing transparency, and expanding access to financial opportunities.
European consumers and businesses stand to benefit significantly from this transformation, particularly if the companies building this infrastructure can continue to build and compete from within Europe.
Meanwhile, U.S. regulators, including the SEC and CFTC, have increasingly taken a more pragmatic approach toward enabling onchain financial innovation.
European regulators should put users and their interests at the center of the framework. Banks and other incumbents should be able to adapt their businesses to serve users in an increasingly onchain economy, rather than relying on artificial restrictions that risk increasing costs and reducing access for Europeans as the rest of the world moves onchain.
DeFi will win.
empty retweeted

⚠️ Beware if you use a Ledger hardware wallet, especially if you bought one recently.
Based on information so far, it seems to be localized to a supply chain attack with one vendor. A small number of people probably bought fake (or tampered) Ledgers.
Ledger is one of the most secure and oldest hardware wallets in the industry. Stood the test of time. But these things happen.
I expect and know all BNB ecosystem players (and all industry) to help trace and recover the funds.

Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBillis. As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices. We recommend Ledger users who purchased from this reseller in the last 90 days to not initiate set up if you have not done so yet. If you have set up your Ledger device, consider moving assets to a new Ledger signer (with new seed). We will continue to inform customers of updates as the investigation progresses.
Reach out to Ledger customer support through official channels with any questions: support.ledger.com/
empty retweeted

Rain has filed with the @USOCC to establish Rain National Trust Bank.
If approved, the bank will:
1. Provide fiduciary custody of digital assets and dollars
2. Manage reserves for permitted stablecoin issuers
3. Issue and redeem USD-backed stablecoins
Rain will stay a payments platform. It will not take deposits or make commercial loans.
Brandon Soto, former CFO of Square Financial Services and most recently CFO of Coastal Financial Corporation, will serve as the proposed President and CEO of Rain National Trust Bank.
The public portion of the application will be posted on the OCC's website shortly.
Full press release linked below.
empty retweeted

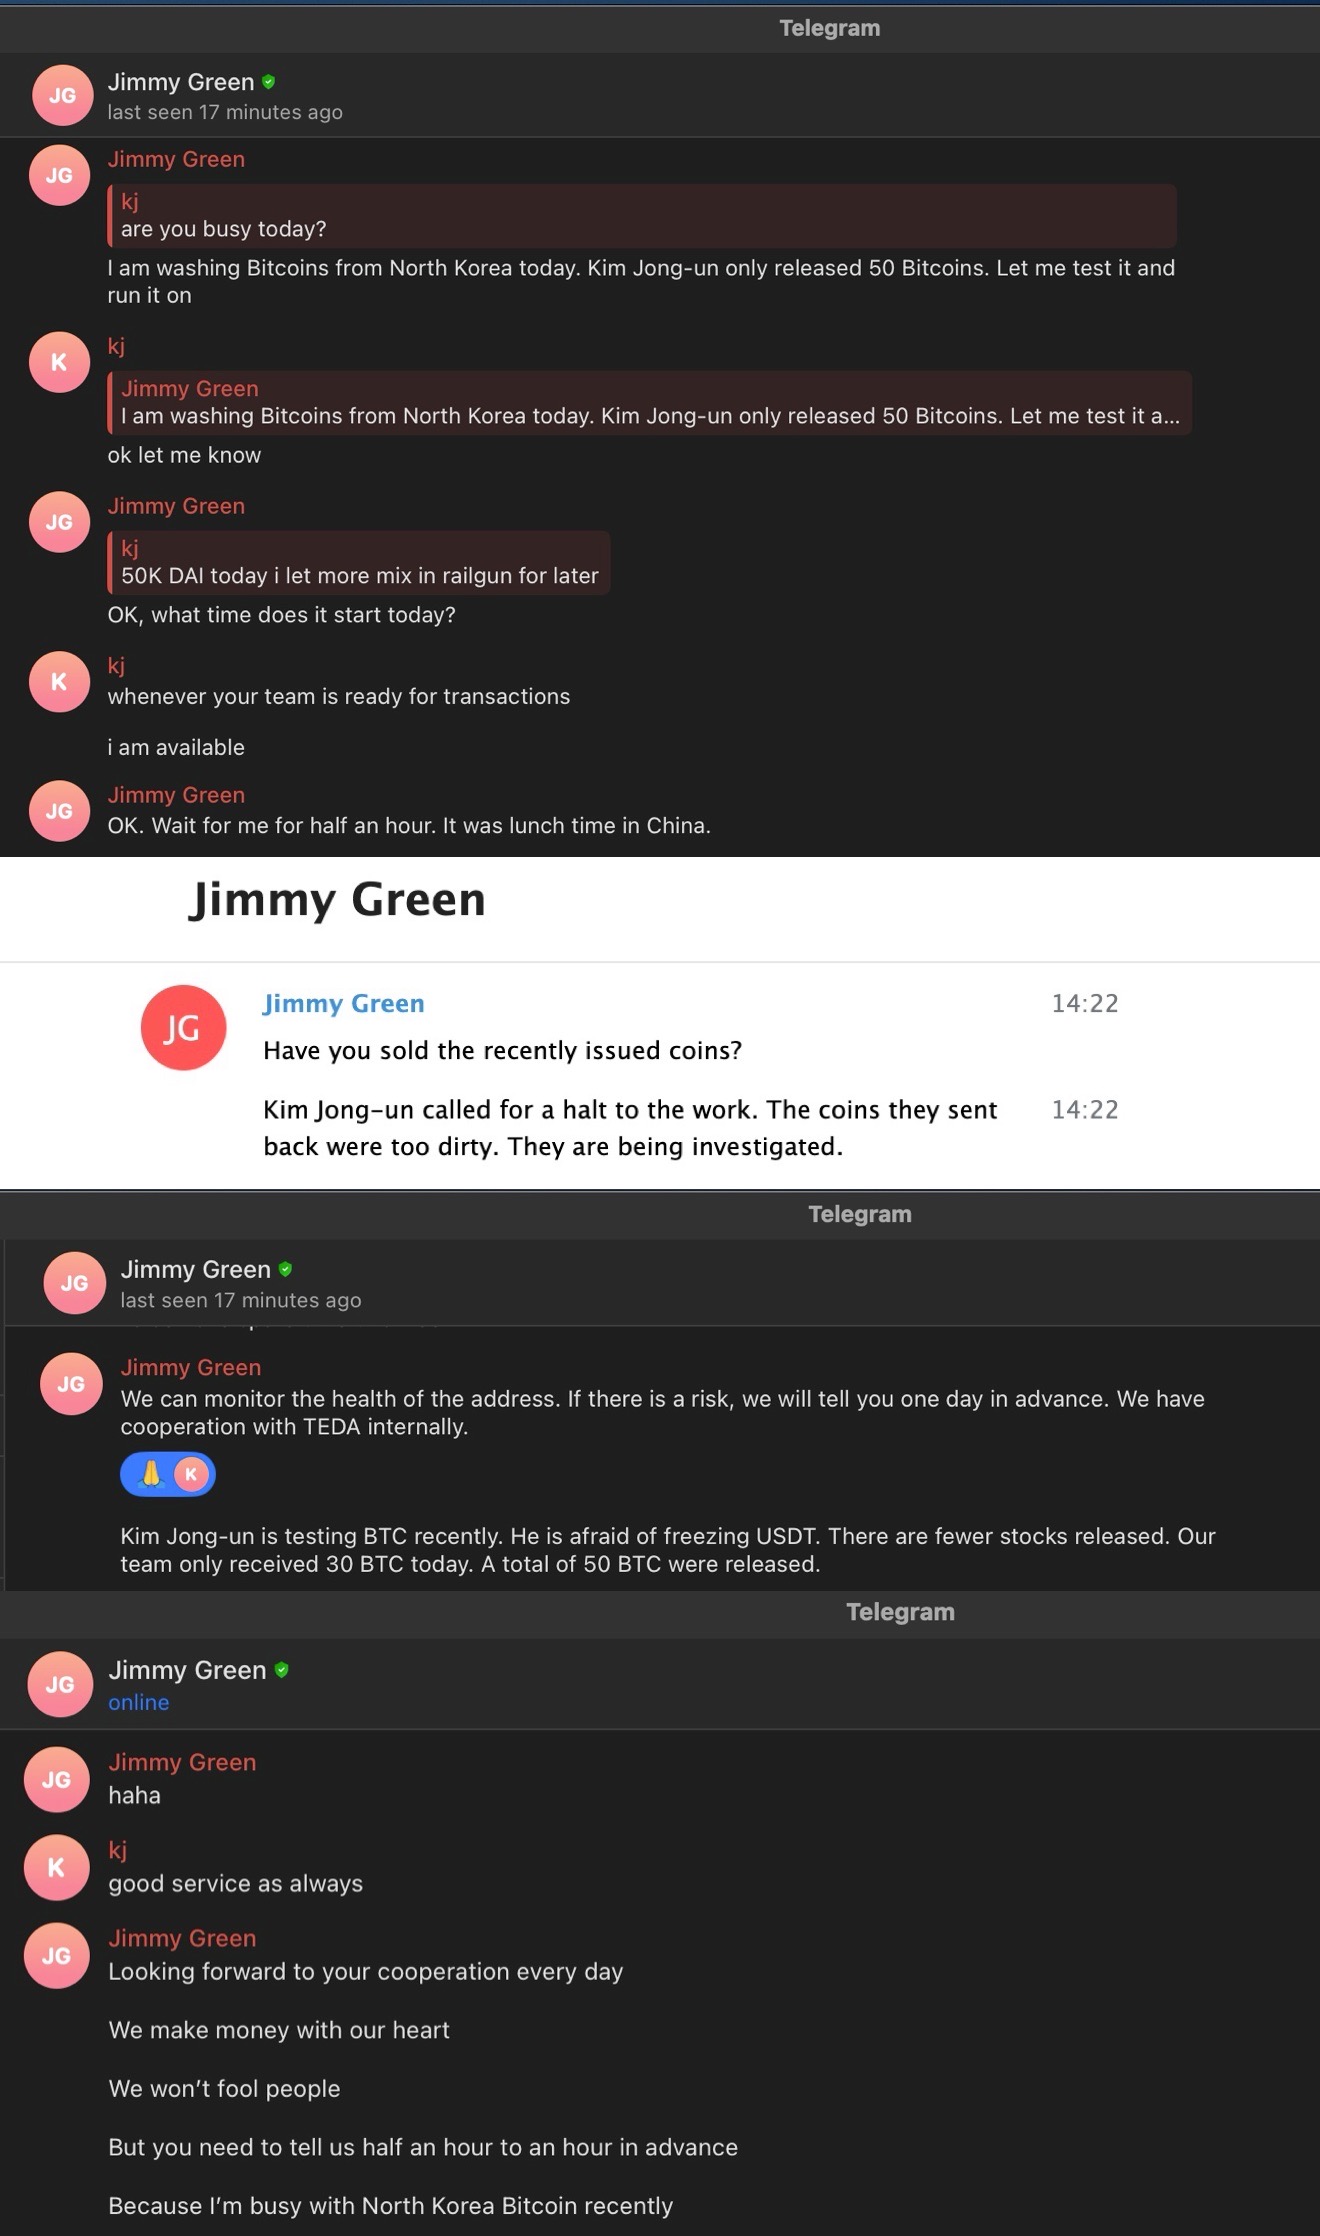
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.

empty retweeted

CT has been live 1 day.
Spot trading on @binance Alpha, @okx, @coinbase, @bitget, @Gate, @MEXC, @krakenfx, @kucoincom, @bitvavocom.
Perpetuals on: @binance, @okx, @bitget, @Bybit_Official, @Gate, @MEXC, @kucoincom, @Aster_DEX.

empty retweeted

I’ve seen a couple of posts about this so wanted to demystify. Today, every Muse user gets a free computer in the cloud. It's a real computer, and we’ve designed the security architecture of the Muse Secure VM carefully so you and your Muse can do almost anything you could with a computer sitting under your desk while keeping you and the system safe from threats like prompt injection. We wrote about this at length in our security blog post – security.muse.ai. Activity in the “runtime cell”, which you share with your Muse is unfettered, but sensitive actions are all overseen by the Sentinel, which runs outside of that cell. Similarly, all sensitive secrets - like the passwords you enter into Muse’s secure credential storage - are also stored outside the runtime cell.
The runtime cell gets its own root filesystem (including a full Ubuntu linux image) separate from the host filesystem where your other more sensitive data lives. Because it is isolated from the sensitive stuff that runs on the same box, this means that we can, and do, offer users full visibility and control over the files in the runtime cell. Just as you can when you install Linux on your home computer, you can poke around and see all the files that make the system work - both debian system files and the binaries and data files that implement the parts of Muse which run in the runtime cell.
This was a very deliberate choice - your Muse Secure VM truly is your own computer in the cloud. You can install software in it, write and compile code, use the browser to surf the web: it is your own Linux box that you can operate as you choose with your Muse. Poking around in this computer doesn't give you any privileged access to Meta infrastructure, or to other people's data
If I may geek out a little here for a second… As a kid I loved to take things apart to see how they worked. As a teenager I got into computers and soon found myself drawn to C:\WINDOWS\SYSTEM and the system registry, later Slackware’s /dev/, /proc/ etc – I could see how the system was laid out and as I explored what DLL files and .so files actually did, I gradually became able to meld the computer to my own will.
We’re really proud to be able to put a real computer in millions of people’s hands with a similar level of transparency. We built a file explorer right into the Library tab of the UI. We want you to be able to see the markdown files Muse writes while it thinks about how to serve you better, and explore the internals of the system if you’d like to.
So, when you ask your Muse to show you its entire filesystem, and receive gigabytes of files you’re seeing the full contents of the runtime cell. It’s yours to explore and enjoy!
If you’re not a geek like me, or simply want to download the data that you personally have created directly with your Muse, we added a feature for that too in Settings > Data controls > Download your agent data.

empty retweeted

Bot detection & human verification will be one of the most urgent demands for businesses over the coming years. Agent swarms will suffocate every website and form; small companies and government websites are most vulnerable.
There is a huge gap in the market for this right now. When we looked at what offerings were in the market to use at X, there was not a single company that brought together all the latest technologies so we had to do it all in-house.
empty retweeted

DigitalOcean Managed Agents is now in public preview.
Run Claude Code, Codex, or your own LangGraph agent in a runtime environment that pauses when idle. Put its tools behind one governed endpoint, and pick from 75+ open and proprietary models. One cloud, one bill.
Prompts to get started available in the blog: do.co/4ysh3it
empty retweeted

Our latest research paper explores the growing connection between AI and digital assets and explains why broad AI adoption may drive new demand, utility and applications across the digital asset economy. blackrock.com/us/individual/…


empty retweeted
muse is going NATIONWIDE to a television near you
this is our first @muse ad ever, going live this weekend! we hope you like it while watching the big game(s)!
big ups to @joshginsberg, denise, and the whole meta marketing team ❤️
empty retweeted

The team at @derivexyz is an example of courage and persistence. They have been building single-mindedly towards programmable derivatives onchain since the dawn of onchain finance >4 years ago. They started with a large cohort of peers that wanted to solve a difficult and important problem, and persisted while most gave up and settled for incremental improvements on established products and points campaigns.
Derive is now doing >$6B of convex programmable derivative volumes onchain.
Programmable derivatives are the flower of the onchain financial system, and they require the type of convex payouts that can be uniquely created on Derive.


Yesterday, we were Lyra.
Today, we are Derive.
Tomorrow, derivatives change forever.
🐎 derive.xyz
empty retweeted

For the opsec-minded folks, I think it's a really hard sell to connect your primary email (and not a burner) to any "Chief of Staff" agent right now (Instinct, Grok Bot, Muse).
Sure, you can do emails and restaurant bookings 2-5x faster, but you are now exposing yourself to asymmetric downside. Most apps handle OTP + account recovery through just your email, so a single hack can compromise your entire digital life.
For the crypto folks: this is reminiscent of chasing that 20% DeFi yield on that new shiny app, with the asymmetric risk of losing your entire balance because of a 0-day.
empty retweeted
1/
The SEC granted a five-year "Innovation Exemption" today letting onchain AMM venues trade tokenized stocks without registering as exchanges. Here's what's in it, and what isn't 🧵
empty retweeted

let me help you:
1. payward trading
2. payward banking
3. payward asset management
4. payward services
all the entities you drew sit within 4 pillars; eventually we'll vertically integrate more products so that any customer, institution in the world can risk manage the same way citadel does in microseconds. reduce the intermediaries to zero including us... we will innovate and disrupt ourselves for best in class products.

all of this is cool, but i wanted to figure out who @Payward actually is and what Kraken has to do with it
tldr: it's the top-level parent company, and Kraken and xStocks sit under it
along with some Bitnomial and NinjaTrader, which got acquired for one main reason, they already held DCM, DCO and FCM licenses, which let you issue futures and list them, clear them yourself, and onboard clients with KYC
anyway, did some research, dropped all the connections in the chart below

empty retweeted

New evidence shows: (1) @Revolut did apply the one refusal ground the law gives it. (2) the attackers targeted in their malicious request high-value clients using blockchain transactions.
Documents show that on 24 July 2026, on a request covering 198 hashes, Revolut refused direct disclosure for 169 tied to Revolut Ltd (UK) and 29 tied to a Swiss entity, redirecting the requester to UK mutual legal assistance.
Only accounts held at Revolut Bank UAB in Lithuania were treated as covered by the EIO. The refusal ground available to Revolut was jurisdictional. They APPLIED it.
EU AML law imposes no verification duty on the bank and provides no meaningful mechanism to check who is really behind an authenticated state request. Refusal to answer carries fines in the millions. In practice, verification is impossible.
Now, how the attackers targeted high-value clients? Per Duel's verified .eml files, they used public blockchain data as query keys.
Hundreds of crypto transaction IDs and deposit wallet addresses tied to suspected high-value Revolut users were submitted under the forged EIO cover. Revolut returned encrypted zip files with folders of ten customers each, ID pictures, verification selfies, account data, unredacted transaction data, with the password sent in a follow-up PEC.
Anyone whose wallet address appears on-chain can be turned into a target this way. Self-custody does not close this door: the moment your KYC data sits with a regulated intermediary, the same channel opens.

Very important that @Corriere covers this issue. Two points missing from the reporting so far:
(1) @Revolut did apply the one refusal ground the law gives it. Documents show that on 24 July 2026, on a request covering 198 hashes, Revolut refused direct disclosure for 169 tied to Revolut Ltd (UK) and 29 tied to a Swiss entity, redirecting the requester to UK mutual legal assistance.
Only accounts held at Revolut Bank UAB in Lithuania were treated as covered by the EIO. The refusal ground available was jurisdictional, not verification.
EU AML law imposes no verification duty on the bank as to who is really behind an authenticated state request, and refusal to answer carries fines in the millions.
(2) How the attackers targeted high-value clients: per Duel's verified .eml files, they used public blockchain data as query keys. Hundreds of crypto transaction IDs and deposit wallet addresses tied to suspected high-value Revolut users were submitted under the forged EIO cover.
Revolut returned encrypted zip files with folders of ten customers each, ID pictures, verification selfies, account data, unredacted transaction data, with the password sent in a follow-up PEC.
Anyone whose wallet address appears on-chain can be turned into a target this way. Self-custody does not close this door: the moment your KYC data sits with a regulated intermediary, the same channel opens.
