

The Application Security Company
London
Joined April 2015
- Tweets3.5K
- Following135
- Followers1.9K
- Likes473




Honored to be featured in @CloudSecList Issue 320 🙌
Our vulnerable-mcp-servers-lab is a training ground for security professionals to learn pentesting MCP (Model Context Protocol) servers.
MCP is becoming the backbone of AI agent integrations.
Understanding its security gaps today means protecting your AI infrastructure tomorrow.
Try it out 👇
github.com/Appsecco/vulnerab…
#RedTeam #AISecurity #AppSec

ALT Screenshot from The CloudSecList Issue 320 showing Appsecco's vulnerable-mcp-servers-lab featured in the Tools section, highlighted with a blue border. The tool is described as "A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers." Celebratory graphics with party poppers surround the screenshot, with "Got Featured in The CloudSec List 🎉" as the headline and Appsecco logo at the bottom.
We are open sourcing the vulnerable MCP servers we coded for the Pentesting MCP Servers workshop at BSides London.
Last Saturday, I ran a 4-hour hands-on workshop at Security BSides London teaching folks how to pentest MCP servers and AI agents.
To make it practical, I built a collection of intentionally vulnerable MCP servers covering real attack scenarios
- Injection vulnerabilities
- Auth bypass paths
- Misconfigured trust boundaries
- Hidden functionality exposure
- Prompt injection surfaces
The workshop sold out and the feedback was clear - people want reproducible labs they can break, learn from, and practice on.
So we're releasing the entire collection on our Appsecco’s GitHub later this week after some bug fixes.
This is for pentesters who want to understand MCP attack surfaces, product security engineers building with MCP, AI red teamers, and anyone who learns by breaking things in a safe environment.
Real vulnerabilities. Real exploitation. Reproducible locally.
Follow Appsecco to catch the release. We'll share setup guides, attack walkthroughs, and the updated MCP Pentesting Checklist v2.0 alongside it.
My contribution on the journey from Pentester to AI Red Teamer.
#pentesting #aisecurity #mcp #mcpsecurity
CVE-2025-55182 (React RCE) is now fully weaponized.
PoCs are out. Attackers are already scanning.
Here’s a quick demo showing how we detect and exploit the vulnerability using Burp Suite, including Active Scan Plus and a manual multipart payload.
If you’re running React Server Components or Next.js, patch today.
Don’t rely on LLM-generated fixes. Verify them.
#React #NextJS #AppSec #AISecurity

Our Chief Hacker at Kloudle and Appsecco wants to know who in our connections uses #Kubernetes.
Quick poll in the post!

I fondly remember my first #kubernetes cluster pentest several years ago. Gained cluster admin by reading protected credentials using a binary planting/path confusion bug!
Fun times! 😎 🎊
I'm running a poll to know who in my connections is using Kubernetes in prod?
14%Managed services (no K8s)
62%We use K8s
17%K8s urgh
7%K8s in prod in private DC
29 votes • Final resultsContinuing our series of IAM - Misconfigurations checkout the Part -2 By @mishr_a_nurag where he explains - how a misconfigured IAM policy can lead to privilege escalation.
Link: blog.appsecco.com/exploiting…
Read up and share your thoughts.
#aws #cloudsecurity #awssecurity #infosec

Check out Bollina Bhagavan's @XCriminal_ new blog on "Getting shell and data access in AWS App Runner"
Read on and share your thoughts!
Link: blog.appsecco.com/getting-sh…
#aws #cloudsecurity #redteam #infosec #appsecco
Check out Varun Bhat's @evils0cket new blog on "Exploiting IAM security Misconfigurations — Part 1"
Read on and share your thoughts!
Stay tuned for part 2 of the blog.
Link: blog.appsecco.com/exploiting…
#aws #cloudsecurity #redteam #infosec #appsecco #awssecurity #IAM
Check out Bollina Bhagavan's @XCriminal_ new blog on "Finding Treasures in Github and Exploiting AWS for Fun and Profit - Part 2"
Read on and share your thoughts!
Link : blog.appsecco.com/finding-tr…
#aws #cloudsecurity #redteam #infosec #appsecco
Checkout Ratnakar Singh's @em_ratnakar blog on his "Internship Journey at Appsecco".
Link: blog.appsecco.com/my-interns…
#appsecco #internship # infosec #cybersecurity

Appsecco retweeted

Limited seats only! I'll be doing a 2 day in person hands-on cloud security training titled "Breaking and Pwning Apps and Servers on #AWS and #GoogleCloud" @bsidesbangalore on June 6th-7th. Register now!
bsidesbangalore.in/event-det…
cc @appseccouk @Kloudleinc

Checkout Abhishek Birdawade's @abhhi3838 blog on "Gaining Experiences and Building Connections: My Internship Journey at Appsecco".
Link: blog.appsecco.com/gaining-ex…
#appsecco #internship #infosec #cybersecurity

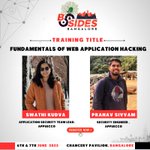
We are offering our most requested training "Fundamentals of Web Application Hacking" by @swatskudva & @zerodaywo1f at @bsidesbangalore
If you're starting off in Appsec as a career option, sign up and learn from our AppSec Experts.
Register: bsidesbangalore.in/registert…
#appsecco

We are offering our most loved training "Breaking and Pwning Apps and Servers on AWS & Google Cloud" by @riyazwalikar & @XCriminal_ at @bsidesbangalore
Hurry-up and register for the conference & training.
Register:
bsidesbangalore.in/registert…
#appsecco #aws #gcp #infosec

Check out Bollina Bhagavan's @XCriminal_ new blog on "Finding Treasures in Github and Exploiting AWS for Fun and Profit"
Read on and share your thoughts!
Stay tuned for Part 2 of the blog.
Link: blog.appsecco.com/finding-tr…
#aws #cloudsecurity #redteam #infosec #appsecco
Discover and learn techniques to hacking apps with nosql backends in our latest post by @srkasthuri
Check out:
appsecco.com/blog/hacking-ap…
#infosec #CybersecurityAwarenessMonth #appsecco #nosqlinjection #Pentesting

Appsecco retweeted

Please follow @InfosecJourneys on LinkedIn and Twitter. It is an one of a kind podcast and a deep dive into the mind of people who are moving mountains in Information Security.
Appsecco retweeted
DeTaTalks with @titanlambda, Security Storyteller EP4!
Welcome @_Shruthi_k, Podcaster at @InfosecJourneys | Customer Success Manager at @appseccouk| Co-founded infosecgirls 🎉
Thank you for interacting with us!
#NullconGoa2022 #infosec #cybersecurity #appsecco
Appsecco retweeted

At @appseccouk, we released our in-person class courseware for free on GitHub.
Will teach you a bunch of techniques
github.com/appsecco/breaking…
cc @riyazwalikar


The next episode in our series of NULLCON diaries is out. If you weren't able to attend Nullcon or could attend only a few, here's your opportunity to find out what you missed.
appsecco.com/blog/nullcon-20…
#appsecco #appseccoatnullcon #infosec #techtalks
