

Building Agents for AI+Security. Building software using https://xitter.cf/t.co/E7fZVhj4qu like https://xitter.cf/t.co/HXSL0xTBWJ https://xitter.cf/t.co/MLS1yxz9Rg https://xitter.cf/t.co/NVEbYPjEGk
Bangalore
Joined December 2006
- Tweets18.9K
- Following3K
- Followers6.5K
- Likes7K




All this shady stuff around banning gold buying is making me think maybe I should stop SIP and buy gold.
🫠

Hey @grok if a government was censoring videos posted by people showing police brutality what can the citizens do to preserve the evidence?
Something that’s based on p2p so that it can’t be easily taken down.
That’s all is being asked for.
Let every single vote count.
If you pretend to treat everyone as an equal go read the struggle to get to this point.
There is no place for stealing votes and elections.

See what an agent running as you can reach.
Free local scan for macOS and Linux.
No account, no network calls, no telemetry.
abr.kloudle.dev

Originally built for the @Algorand Global x402 challenge.
Paste this into your agent
Read abr.kloudle.dev/llms.txt and follow it to check my agent blast radius.
Beads is the fundamental piece that helped me use different family of agents to steer, write specs, code, review, audit, ship.
Beads with dolt is the ultimate multi-agent power up.
Thank you so much for building it and releasing it as an open source software.
👏👏👏

Beads is the oldest and most mature OSS memory system for agents out there. It's the foundation for all my work for the past year, and has matured tremendously with the work of the Gas City folks.
Now that everyone is finally figuring out that they need to "grow" their company brains, I see all these products coming out. You don't need products, you just need Beads. Show it to your agent today.
So amazing to read the variety of answers in this thread.
Bookmarked bunch of tools.
My stack
🏗️ All Agents on dedicated servers
🏗️ Wezterm on laptop, herdr on server
🏗️ Beads for each repo to track work
🏗️ My own harness sfsf for completing multiple beads as goals

The era of checklist based cybersecurity accounting is coming to an end.

The end of software secrecy is almost upon us. The death of closed source, and the final triumph of open source.
I should have realized this a few months ago when I successfully decompiled the game of Firefighter from an ancient DOS shareware binary. My robot friend was able to tell it had been written in Borland Pascal from looking at the data layout; it gave me back very readable Pascal code with sensibly chosen function and variable names. I transpiled it to Rust and now ship it as part of my heritage games collection.
The thing is, I thought of this as a fun stunt but didn't have any confidence that the technique would scale up to large, real programs. I have since learned that people are now doing this sort of thing with entire AAA games, which are among the most complex software artifacts ever to be shipped as a binary. If they can be decompiled, anything can be.
This has implications. Massive implications. We need to think about what the world is like when, in general, there is no longer a secrecy moat around almost any software at all.
1/2
Folks if you want to understand the historical context.
Recommended reading.
Edwin Black’s book
IBM and the Holocaust: The Strategic Alliance Between Nazi Germany and America's Most Powerful Corporation


Wrote about the cybernetic models behind SIR created by TCS and where is this model coming from and how it is linked to One Nation One Election.
newslaundry.com/2026/10/03/b…

It’s been going on since GPT 5.5.
I am glad it’s not just me who experienced it.
So grateful for access to Kimi and GLM.

Friendly reminder about new subtle policy and guardrail changes in GPT-6 and 6.1:
Contrary to how Anthropic does it and slaps your wrist for even asking it, Sol 6 and 6.1 dance around the bushes, A LOT, and loop forever, effectively wasting tokens, instead of refusing taking final actions. It chats and documents "progress" and keeps iterating over results but takes no actual action, being execution of a command, placing an order or any action that crosses the system policy guardrails.
I've been observing this since day one of Sol 6 release, especially in my AI trading harness.
Stick to 5.6 Sol, is my suggestion for now.
YMMV.
Here you go.
Ask your fav ai to make you a nice infographic on what motivated leave voters in brexit.


Imagine making businesses dependent on a handful of US labs for permission to defend themselves.
A bank’s security cannot depend on an attacker getting refused by Claude.
Refusals can add friction. They do not fix a vulnerable system, and attackers are not obliged to use a model that follows those rules.
Hugging Face already experienced the other side of this. During its investigation of the July attack, Claude refused much of the forensic analysis. The team moved that work to GLM-5.2 running on its own infrastructure.
Restrict capable open models and the businesses supposedly being protected could lose precisely that fallback.
Microsoft made a similar argument in 2002: public source access helps attackers, so access should be limited to trusted parties.
The Crypto Wars offer another warning. US export restrictions left weak encryption in software. Years later, FREAK and Logjam exposed this stupidity.
Open models carry risks. So does making defensive capability available only with a vendor’s permission.
Before calling for a ban, think how defenders retain access to the tools they need when the gatekeeper says no.

I've done a complete U-turn on my opinion on open source AI. We should be careful (and probably disallow release) of models on par with current open source Astra/Opus level models.
AI is now reverse engineering games from binaries and remaking them. Reverse engineering games is a very hard problem. If this is possible then reverse engineering banking software, ID systems (Aadhaar), flights, etc is possible too. A game ships its binary to every player. Bank and Aadhaar backends are protected by servers, but it's unlikely the security teams at these are smarter than advanced AI that can do this to games.
We are protected rn because a Claude will refuse to tick "I'm not a robot" on websites. When OSS models don't respect that, we have a looming cybersecurity problem. Apologies I didn't see this earlier.
Dhurandhar 3
NatGeo dekhta hoon, isliye pilot hoon.
Movie loading…
[█████████░] 90%

I just heard a radio report on the Dubai-Tel Aviv flight incident.
Let me get this right:
The copilot stabbed the pilot.
A passenger going to the loo heard the altercation & alerted staff.
The plane went into a steep decline.
While that was happening, the stabbed, blood-soaked & still wrestling captain broke free from the tussle & opened the cockpit door - an awkward keypad operation.
While still in steep decline, passengers & flight crew stormed the cockpit, detaining the copilot, AND A PASSENGER steadied the plane, before, handily, ‘2 other Israeli pilots’ that just happened to be on board, popped up out of nowhere, incredibly avoided being shot out of the sky by a trigger happy Israel below, & flew it to Saudi Arabia where they landed it.
How did the passenger steady the plane? He had watched a TV show ‘Air Crash Investigation’ and “knew exactly what to do”.
Now.
I have SOOOOO many questions!!!
😂😂😂🙄🤷♂️
Anyone with a working crypto wallet who can send $0.20 in USDC on the Algorand Network to a wallet of mine?
Need to test one thing before making my new tool live for the Global x402 Challenge.
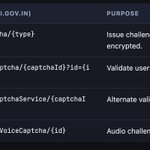
2 weeks ago I posted how multipel Election Commission of India websites have CAPTCHA that is easy to bypass.
xitter.cf/makash/status/20984065…

2/n
Just copy the entire bundle file using copy paste or if you prefer cli curl it.
curl -o voters-eci-main-bundle.js voters.eci.gov.in/static/js/…
Its about 1.6 MB file.
There was no testing of production systems for this analysis.
The security impact assessment is from public bundle analysis.
There are potentially 100s of IP addresses in the ECI Network. They may be hiding similar apps or worse.