




bcoles retweeted

Повну емуляцію апаратної платформи Nokia 6600 (NHL-10) у QEMU завершено. GSM-зв’язок працює end-to-end:
Відправка та прийом СМС
ARM → DSP → IQ → Osmocom → IQ → DSP → ARM
KASLD v0.4.0 released.
Linux #KASLR derandomization tool.
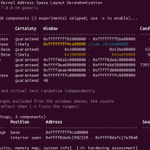
Memory regions now carry a certainty rating: "guaranteed" proven values/ranges, and "likely" narrower guesses that can be wrong (from heuristics/side-channels).
+18 leak components (120 total).
github.com/bcoles/kasld

ALT KASLD recovered the kernel virtual base address on an Ubuntu 26.04 system.

ALT KASLD recovered the kernel virtual base address on a Debian 13 system.

ALT KASLD recovered the kernel virtual base address on a Fedora 44 system.

ALT KASLD recovered the kernel virtual base address on a CachyOS 260426 system.


KASLD v0.3.0 released.
Unprivileged Linux #KASLR derandomization tool that gathers leaks & side-channels and fuses them through a constraint solver into one sound answer for the kernel base — exact where a leak allows, smallest residual window otherwise.
github.com/bcoles/kasld

bcoles retweeted
💥 Introducing "Dirty Frag"
A universal Linux LPE chaining two vulns in xfrm-ESP and RxRPC. A successor class to Dirty Pipe & Copy Fail.
No race, no panic on failure, fully deterministic. ~9 years latent.
Ubuntu / RHEL / Fedora / openSUSE / CentOS / AlmaLinux, and more.
Even if you've applied the "Copy Fail" mitigation, your Linux is still vulnerable to "Dirty Frag". Apply the Dirty Frag mitigation.
Details:
dirtyfrag.io
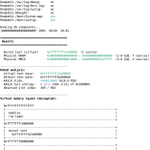
KASLD v0.1.0 released.
New orchestrator runs and cross-correlates leak components to map kernel memory layout. Computes #KASLR slide, entropy bits, and renders virtual/physical memory maps.
Now includes prefetch side-channel.
github.com/bcoles/kasld

New tool: envex — extract and analyze environment variables from running Linux processes. Flags secrets and credentials across all processes using name heuristics, value pattern matching, and entropy analysis. No ptrace or special capabilities required.
github.com/bcoles/envex

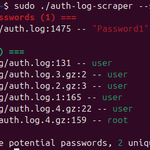
New tool: auth-log-scraper — search Linux auth logs for usernames that look like accidentally typed passwords. 100+ service-specific parsers (SSH, databases, web servers, monitoring, etc.), JSON/CSV output. Vibe coded, so YMMV.
github.com/bcoles/auth-log-s…

bcoles retweeted

Qualys Threat Research Unit (TRU) discovered CrackArmor: 9 AppArmor flaws impacting 12M+ Linux systems since 2017. These enable root access & container breakouts.
Patch your kernels now! Details: bit.ly/4s2c3O4
#Linux #Cybersecurity #CrackArmor"

bcoles retweeted

A Race Within A Race: Exploiting CVE-2025-38617 in Linux Packet Sockets.
A step-by-step guide to exploiting a 20-year-old bug in the Linux kernel to achieve full privilege escalation and container escape, plus a cool bug-hunting heuristic.
open.substack.com/pub/calif/…

bcoles retweeted

🎅mongobleed - poc for CVE-2025-14847. Leaks data from mongodb instances due to flaw in zlib message decompression. Reminiscent of heartbleed ❤️

If you're using #Hexstrike Server, be aware that it binds to all interfaces by default (which allows unauth remote command execution).
github.com/0x4m4/hexstrike-a…

bcoles retweeted

Local Privilege Escalation in Fedora Linux (CVE-2025-12744).
Red Hat has made this public, but patches aren't out yet. Reliable root for any local user.
Mitigation: sudo systemctl disable --now abrtd
Writeup + PoC: initblog.com/2025/abrt-root/
I've released Rootkit Signal Hunter - a simple tool which detect rootkits which use signals to elevate process privileges.
github.com/bcoles/rootkit-si…
bcoles retweeted
Here is our 0day for kernelCTF🩸
- 82k bounty
- quickest submission ever
- all instances pwned😎
syst3mfailure.io/rbtree-fami…
Disclaimer: We apologize for abusing the red black tree family. Turning grandparents against grandchildren is only acceptable in the context of pwn😤


bcoles retweeted

An introduction to Software Defined Radios.
A thread for beginners on:
1. What a SDR is
2. What you can do with SDRs
3. How it plays a role in the security/hacking world
4. How it’s used in ham radio.
5. How to choose/buy one
6. Link to more reading material
0/21

bcoles retweeted
Big new feature in kernel-hardening-checker: now it supports checking the Linux kernel security parameters for RISC-V ⚡️ (in addition to X86_64, ARM64, X86_32, and ARM).
I've spent many weekends on this. Thanks to @_bcoles for the contribution ⭐️
github.com/a13xp0p0v/kernel-…

bcoles retweeted
Too Subtle to Notice: Investigating Executable Stack Issues in Linux Systems
huhong789.github.io/papers/y…

bcoles retweeted
KernelSnitch: Side-Channel Attacks on Kernel Data Structures
Paper by Lukas Maar et al. about using a timing side-channel for leaking addresses of exploitation-relevant kernel structures.
lukasmaar.github.io/papers/n…

