

Security & AI @ Microsoft. Posts are my own
Joined May 2008
- Tweets1.4K
- Following565
- Followers10.3K
- Likes6K






Joe Desimone retweeted

Russian threat actor Midnight Blizzard is conducting widespread traffic manipulation attacks at hotels worldwide. Result: delivering malware or redirecting auth flows at their discretion, globally.
Since early May 2026, we saw this subcluster manipulate DNS and HTTP traffic from networks served by captive portals to redirect user traffic through actor-controlled infrastructure. We’re calling the campaign CaptiveCrunch.
“We have observed notable commonalities in the equipment and management systems used across multiple affected networks.”
We break down the malware & techniques, but the most important part is how dynamic all of it is: Midnight Blizzard is using AI to support a significant portion of these operations. They are moving and changing quickly.
Feedback welcome on the suggested mitigations: microsoft.com/en-us/security…
Help spread the word to VIPs in governments, diplomatic entities, non-governmental organizations (NGOs) in the US and Europe (probably also those traveling to Black Hat)

Joe Desimone retweeted

Our new multi-model agentic security system brings together more than 100 specialized agents across frontier and custom models to find exploitable bugs, delivering top performance on the CyberGym benchmark.
We used it ahead of Patch Tuesday to help find and fix 16 vulnerabilities. Today we’re announcing that customers can sign up to test it in private preview.
microsoft.com/en-us/security…

Joe Desimone retweeted

OpenAI’s GPT-5.5 is the second model to complete one of our multi-step cyber-attack simulations end-to-end 🧵

Joe Desimone retweeted

Howdy folks! Taking a break from my twitter break to let yall know that we released a new @GreyNoiseIO product yesterday. It's called Project Swarm. We've been quietly not-so-quietly working on it for a few years. You can buy it now. It costs $1.
There are lots of vulnerabilities on edge-facing apps. To catch in-the-wild exploitation of them, we @ GreyNoise run sensors on the internet. New AI models means more vulnerabilities being identified and exploited, and FASTER. Long term, software and hardware will probably get better, but in the meantime we're gonna have to deal with A LOT of vulnerabilities.
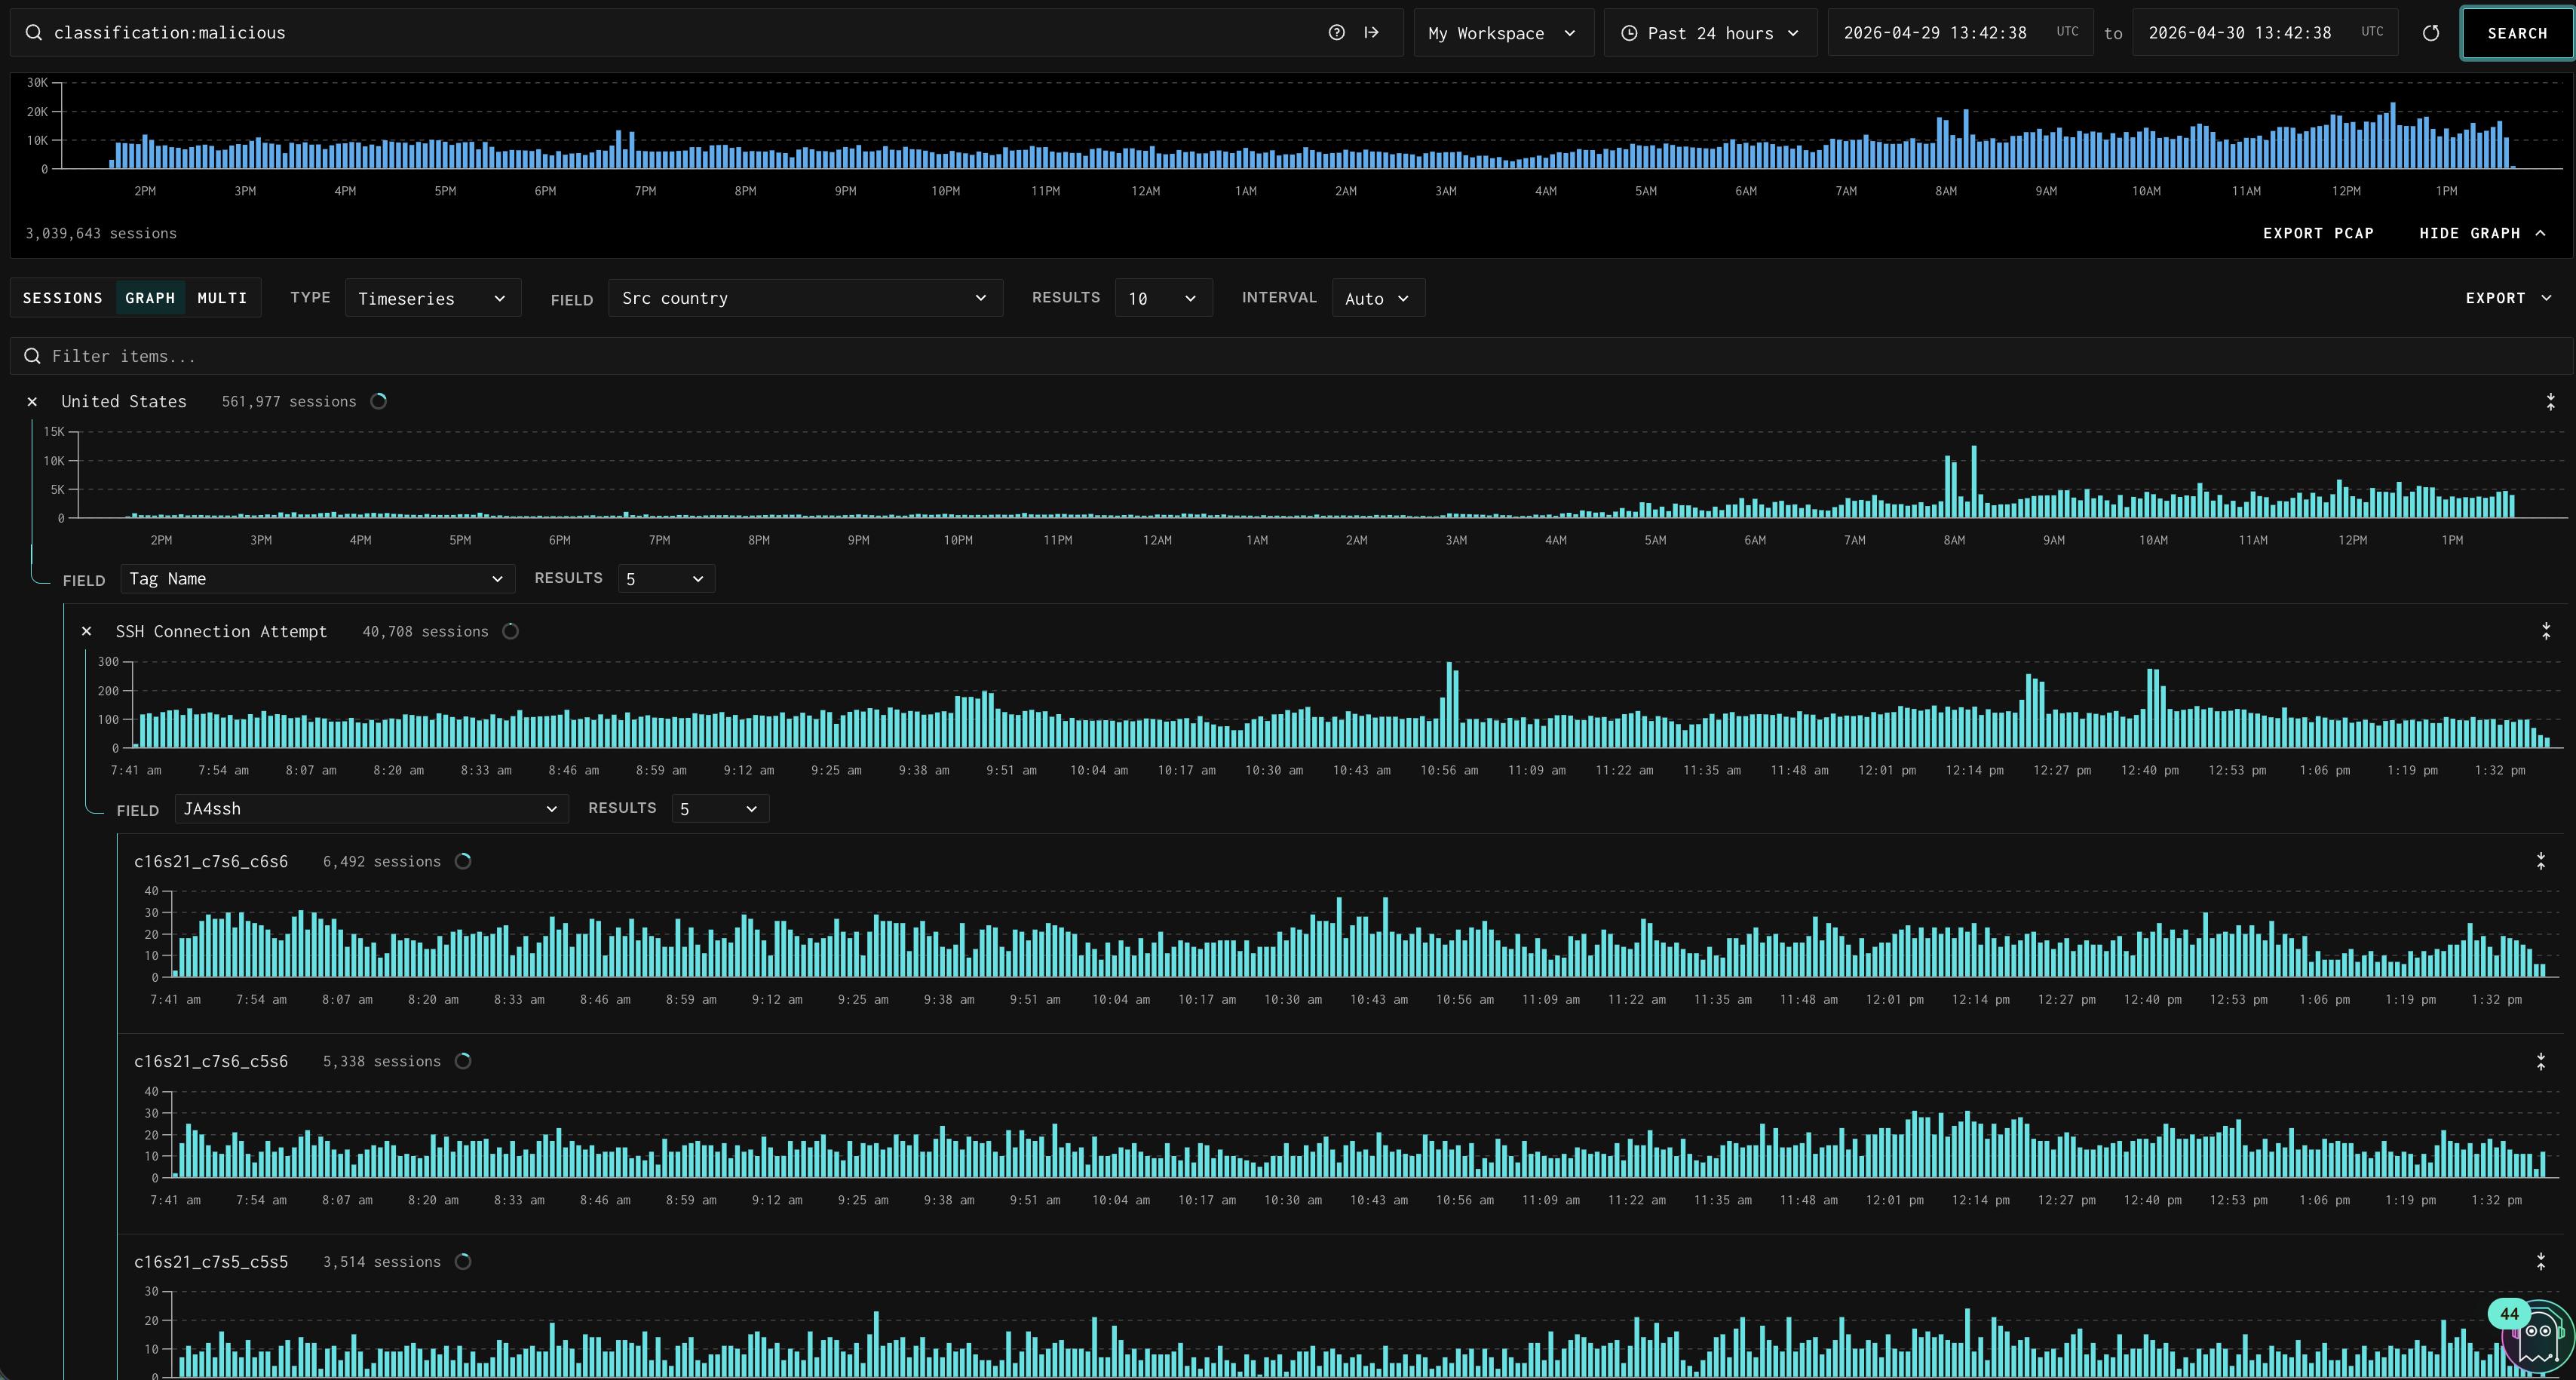
At GreyNoise, the sensors we run are basically honeypots- we bait attackers to scan and exploit them which enables us to learn where the attackers are, which vulnerabilities they are exploiting, what it drops, and what it looks like on the wire. From ~2020-now it took us years to build up our fleet. Now anyone can use our new product to deploy their own sensors on their own networks, or an entire fleet of any size, in a day. You can rip back the data and do whatever you want with it. You can resell it, put it into your product, or just stare at it- whatever you want! On our side, we aggregate the data and pour it into a community dataset that everyone shares. As more people join, the data gets bigger and better.
Couple neat features:
- Sensor deployment is a single bash command on any modern linux distro that supports iptables and wireguard.
- Sensors and vulnerable software (profiles) are abstracted into different logical concepts, which means the "what" and "where" are different things, and the sensor is not constrained by the compute required to run the vulnerable software. Also, no matter how hacked the profile (honeypot) gets, it can't touch your host sensor or the rest of your network.
- Sensors can run fake honeypots, real software, or even real hardware (bridged with a raspberry pi) like old crappy routers and modems (or expensive firewalls and VPN gateways 👀)
- You can create dynamic blocklists that block IPs sourced from your own sensors in real time, so if a remote IP address *looks at your network* the wrong way, you block them instantly.
- All the PCAP data is available to you in a gorgeous and intuitive interface at near real time and fully enriched against all of our (thousands of) rules. We're working on the host metadata (malware, syscalls, host behaviors) as well, but this will come later.
- If we don't tag a CVE that's interesting to you, you can write a Suricata rule to tag it yourself once and your data gets tagged with it in real time forever.
- You can instantly download PCAPs of any exploits that hit your sensors.
- If you don't want your data shared with the community dataset, you can talk to our team and we'll work out rights to make it private.
Check it out! There's a lot of moving pieces to make this work and we expect bugs, but it's available right now. Join the fight!
greynoise.io/project-swarm



Joe Desimone retweeted

Patch your Linux boxes!
Copy.Fail is a trivially exploitable logic bug in Linux, reachable on all major distros released in the last 9 years. A small, portable python script gets root on all platforms.
Found by the teams at @theori_io and @xint_official
More details below
xint.io/blog/copy-fail-linux…

New adventure: wrapped week one at Microsoft Security! Working alongside @dwizzzleMSFT, who I plan to annoy with a backlog of questions. Excited to work on AI and security at planet scale 🤓


Engineers at Microsoft have been busy. Today they patched 5 LPE vulns I submitted to their bounty program. All found with AI (not Mythos 😛)
Cloud Files Mini Filter Driver - msrc.microsoft.com/update-gu…
Common Log File System Driver - msrc.microsoft.com/update-gu…
Desktop Window Manager - msrc.microsoft.com/update-gu…
Desktop Window Manager - msrc.microsoft.com/update-gu…
Desktop Window Manager - msrc.microsoft.com/update-gu…
After 10 years at Elastic/Endgame, today is my last day.
Incredibly proud of what this small but mighty team has built. Working alongside our community of users has been one of the most rewarding parts of the journey.
On to a very exciting new adventure soon, stayed tuned!
We open sourced the tool used to detect the Axios supply chain compromise! I built it Friday after a red eye home from RSAC. Also, wrote up the full story, including the hectic moments after that first critical alert
github.com/elastic/supply-ch…

Story, and thoughts on the software ecosystem elastic.co/security-labs/how…

We published a pair of articles on the axios compromise and deep dive on the malware, alongside detection strategies
elastic.co/security-labs/axi…


Cobbled together a supply chain monitoring system last week: Cursor+Composer-2-fast harness on live package diffs (pypi+npm). Simple! Received a slack alert within minutes of Axios compromise. Reported to the devs after triple checking, because at first I could not believe it!


Now let's talk attribution. @DefSecSentinel quickly pointed to DPRK 🇰🇵. Remarkable similarities to WAVESHAPER / UNC1069

Analysis of the macho malware used in the Axios supply chain compromise
gist.github.com/joe-desimone…

Analysis of the macho malware used in the Axios supply chain compromise
gist.github.com/joe-desimone…
We are working it, sharing what we know as of now - gist.github.com/joe-desimone…

We are working it, sharing what we know as of now - gist.github.com/joe-desimone…

@npmjs @GHSecurityLab there is an active supply chain attack on [email protected] which pulls in a malicious package published today - [email protected] - someone took over a maintainer account for Axios
Joe Desimone retweeted

@npmjs @GHSecurityLab there is an active supply chain attack on [email protected] which pulls in a malicious package published today - [email protected] - someone took over a maintainer account for Axios