
freeman retweeted
KERNSEAL makes the linear page cache overflow in cyberstan.co.uk/fuse-readdir… deterministically unexploitable. Serial log below 👇

freeman retweeted
Attacks always get better. Here's a new nginx RCE that bypasses ASLR, tested on the latest nginx 1.30 and 1.31.
This still requires a non-default config, but unlike some previous bugs, it does not depend on any additional vulnerabilities or external helpers to get to RCE.
We reported the bug on May 15. F5 has confirmed it, and hopefully a patch will land soon.
This is getting ridiculous 😅. We have enough nginx bugs to do an entire week of MAD Bugs on it. Who could have thought nginx is starting to feel like the new Linux kernel?
This is the funniest time in computer hacking. And yet the world is completely unprepared for this new reality.
freeman retweeted

‼️🚨 Pwn2Own Berlin 2026 just hit a wall. For the first time in 19-years, ZDI rejected dozens of working zero-day RCE submissions because organizers ran out of contest slots.
Rejected hackers are now going public with PoC demos and direct vendor disclosures, breaking Pwn2Own's usual secrecy.
▪️ AI surfaces a massive wave of 0-day RCEs.
▪️ Submissions overwhelm ZDI past max capacity.
▪️ Slots run out. Researchers with working chains get rejected.
▪️ "Revenge disclosures" begin. ← we are here.
Confirmed casualties so far:
▪️ @xchglabs : 86 vulnerabilities prepared (PyTorch, NVIDIA, Linux KVM, Oracle, Docker, Ollama, Chroma, LiteLLM, llama.cpp). All rejected. Now reporting directly to vendors with writeups dropping as patches land.
▪️ @ggwhyp : full-chain Firefox RCE on Windows. Rejected. Publicly demoed (HTML page → cmd.exe → calc.exe). Responsibly disclosed to Mozilla.
▪️ @yunsu_dev : working RCE chain, rejected. Submitting elsewhere.
▪️ @ryotkak : tried to register for 3+ weeks. ZDI confirmed "at maximum capacity, can't add extra contest days." Considered canceling flight and hotel.
▪️ @anzuukino2802 : Claude Code RCE PoC. Rejected.
▪️ @desckimh : 0-day RCEs in Ollama and LM Studio. Rejected.
Reported impact: a community-estimated 150+ researchers tried to register. Accepted contestants are now being warned about collisions. Rejected vulnerabilities going to bug bounty programs may trigger pre-event patches that invalidate the work of those who got in.
ZDI has not publicly addressed the capacity issue. The event still runs May 14-16 in Berlin.


freeman retweeted
Linux Kernel Hardening: Ten Years Deep
Talk by @kees_cook about the relevance of various Linux kernel vulnerability classes and the mitigations that address them.
Video: youtube.com/watch?v=c_NxzSRG…
Slides: static.sched.com/hosted_file…



freeman retweeted

This year, our team did a lot of important industry REsearch work. But this BMC research shows literally how poor product security practices are in critical data center infrastructure components. The bugs we found should not exist in 2023 in any environment.


🚨New REsearch: "Old But Gold: The Underestimated Potency of Decades-Old Attacks on BMC Security"
⛓️Our team demonstrates critical security risks affecting the BMC FW supply chain ecosystem that could lead to full remote control of the server system.
binarly.io/posts/Old_But_Gol…

freeman retweeted
An RFC patch series by @tehjh and @_MatteoRizzo for mitigating cross-cache use-after-free attacks.
The performance impact is still questionable, but functionality-wise, this would be an exciting change if merged 😃
lore.kernel.org/all/20230915…

freeman retweeted
Here is the writeup for CVE-2023-3389, a Use-After-Free on an hrtimer in io_uring, which I exploited for the kCTF VRP
qyn.app/posts/CVE-2023-3389/
freeman retweeted

Yay! My writeup on finding (half) Spectre-v1 gadgets in the Linux kernel using #CodeQL is finally live 😁😁
github.com/google/security-r…
freeman retweeted

RISC-V (@risc_v) Control Flow Integrity (CFI) is coming and I'm proud to be one of the contributors to this important security extension. Full spec is available here:
github.com/riscv/riscv-cfi/b…

freeman retweeted

[Zer0con2023]
Jun Luo(De4dcr0w) & Yanfeng Wang giving their talk on Busy2Nice : A New Way to Win the Race for Tiny Windows in the Linux
#Zer0con2023


freeman retweeted
If anyone who's around in Paris for @hexacon_fr wants to acquire a USB-Cereal adapter — hit me up.
This adapter is a convenient replacement for the Android Debug Cable. Essentially splits the USB port into two: one with UART with kernel logs, the other is a pass-through for ADB.

freeman retweeted

A technical analysis of Pegasus for Android – Part 1 cybergeeks.tech/a-technical-…
freeman retweeted

Linux: munmap() race with pagemap_read() leads to page UAF bugs.chromium.org/p/project-…


freeman retweeted

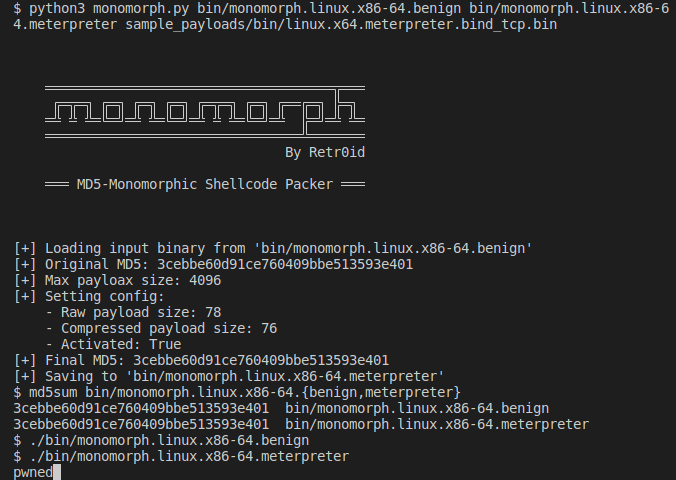
Pack arbitrary shellcode into an executable that always has the same MD5 hash:
github.com/DavidBuchanan314/…
freeman retweeted

Wrote another @solana pwnable for @paradigm_ctf -- this time based off of a real bug ;)
ctf.paradigm.xyz/challenges/…

freeman retweeted

iOS and MacOS recently started parsing media codec parameter sets in the kernel, leading to bugs like this bugs.chromium.org/p/project-… – at Mountain View, CA