

The most secure way to buy, swap, and manage crypto - for you and your business. https://xitter.cf/t.co/zfK3gn7zeI
Your pocket
Joined August 2018
- Tweets13.3K
- Following498
- Followers41.1K
- Likes33.6K



Pinned Tweet
🔮Prediction markets are live on @ZenGo - powered by @Polymarket.
🏆Predict the 2026 World Football Tournament straight from your phone. ⚽48 nations. 104 matches.
Back your team. Make your call.
#PredictionMarkets #WorldCup #CryptoWallet
→ zengo.com/prediction-markets…
Day 1 on Arc.
USDC pays its own gas. No spare token just to move dollars.
What are you sending first?
xitter.cf/ZenGo/status/211040028…

Zengo now supports Arc.
On Arc, USDC pays its own network fees. Buy, swap, send and receive USDC without holding any other token just to cover gas.
Welcome, @arc

Zengo now supports Arc.
On Arc, USDC pays its own network fees. Buy, swap, send and receive USDC without holding any other token just to cover gas.
Welcome, @arc
Verification only helps if you trust what's doing the verifying. Zengo took another route: no seed phrase, no hardware in the mail. Two key shares, neither signs alone.
xitter.cf/peterktodd/status/2108…

Solid digging. Whatever the root cause turns out to be, the question is the same: who can sign? Zengo has no seed phrase to pre-generate, copy, or phish. Two key shares, neither signs alone.
xitter.cf/exsiway_/status/210863…

so about the $86m ledger drain. everyone’s screaming “ledger got hacked” again. i spent the evening digging and it’s dumber and scarier than that
there’s a shop in malaysia called cryptobilis that sells hardware wallets. ledger has it listed as an official authorized reseller since at least 2022, for malaysia, indonesia and the philippines. legit shop, real devices, years of normal customers
this spring the founders sell it. the deal comes with an NDA: they can’t tell anyone about the sale until october 19
by august the company registry shows one owner with 100%. some guy from heilongjiang, china
the shop keeps running like nothing happened. the site, the name and the “authorized by ledger” badge all stay up
then on oct 8 @MagicalTux posts photos of a ledger he cracked open. hidden under the screen there’s an extra little board with an LTE modem and an eSIM. it just watches the display. you set up your wallet, your 24 words show up, and they get sent out over mobile data. ledger’s genuine check doesn’t catch it because the actual ledger chip is real. his device came from malaysia
xitter.cf/MagicalTux/status/2108…
that post does 120k views
22 hours later someone sweeps everything. 203 BTC hits two addresses in literally one block. ~$58m USDT moves on tron in the same hour. i added up all the wallets: ~$91m
about 7 hours after that ledger says “we’re investigating” and asks cryptobilis to pause sales
cryptobilis is still on ledger’s site as an authorized reseller
to be fair, nobody has officially tied the new owner to the bugged devices yet, and ledger hasn’t confirmed how it happened. but read it as a business plan:
get authorized, sell real stuff for years, quietly sell the company under an NDA, keep the badge, ship devices that phone home, then drain everything the second someone notices
and was ledger even told the shop got sold? nobody’s said so
“authorized reseller” means ledger trusted whoever ran the shop back in 2022. says nothing about who runs it today
bought your hardware wallet anywhere but the manufacturer? open it up today, ledger literally has a guide for that. then move to a fresh seed on a device bought direct
wonder who’s going to answer for this: the chinese frontman from heilongjiang, the shop’s previous owners, or ledger itself
@Ledger clearly needs to keep a much closer eye on who they call official resellers, and take way more responsibility for who sells their devices and how

Your security shouldn't depend on who sold you the box.
Zengo: no seed phrase, nothing to ship. Two key shares, neither signs alone. 🧘
Box or math, which do you trust?
Seedless is having a moment 👀
Zengo was built without one from day one. Two key shares, plus a Recovery Kit (your email and a Recovery File in your cloud).
What made you ditch the seed?

Builders on Robinhood Chain: Stock Tokens + crypto in a wallet that’s never been hacked. Keyless MPC. Self-custodial.
@RobinhoodCrypto
xitter.cf/RobinhoodCrypto/status…
Robinhood Chain is now supported in Zengo 🪶
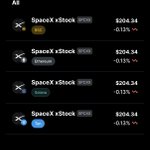
Stock Tokens and crypto on Robinhood Chain, side by side in one self-custodial wallet.
Welcome, @RobinhoodCrypto

Robinhood Chain is now supported in Zengo 🪶
Stock Tokens and crypto on Robinhood Chain, side by side in one self-custodial wallet.
Welcome, @RobinhoodCrypto
Scammers didn't fake a site.
They faked a whole L2.
Reserved chain ID. Working bridge. Looked live.
About $2M in ETH walked across before anyone noticed the mainnet… wasn't.
If a network just "appeared," pause.
Check the official source. Read the sign request.
On Zengo, you start every move, and ClearSign shows you what you're approving.
Predict the World. Earn USDC. 🔮
Sports, crypto, politics, culture: make your call in Zengo.
zengo.com/prediction-markets…
How it actually works.
~$351M moved out while "private keys weren't compromised."
Nobody needed the keys. Forged requests got routine, automated approvals.
On Zengo, you start every move. Two key shares, and neither can sign alone.
Self-custody is who can sign.
Exchange: “Private keys weren’t compromised.”
Also the exchange: ~$351M moved out.
Both can be true when hot/warm ops get spoofed.
Self-custody isn’t a vibes thing — it’s who can sign.
Zengo: keyless MPC. You start every move.
Guessing a 24-word seed is basically impossible.
Phishing one is not.
That’s the whole scam industry.
Zengo never creates a seed for you to type into a fake “security check.” Keyless MPC. Personal Share + Remote Share. You initiate. We can’t move funds alone.
Self-custody without the phrase.
#CryptoSecurity


🚨 Warning: Coldcard users were affected by a severe security breach allowing hackers to find their private keys remotely and drain their accounts.
Zengo crypto wallet is not affected in any way. We use MPC cryptography so no private keys are ever created or stored at any moment.
If you are an affected user, please move your funds to brand new wallet and do not use the private key you had before.
You can safely deposit them in Zengo ("receive") and start fresh and secure.
🛡️More on Zengo.com/security


I just got robbed.
$1.6 million dollars in Bitcoin was drained from my account on July 29th in the @COLDCARDwallet hack.
How's your day going?