

Your digital life is being decided for you. Techlore helps you take it back—privacy, security, and digital rights, made simple by Henry Fisher.
Joined May 2019
- Tweets2K
- Following110
- Followers28.3K
- Likes3.5K





Techlore retweeted

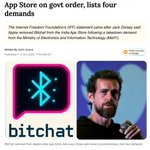
Statement : The removal of BitChat from the India App Store is unconstitutional. Section 69A permits the blocking of unlawful information, not of a messenger for working during internet shutdowns.
New Delhi, 3 October 2026
An Apple App Review notice published today by Jack Dorsey on X records that BitChat has been removed from the India App Store "per demand from the Ministry of Electronics and Information Technology", issued under Section 69A of the Information Technology Act, 2000, on the ground that the application "includes content that is illegal in India". The notice adds that BitChat's TestFlight builds are no longer available for testing in India. It does not identify the content said to be illegal or the ground under Section 69A invoked. The blocking order has not been published. The Internet Freedom Foundation condemns the order and calls for its immediate publication and withdrawal.
BitChat relays end-to-end encrypted messages between nearby phones over Bluetooth mesh. It has no servers and hosts no content of its own. What travels through it is the private speech of its users, so the claim that the application "includes" illegal content is incoherent. The State's actual objection stands recorded in the notices the Indian Cyber Crime Coordination Centre issued on 23 July 2026 to GitHub, Google and Apple against BitChat, Briar and Bridgefy which stated that such applications work even during internet shutdowns and hamper lawful interception, attribution and traceability. Those notices, issued under Section 79(3)(b) were reportedly withdrawn after public disclosure. The same end has now been pursued through Section 69A. The objection is to capability of an application, not to content it transmits. A citizen's ability to speak to another citizen while the State has switched the internet off is not a ground of restriction under Section 69A or Article 19(2) of the Constitution.
Section 69A survived constitutional scrutiny in Shreya Singhal v. Union of India (2015) because of its safeguards which included the need for a reasoned, recorded order, committee review, and a hearing to the originator under Rule 8 of the Blocking Rules, 2009, which the Delhi High Court enforced in Tanul Thakur v. Union of India (2022). Further, Anuradha Bhasin v. Union of India (2020) requires that orders restricting fundamental rights be published and adopt the least restrictive measure. However, it appears in this instance, each safeguard has been evaded. A secret order blocking an entire application, rather than any identified unlawful information, is the most restrictive and disproprotionate measure available. Further, the confidentiality claimed under Rule 16 cannot defeat the right to challenge an order, and the constitutionality of this blocking regime is itself pending consideration before the Supreme Court.
While removal from the App Store does not delete BitChat from phones, it stops new downloads and security updates, leaving existing users on unpatched versions, and it ends security testing in India through TestFlight. During the Jantar Mantar protests, when mobile internet was suspended and jammers were deployed, Bluetooth mesh messaging was a channel of last resort through which young people coordinated their safety. To our knowledge, Apple has removed BitChat on a government's demand in only one other country. This is in China, in April this year.
Our demands
1. MeitY must publish the blocking order, the ground invoked and the record of the committee's proceedings, and serve the developers with a copy and an opportunity of hearing.
2. The direction must be withdrawn. Any specific unlawful use must be met with targeted proceedings under due process, not the removal of a communications tool for everyone.
3. Apple must disclose the demand in its transparency reporting and notify its users in India, and must state whether parallel directions have been received in respect of other app stores.
4. The secrecy of the blocking regime must end. The Blocking Rules, 2009 should be amended to require publication of orders and notice to originators, without awaiting the outcome of the pending constitutional challenge.
The Internet Freedom Foundation will file applications under the Right to Information Act seeking a copy of the order, and stands ready to assist the developers and affected users in India.
Techlore retweeted

Firewalls Don't Stop Dragons has now published 500 podcast episodes, 5 editions of the book, and 300+ blog posts.
A HUGE thank-you to my listeners, readers, fellow evangelists, and patrons for making all of this possible!
Celebrate with me! fdsd500.com


Techlore retweeted

We run a Tor relay. Not as marketing, as rent.
A privacy company that uses Tor and contributes no bandwidth back is freeloading on volunteers. The relay is our share.
Fingerprint and live stats are public, so you can verify it rather than take our word.
pikasim.com/tor-relay

Techlore retweeted

The iCloud Private Relay bug that leaks the IP isn't mentioned, although it had been fixed.


Techlore retweeted

A year ago, we soft-launched Tor VPN Beta as a way to extend Tor's privacy protections beyond the browser to an entire Android device. Since then, we've been able to learn from how people are actually using it in real-world scenarios. Learn more about what makes our per-app circuit isolation different from commercial VPNs, the surprising UX lesson when trying to bypass blocks, and the mobile foundation we're building for what's next. blog.torproject.org/tor-vpn-…

Techlore retweeted

Issue 99 of PrivacyTests.org is out today!

Techlore retweeted

.
The ID Check Company That Leaked 153 Million Licenses
youtu.be/vYgLzpz9Knw via @TechloreInc

Techlore retweeted

OMG we got a shoutout from the venerable @TechloreInc 🤩
Go check out this episode of Surveillance Report! youtube.com/watch?v=aBcubRmx…

Techlore retweeted

Our lead engineer spoke to @TechloreInc about Strongbox & it's future - check it out below 👇🏻
youtube.com/watch?si=c88FSPh…


Techlore retweeted
Thanks for building out a cellular category and listing PikaSim!
For privacy folks finding us here: beyond data eSIMs, we also offer mobile plans with a real number and anonymous SMS verification.
Good company to be in, alongside @CapeCellular, @phreeli and @silentlink1.

The SPA Tools, simple recommendations for privacy & security services also got a brand new cellular category 📱
A warm welcome to these service for the work they're doing! @CapeCellular @phreeli @silentlink1 @PikaSim_esim

ALT Grid of rounded cards titled "Cellular Providers" listing privacy-focused carriers — Cape, Phreeli, PikaSim, Silent Link — each tagged "Intermediate" and "Paid" with short notes about anonymous SIM/eSIM and network privacy features.

Techlore retweeted

Thank you for including us in your VPN tier list video @TechloreInc!
Techlore retweeted
"I think Obscura in 2026... is doing the most interesting stuff in the VPN space."
What an honor coming from @TechloreInc! 🤩

Techlore retweeted

Excellent video by @TechloreInc on VPNs, he has covered all the main points and explained with clarity
if you would like a detailed comparison, techlore has also made a comprehensive comparison sheet for VPNs at vpn.techlore.tech
youtu.be/i_B3BuRb3eQ?si=XAdD… via @YouTube

Techlore retweeted

Which VPN Should You Actually Use? (2026 Tier List)
via @TechloreInc
youtube.com/watch?v=i_B3BuRb…

Techlore retweeted
Introducing Loupe, our latest privacy app for iOS. Discover what apps can learn about you just by reading data your iPhone already exposes, such as your languages, installed apps, device sensors, and much much more
Loupe is free, private, and open source. Give it a try 👇

Techlore retweeted

CopyFail Explained: The Largest Linux Exploit in Years youtu.be/YUZ7RQzfKzo?si=gR96… via @YouTube @TechloreInc

Techlore retweeted

It’s absurd that American authorities can purchase personal data – that they’re not allowed to gather themselves without a warrant – directly from data brokers. This violates the Fourth Amendment, and it’s time to close the data broker loophole.
Today, @RepThomasMassie, @RepBoebert and @naomibrockwell at the @LudlowInstitute introduced the Surveillance Accountability Act. It requires warrants based on probable cause for all government surveillance and data access. You can read more about it at surveillanceaccountability.c…