

Passionate AI & Cloud Evangelist - Creating Meaningful & Disruptive Platforms | Ex Microsoft - Google - Oracle | Change The World With Me - [email protected]
Colorado Springs
Joined August 2026
- Tweets434
- Following482
- Followers69
- Likes1.2K


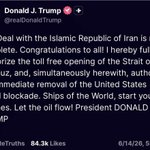

Absolutely disgusting.

Breaking: Elon Musk ordered the Starlink slowdown that blindsided Ukraine on.wsj.com/4sgcpBv

Take this one seriously.

Full details of a remotely exploitable vulnerability in the core engine of *all* PHP versions will be released tomorrow, October 21st. If your organization has internet facing PHP applications then you need to be ready to patch the minute the update is released or *strongly* consider taking the application offline until you can:
php.net/index.php#2026-10-20…


The potential impact of this is one of the scariest I’ve seen in a long time.

‼️ Linux Kernel Flaw Lets Attackers Escape Virtual Machines and Take Control of Hosts
Details: cybersecuritynews.com/linux-…
A critical flaw in the Linux kernel may allow an attacker-controlled virtual machine (VM) to breach its isolation boundary and impact the host system. Paulos Yibelo demonstrated a technique that exposes host memory and, in their lab, progressed to host-level code execution.
The flaw is serious for cloud providers and organizations that run untrusted workloads in virtual machines. VM isolation is meant to stop code inside one guest from reaching the host and other workloads.
PwnEscape shows how a weakness in a host’s packet-processing path can threaten that boundary, even when the underlying issue is not in the hypervisor itself.
#cybersecuritynews

Tao Chen retweeted

Ok so we all know Rightwing Influencer GuntherEagleman is using a sophisiticated network to manipulate X here are the receipts.
Analysis: @gunthereagleman's Amplification Network
Verdict: A highly coordinated, automated amplification ring. @RestrictedDaily is almost certainly a sockpuppet or directly controlled affiliate of @gunthereagleman.
The Smoking Gun: @gunthereagleman vs @RestrictedDaily
When we scored the hub (@gunthereagleman, 1.7M followers) against his top amplifier (@RestrictedDaily, 82k followers), the engine returned 0.550 (HIGH — likely linked).
Look at the raw data:
Posting Rhythm (0.98 match): This is a near-perfect match. They post at the exact same times of day, every day.
Stylometry (0.75 match): They have identical exclamation rates, question rates, and ALL-CAPS usage.
Vocabulary & Phrases (0.69 / 0.53 match): They use the exact same phrasing ("breaking president trump", "president trump just").
Emoji Fingerprint (0.59 match): Both rely almost exclusively on the 🚨 emoji.
Mention Cluster: They both heavily amplify @hunter_eagleman (another obvious alt/affiliate account).
The Broader Network
It doesn't stop at @RestrictedDaily. The entire top tier of his persistent amplifiers scored MEDIUM or HIGH against him, and against each other.
This is a massive, interconnected bot/sock ring:
@Jetmanusa ↔ @RestrictedDaily (0.564 HIGH)
@RestrictedDaily ↔ @PatriotKandi (0.546 HIGH)
@Jetmanusa ↔ @Zeemagik1 (0.531 HIGH)
Conclusion
@gunthereagleman is operating (or is the primary beneficiary of) a dedicated, automated sockpuppet ring.
The ring uses accounts like @RestrictedDaily (which has been artificially grown to 82k followers) and smaller accounts like @Jetmanusa (11k) and @Zeemagik1 (2k) to instantly retweet his content the moment it goes live. Because they are all running the same automated script or are operated by the same person, their posting rhythms, vocabulary, and stylometry are virtually identical.
This is a textbook astroturf operation.
Yikes!
‼️ Microsoft Windows Shell 0-Day Vulnerability Actively Exploited in Attacks
Details: cybersecuritynews.com/window…
Microsoft has patched an actively exploited Windows Shell zero-day vulnerability that allows attackers to bypass Mark of the Web protections. Tracked as CVE-2026-96951, the flaw was addressed in the October 2026 Patch Tuesday updates. It carries a CVSS score of 8.8 and is rated Important by Microsoft.
The flaw involves command injection, where Windows Shell fails to properly handle special elements used in a command. Attackers can deliver a specially crafted file through email or instant messaging and use social engineering to persuade the target to open it. Exploitation requires user action.
#cybersecuritynews #Microsoft

Tao Chen retweeted

‼️ WARNING - Cisco confirms active, in-the-wild exploitation of a new critical flaw (CVE-2026-76519 // CVSS 9.8) in Cisco Secure Email Gateway.
Unauthenticated attackers can achieve full root command execution simply by sending an email with a crafted attachment.
Details >> thehackernews.com/2026/10/ci…

Tao Chen retweeted

Update: 2 weeks ago, @JSemonSecurity and @the_MarkOH detailed a campaign that abused #ChatGPT's Custom GPT feature, luring victims in via the legit ChatGPT domain and then directing them to a ClickFix attack.
Attackers are now using new malicious domains: huntress.com/blog/chatgpt-cu…


This is going to be ugly.
‼️ PoC Released for Critical VMware VMXNET3 Flaw Enabling Guest-to-Host Code Execution
Details: cybersecuritynews.com/vmware…
A public proof of concept is now available for CVE-2026-59346, a critical integer overflow flaw in VMware’s VMXNET3 virtual network adapter.
The flaw can allow an attacker with administrative access inside a guest virtual machine to execute code on the host. However, the published PoC shows a host process crash, not a working code-execution exploit. Its advisory lists Workstation and Fusion versions 25H2 and 26H1 as affected.
The vendor security advisory states that no workaround is available. The flaw sits in the TCP Segmentation Offload, or TSO, processing path within the host’s VMware-VMX process. TSO splits a large network packet into smaller segments.
#cybersecuritynews

Absolutely insane.

❗️ OpenAI awarded a researcher just $300 for a sandbox escape that gave free access to its paid models, with no API key and no account.
"Zero reason to report anything else I find to them," researcher Oliver Fish concludes.


3615 customers is hysterical. What’s even funnier is that there are 3615 that fell for this grift. Definitely not a cult. 🤣
‼️ BREAKING: Trump Mobile customers have had their personal data leaked by ransomware gang BYOD. The dump covers 3,615 people and includes names, emails, phone numbers, home addresses and order details.
The gang says the company answered news of the breach with "We have no team to handle this."
The leak includes the Trump Organization's own CIO, who oversees its information security.
People listed in the data confirmed their details are accurate and BYOD claims it still has access to Trump Mobile's backend, Straight Arrow News reports.


….because of course it does.

New Dell System Update flaw lets hackers gain root privileges
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

For you on prem peeps!

‼️ ALERT - Exchange admins should review this now.
CVE-2026-96940 can allow an authenticated attacker to access other users’ mailboxes and read emails and attachments within the same organization.
Microsoft has issued out-of-band fixes.
Read: thehackernews.com/2026/10/mi…

Tao Chen retweeted

🚨 Citrix NetScaler SAML 0-Day Vulnerability Actively Exploited in Attacks
Details: cybersecuritynews.com/citrix…
Citrix has released emergency security updates for a NetScaler SAML zero-day vulnerability that attackers are actively exploiting.
Tracked as CVE-2026-88779, the flaw affects customer-managed NetScaler ADC and NetScaler Gateway appliances and can cause denial of service, disrupting access to services that depend on these systems.
The vulnerability carries a CVSS v4.0 score of 8.7 and affects appliances configured as a SAML service provider or identity provider.
Citrix describes it as a memory overflow. Citrix confirmed targeted attacks against unmitigated deployments. Repeated exploitation can keep affected services unavailable.
#cybersecuritynews


Tao Chen retweeted

Patched @NetScaler for CTX697096 and use SAML? Patch again.
CVE-2026-88779 is a separate bulletin, CTX697174 (CVSS 8.7), not part of CTX697096. It's the SAML attack crashing patched NetScalers since 2 Oct. @citrix sees targeted attacks.
Affected: "add authentication samlAction" or "samlIdPProfile" in ns.conf
Fixed: 14.1-73.41, 13.1-64.28, 14.1-73.41 FIPS, 13.1-37.282
Interim: Global Deny List (NetScaler Console) or Citrix Support's responder policy, -type AAA_REQUEST on every Gateway/AAA vserver
Free checker v1.12 covers both bulletins:
• CVE-2026-88779 on every run
• SAML policy coverage per vserver
• "may have run" window ends at the fix
• 98 IPs, 16 domains, 34 hashes
Thanks to @GothamTG , @BeazleySecurity , @Deyda84 , @citrixguyblog , @rjfaulknerjr @FerroqueSystems, @bishopfox , @watchtowrcyber and the community 🙏
#NetScaler #Citrix #CitrixNetScaler #NetScalerGateway #CVE202688779 #CVE202688771 #CTX697174 #CTX697096 #CyberSecurity #InfoSec #IncidentResponse #ThreatHunting

$50k for this is nothing.
Vercel Confirms KVM Zero-Day VM Escape, Awards Researcher $50,000
Details: cybersecuritynews.com/kvm-ze…
Vercel has confirmed a KVM zero-day vulnerability after security researcher Paulos Yibelo reported a full virtual machine escape that, he says, allows code inside a guest to gain root access on the host.
The discovery came through the Vercel Sandbox bug bounty program, raising concerns about a security boundary used to contain untrusted workloads and AI agents. A bounty notification shared with the announcement shows Vercel awarding Yibelo $50,000, the program’s maximum payment for one report.
The message describes the highest award as reserved for vulnerabilities that let an attacker read or change another Vercel customer's information.
#cybersecurityawareness #cybersecuritynews

Tao Chen retweeted
Crypto Scammers Hijack Microsoft’s Official X Account * updated with statement and clarifications from Microsoft securityweek.com/crypto-scam…

