

Software Security | (De-)Obfuscation | Exploitation | Compiler | Señor Software Security Researcher
Joined December 2015
- Tweets1.5K
- Following857
- Followers586
- Likes5.7K




SektorROM retweeted

Improving MBA Deobfuscation using Equality Saturation by @fvrmatteo and @mr_phrazer.
secret.club/2022/08/08/eqsat…
SektorROM retweeted

Recon'22 slides of @p1onk's and my talk "The Mysterious Life of an Exception" are online: recon2022-exceptions.github.…! We really enjoyed @reconmtl and hope to be back one day.
SektorROM retweeted

We published the first ever blog post about HyperDbg Debugger. In this post, we explain the principles and methodologies of @HyperDbg
rayanfam.com/topics/hyperdbg…
SektorROM retweeted

In ACM @asiaccs2022, I have given a keynote speech on cellular security. More precisely, I discussed why it is difficult to secure cellular standards, networks and devices. This talk is an updated version of the keynote speech I gave at #qpss 2019.
youtube.com/watch?v=I9bUWn_x…
SektorROM retweeted

Some suggested reading for CCC:
cfallin.org/blog/2022/06/09/…
A nice write-up of the issues when designing a register allocator.
SektorROM retweeted

Flutter is rapidly gaining popularity as a framework to develop mobile apps. We investigated the current situation of reverse engineering #Flutter apps, the available tooling, and where things are headed in the future: hubs.la/Q01dh-m00
#reverseengineering #FlutterDev
SektorROM retweeted

We're excited to launch @theopenssf Fuzz Introspector, a tool targeted at helping developers identify coverage bottlenecks & writing more productive fuzzers. This is fully integrated in the OSS-Fuzz service as well, we encourage developers to try it out - openssf.org/blog/2022/06/09/…
SektorROM retweeted

Spent the past 6 months working on coverage-guided, emulation-based greybox fuzzer that makes use of a custom Just-In-Time compiler.
Blog post describing the features/implementation alongside a link to the code are listed below.
seal9055.com/blog/fuzzing/sf…
github.com/seal9055/sfuzz


SektorROM retweeted

Call for papers now open for this years CheckMATE workshop:
-> Research on offensive and defensive techniques in the context of Man At The End (MATE) attacks <-
Registration Deadline: 22.07.2022
Submission deadline: 29.07.2022
cct.lsu.edu/~checkmate/cfp.h…
Collocated with @acm_ccs
SektorROM retweeted
The slides of our @reconmtl talk on the next generation of virtualization-based obfuscators are now available. @m_u00d8 & I show how to break current VMs and why these attacks will no longer work. We also discuss the next steps in deobfuscation research.
synthesis.to/presentations/r…

SektorROM retweeted

The preprint of our IJCAI'22 paper is now available 🥳
We propose the first use constraint acquisition (symbolic ML) for program analysis 🤩
Check this out !
binsec.github.io/assets/publ…
@BinsecTool @CEA_List @lirmm_ @simula_research #MachineLearning #ArtificialInteligence #research
SektorROM retweeted

After 3 years of development, today we proudly announce & celebrate the first release of a new hypervisor-based user-mode & kernel-mode debugger, @HyperDbg. 🎉
As an alternative to #Windbg, HyperDbg is mainly built for analyzing, reversing, and fuzzing!
github.com/HyperDbg/HyperDbg

SektorROM retweeted

With the tireless work of our students, Chenbing and Ruotong, we extended our compiler-based disassembly ground truth tools to support ARM/AArch64/MIPS32/MIPS64: github.com/junxzm1990/x86-so…; Also extended the README on how the code is implemented. A USENIX'22 paper to follow -:)

SektorROM retweeted
I made a Cheat Engine-style memory scanner for /proc/mem a while back. I’ve released it! github.com/gamozolabs/mempee… Mainly just useful when attaching a debugger is too noisy.

SektorROM retweeted

Check out this awesome paper about evaluating C static analyzers led by @stephanlipp my former colleague at @tum_i4
This Post is from an account that no longer exists. Learn more
SektorROM retweeted
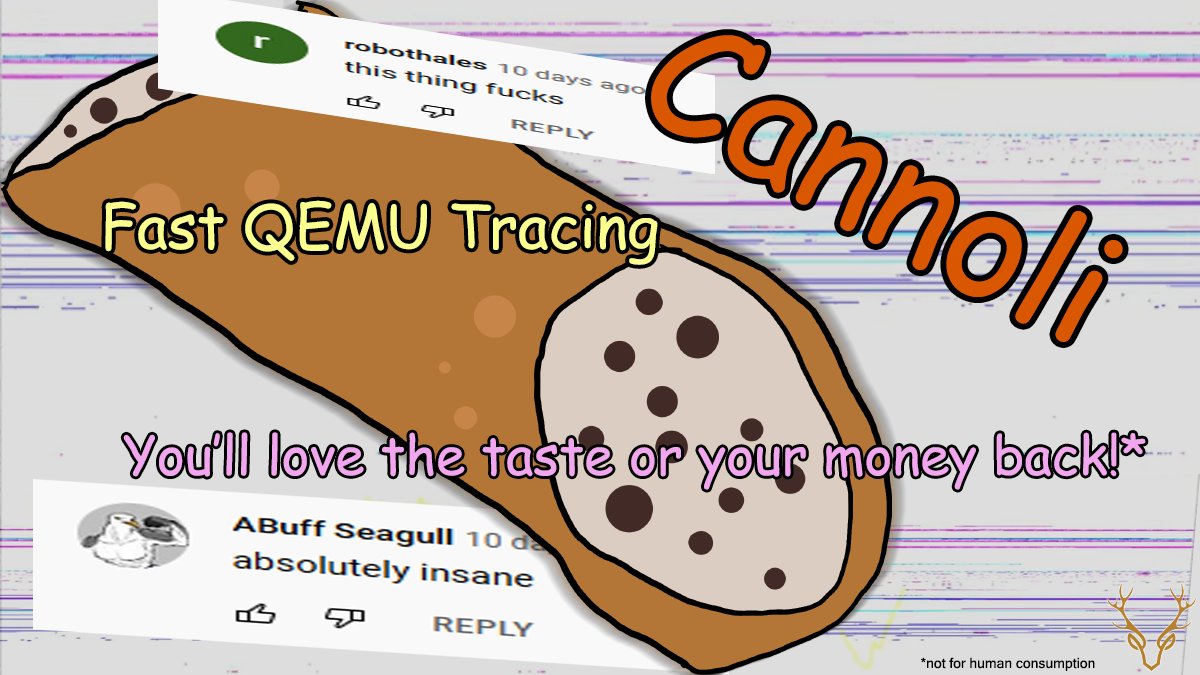
Check out my new blog and release on Cannoli. High performance tracing in QEMU!

There's always room for better performance. The fastest Qemu tracing tool by @gamozolabs.
margin.re/blog/cannoli-the-f…
SektorROM retweeted

Iwo Błądek - Machine Learning and Formal Verification
for Acquisition of Knowledge in Heuristic Program Synthesis: bip.put.poznan.pl/sites/defa…
Amazing PhD dissertation, reading it these evenings, recommended if you are interested in program synthesis.

SektorROM retweeted
Had a blast presenting together with @Digital_Cold at #CanSecWest. Here are our slides on FirmWire, our baseband emulation tool which allowed us to find several critical bugs: docs.google.com/presentation… - Lot's of practical examples on how to use parts of the framework in there!
