

We help restore trust in phone calls by making signing and verifying caller metadata with STIR/SHAKEN affordable and easy.
Seattle, WA
Joined July 2021
- Tweets115
- Following40
- Followers29
- Likes65





Pinned Tweet
June 30th is just around the corner. We can help you get compliant and stay compliant. martinisecurity.com/c/getcom…

Martini Security retweeted

The FCC proposed a $2 million penalty on a voice service provider for allegedly applying improper attestation levels on calls it originated and authenticated with STIR/SHAKEN. This notice has some lessons for other providers. Read More: transnexus.com/blog/2024/pro…

Martini Security retweeted

@SecurityMartini is, in my opinion, the best STIR/SHAKEN CA in the program. I'm proud to be both a client and an occasional contributor.

The STIR/SHAKEN ecosystem is soon transitioning to a new Certificate Policy. @SecurityMartini is still awaiting approval to begin issuing under it. With that said we remain hopeful about receiving this approval soon.
In preparation we have updated the STIR/SHAKEN Ecosystem Compliant Report (ecosystemcompliance.martinis…) and its associated tests to support these new requirements.
At this time we do not see any certificates issued under this policy. Given past adoption timelines it is hard to predict when that might happen. For example, the first CP was published in 2020, and CAs are supposed to comply with a new CP within 90 days of that. Despite this, many issuers today are still issuing certificates under the this old CP they were originally approved under.
This is noteworthy because there have been 3 other versions since then. To put a finer point on it, it has been 168 days since CP 1.4 was approved and there are no compliant certificates in use from what we can tell.
On a more positive note, it does appear that the STI-PA and PMA have been making some efforts to improve the processes as feedback is flowing more promptly now and there are subtle signs they may be taking compliance issues more seriously moving forward.
With all that said we are proud of our track record of being open, giving back to this ecosystem and being the most compliant CA within this ecosystem.

Martini Security retweeted

The STIR/SHAKEN ecosystem is soon transitioning to a new Certificate Policy. @SecurityMartini is still awaiting approval to begin issuing under it. With that said we remain hopeful about receiving this approval soon.
In preparation we have updated the STIR/SHAKEN Ecosystem Compliant Report (ecosystemcompliance.martinis…) and its associated tests to support these new requirements.
At this time we do not see any certificates issued under this policy. Given past adoption timelines it is hard to predict when that might happen. For example, the first CP was published in 2020, and CAs are supposed to comply with a new CP within 90 days of that. Despite this, many issuers today are still issuing certificates under the this old CP they were originally approved under.
This is noteworthy because there have been 3 other versions since then. To put a finer point on it, it has been 168 days since CP 1.4 was approved and there are no compliant certificates in use from what we can tell.
On a more positive note, it does appear that the STI-PA and PMA have been making some efforts to improve the processes as feedback is flowing more promptly now and there are subtle signs they may be taking compliance issues more seriously moving forward.
With all that said we are proud of our track record of being open, giving back to this ecosystem and being the most compliant CA within this ecosystem.
We have concerns about ongoing non-compliance in the CA ecosystem supporting STIR/SHAKEN. We notified the FCC and shared recommended changes. Read our notice ➡️ fcc.gov/ecfs/search/search-f… or explore the state of SHAKEN CA ecosystem ➡️ ecosystemcompliance.martinis… #STIRSHAKEN #Compliance
We are proud to have had the chance to work with @certifytheweb in their testing of this new capability!
This is fantastic! @certifytheweb has become the first general-purpose ACME client that supports STIR/SHAKEN! Now, service providers have the convenience of managing both their STIR/SHAKEN and TLS certificates through the same platform!
Martini Security retweeted

How do you leak an OEM private key for a trusted boot system. What kind of incompetence leads to that key ever being in a place where it can leak. And if that key can leak, what secret keys aren’t going to leak?


The large majority of calls received by service providers are still unsigned. All facilities based small service providers have until June 30th to get STIR/SHAKEN compliant. We can help. martinisecurity.com/solution…

Vermouth provides you everything you need to get compliant with your Traced Act obligations. martinisecurity.com/solution…

We prioritize security & compliance. No empty promises here. Our #STIR #SHAKEN services are backed by automated tech & policy automation. See our regular reports. #cybersecurity #compliance ecosystemcompliance.martinis…

🍸Meet Martini Security's complete STIR/SHAKEN & robocall solution! Quick to deploy, open source, handles certificate mgmt, call metadata signing/verification & provides robust robocall mitigation capabilities all for FREE!. 📞🔒🍸 martinisecurity.com/solution…

🌟 Discover how to to get STIR/SHAKEN compliant with Asterisk in our new white paper! . Don't wait any longer, dive in: martinisecurity.com/whitepap… #STIRSHAKEN #Asterisk #SecureCalls
🚀 Unveiling our latest white paper on achieving STIR/SHAKEN compliance with Kamailio! Master the process and ensure secure calls 📞 with our expert guidance. Ready to get started? Check it out now: martinisecurity.com/whitepap… #STIRSHAKEN #Kamailio #VoIP
Vermouth is the only Open Source STI-AS, STI-VS with built in Certificate Lifecycle Management, and both DNO, and DNC support. Most users are able to get up and running in under an hour! #SHAKENSTIR martinisecurity.com/vermouth
Just in! Martin Security's Vermouth offering now comes with basic robocall mitigation features, including call blocking and labeling for DNO and DNC enforcement. And the best part? It's all free and open source! #robocall #stirshaken #opensource martinisecurity.com/vermouth
On average each STIR/SHAKEN compliant service provider has an average of 7.50 unique unexpired certs. This suggests broad use of cert lifecycle management. We implement ACME to make this as easy as possible for service providers to roll out a reliable and vendor neutral solution.
We just published a new white paper on how to enroll for a STIR/SHAKEN using Olive. Did you know you can give us a shot for only $98? Verification only takes a few minutes and you will be up and running! martinisecurity.com/whitepap…

Have you already deployed STIR/SHAKEN? Did you know you can switch to Martini Security and up to one year free? Just show us your current certificate and we’ll add up to one year to your subscription with us! martinisecurity.com/pricing

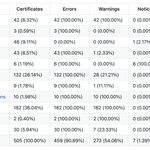
Approved CAs in the STIR/SHAKEN ecosystem are required to meet technical and policy requirements. We’ve automated testing many of these checks and run them against a large corpus of observed certificates. You can find the highlights here: ecosystemcompliance.martinis…