

Cybersecurity Enthusiast | Python Lover | PowerPoint Hero | Fiery Typist | Student at University of Dhaka
Dhaka, Bangladesh
Joined January 2013
- Tweets376
- Following473
- Followers535
- Likes7K




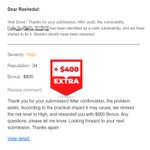


Alhamdulillah...!
#Top_2 once again on Tecno Mobile Security Response Center @TecnoSRC!
Rewarded with $7,300 including the special recognition #Diligent_Star.
"...And Allah provides for whoever He wills without limit." [Al Quran - Sura 24:38]
#bugbounty #cyber #security

1
9
779
14th June, World Blood Donor Day...!
Donated for 16 Times, Alhamdulillah...
Now a member of lifelong "Silver Club"...

1
36

I just completed module #API #Attacks in @hackthebox_eu...!
Price: $10
The last challenge will teach you once again to 'Try Harder'...
You'll learn here the OWASP Top 10 API Security Risks...
My Rating: 4.7
academy.hackthebox.com/achie…
#hackthebox #htbacademy #cybersecurity

180
PortSwigger featured my tips here portswigger.net/blog/20-burp…

4
143
Don't Use Burp Suite Like Mediocre!
Some Burp Suite Shortcuts for Your Efficient Hacking!
- Ctrl+R Send a request to the 'Repeater' tab
- Ctrl+Shift+R Jump to the 'Repeater' tab
- Ctrl+Space Send the request to the server from the 'Repeater' tab
- Ctrl+U URL Encode your input

1
18
885
Some people keep learning bugs but they don't apply the methods in real world web applications to exploit such vulnerabilities...
For example, you just completed a Race condition lab from Portswigger, go for exploiting this vulnerability in a bug bounty website...
3
253
2/2
2. Keep reading disclosed reports from hackerone.com/hacktivity/
3. In the next two months, whenever you start using a browser, always intercept all traffic through Burp.
4. Don't fall into the learning loop, start hacking today!
14
647
Don't Start Web Hacking Now, Begin from YESTERDAY!
Get Ready for Bug Bounty in Just 4 Steps:
1. Start learning from portswigger.net/web-security by selecting a particular bug type e.g. Broken Access Control
1/2
#infosec #bugbounty #tips #ethicalhacking #infosecurity #whitehat

What an insight! @NahamSec
"When I can't find bugs, I change perspective not targets.
Client-side -> API Issues
Main App -> Developer Platform"
"Give Me 13 Minutes and 2025 Will Be Your Best Bug Bounty Year"
YouTube Link: youtube.com/watch?v=PER6Nvr6…

Alhamdulillah!
Awarded with $600 for finding an IDOR vulnerability!
Context:
- The Web App was letting users to upload payment screenshots if they chose 'Bank Transfer' method for boosting their posts.
- But abusing the IDOR vulnerability, I could upload/replace victims' images.

2/2
Replace the image link with an XSS payload like...
POST /comment HTTP/1.1
Host: example.com
commentText=Nice&imageLink=example.com/img/not_exists.j…" onerror=confirm(1337) onerror=confirm(1338)
NB. Don't forget to use 'onerror' event double time.

5
Secrets:
1/2
If you see, your uploaded image generated a URL and getting passed immediately with another HTTP request like below
POST /comment HTTP/1.1
Host: example.com
commentText=Nice&imageLink=example.com/img/123.jpg

9